

Turn every policy into automated workflows with built-in enforcement and audit-ready proof.


What Is Compliance Operations? The Complete Guide
Compliance operations is the discipline of turning compliance requirements into the way work actually runs. It connects obligations and policies to controls, owners, workflows, approvals, evidence, exceptions, and review. The result is a system that guides compliant action while the work is happening and preserves proof of what happened.
The practical test is simple: can the organization show that the right person completed the right control, at the right time, using the right evidence, and that any deviation was found and resolved? If the answer depends on chasing screenshots and rebuilding a timeline before an audit, compliance is documented but not fully operationalized.
In this guide:
- What is compliance operations?
- Why does compliance operations matter?
- How is it different from compliance management and GRC?
- What are the core components?
- How does compliance operations work?
- What does it look like in practice?
- How do you build compliance operations?
- Who owns compliance operations?
- Which metrics show it is working?
- How should AI fit into compliance operations?
- How does Process Street support compliance operations?
- Frequently asked questions
What is compliance operations?
Compliance operations is an operating model for embedding legal, regulatory, contractual, industry, and internal requirements into everyday business processes. It translates a requirement into a control, gives that control an owner, places it inside a repeatable workflow, defines the evidence that proves completion, and creates a route for exceptions and corrective action.
It is broader than audit preparation. Audits inspect a period of activity. Compliance operations shapes the activity itself. A strong system can prevent an incomplete request from advancing, require a qualified approver, calculate a due date, collect a file, escalate a missed step, record a decision, and preserve the history for later review.
Compliance operations also connects the people who set requirements with the people who perform the work. Compliance specialists interpret obligations. Process owners design how the requirement will be met. Operators complete the control. Managers review exceptions. Internal audit tests whether the system is designed and operating effectively.
Why does compliance operations matter?
Policies can be accurate and still fail in practice. A requirement may live in a policy library while the operating team uses an email thread, spreadsheet, or improvised checklist. That gap creates skipped approvals, inconsistent evidence, unclear ownership, and late remediation. Compliance operations closes the gap by putting control logic inside the path of execution.
This is also how external evaluators tend to think about effectiveness. The U.S. Department of Justice guidance on evaluating corporate compliance programs asks whether a program is well designed, adequately resourced and empowered, and effective in practice. It specifically examines whether policies are integrated into operations, whether gatekeepers know how to escalate concerns, and whether the program improves when problems reveal weaknesses.
- Prevention: Required fields, permissions, approvals, and stop conditions make obvious violations harder to complete.
- Detection: Monitoring and exception routes reveal late, missing, unusual, or rejected activity while action is still possible.
- Proof: The execution record preserves owners, timestamps, decisions, evidence, and changes in context.
- Learning: Findings and exceptions feed into policy, control, training, and workflow changes.
- Scale: Repeatable processes keep control quality consistent across teams, locations, and growing volumes.
How is compliance operations different from compliance management and GRC?
Compliance operations, compliance management, and governance, risk, and compliance are related layers, not mutually exclusive categories. The useful distinction is the job each layer performs.
| Discipline | Primary job | Typical artifacts | Core question |
|---|---|---|---|
| Compliance management | Define and govern the compliance program | Obligations, policies, risk assessments, training, reporting | What must the organization do, and how will the program be governed? |
| Compliance operations | Execute controls in recurring work | Workflows, assignments, approvals, evidence, exceptions, remediation | Did the required control happen correctly in this case? |
| GRC | Connect governance, risk, controls, and assurance at enterprise scale | Risk registers, control libraries, frameworks, issues, audits | How do risks, controls, obligations, and assurance relate across the organization? |
A compliance management system provides the governing structure. ISO 37301 describes establishing, developing, implementing, evaluating, maintaining, and improving an effective and responsive compliance management system. Compliance operations is where that intent becomes executable work, measurable control performance, and evidence.
GRC platforms can provide a valuable system of record for requirements, risks, controls, issues, and audits. They do not automatically become the place where a hiring manager verifies an identity document, a finance reviewer approves a reconciliation, or an access owner completes a quarterly review. Compliance operations connects the system of record to the system of action.
What are the core components of compliance operations?
A durable program forms a closed loop. Governance defines the standard. Execution applies it. Oversight tests results. Improvement changes the system when evidence shows a weakness.
Policy-to-control map
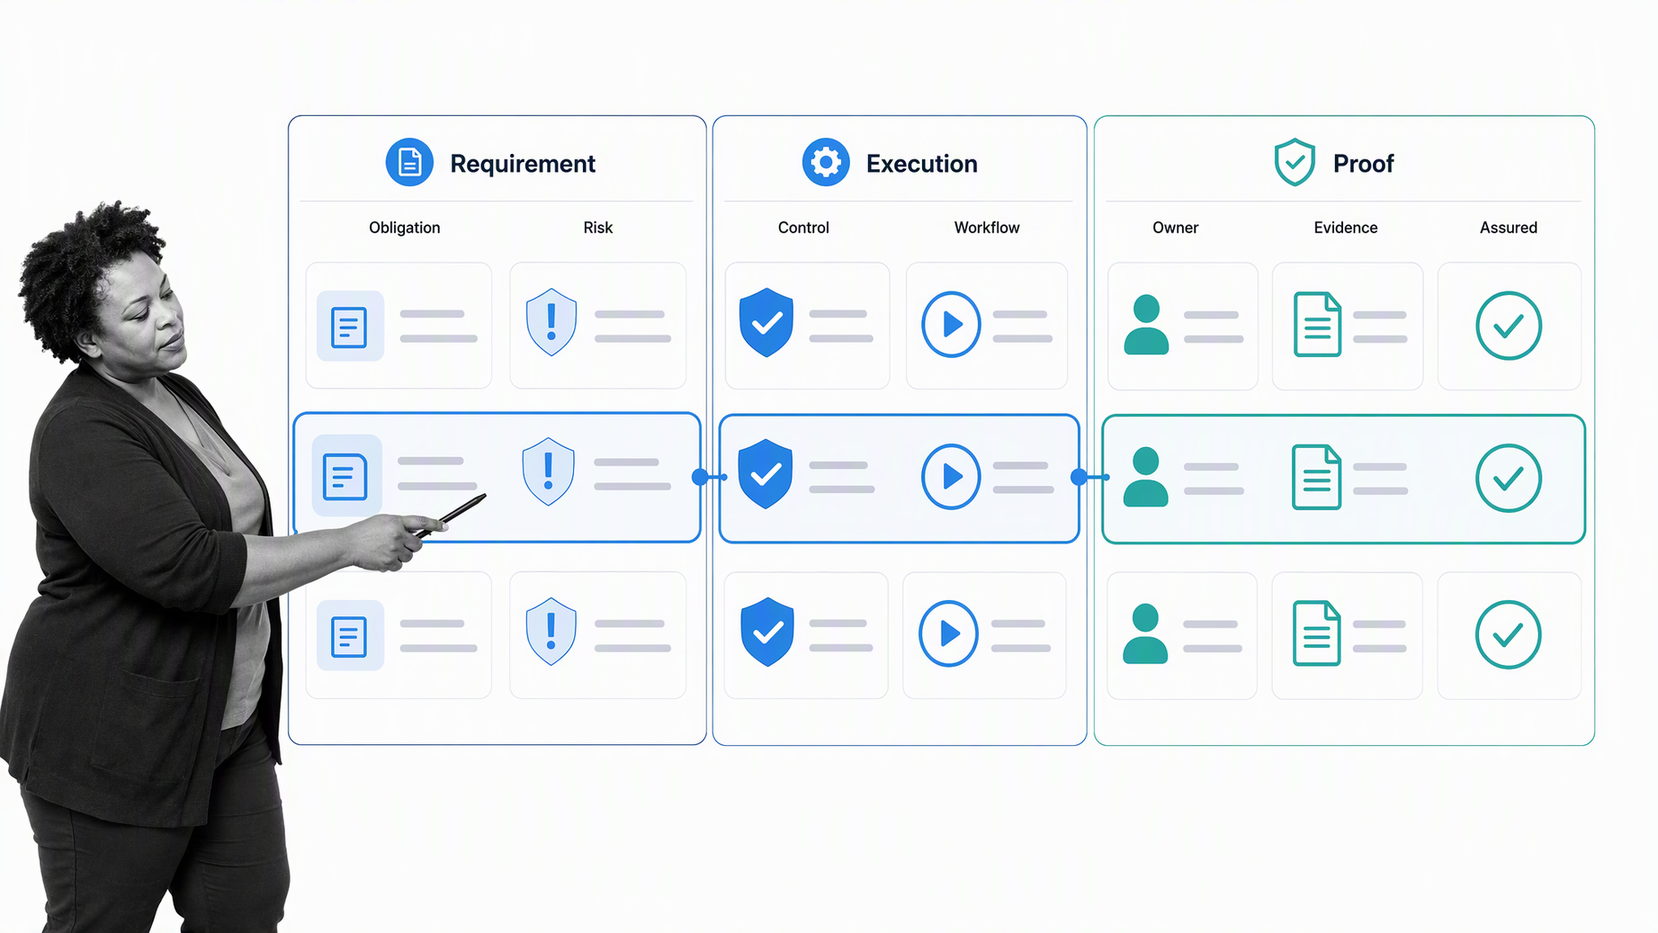
Start with traceability. Each material obligation should connect to one or more policies, controls, processes, owners, evidence requirements, and review activities. The map prevents two common failures: requirements with no operating control and controls that consume effort without a clear requirement or risk behind them.
- Obligation: The legal, regulatory, contractual, standard, or internal requirement.
- Risk: The event or condition the organization is trying to prevent, detect, or correct.
- Control: The action or condition that changes the likelihood or impact of that risk.
- Workflow: The sequence, ownership, decisions, and timing through which the control operates.
- Evidence: The record that shows the control was performed and reviewed.
- Assurance: The test that determines whether the control is appropriately designed and working.
Controlled policies and procedures
Policies need owners, approval, version history, review dates, and a clear relationship to the procedures that implement them. Operators should see the instruction relevant to the task they are performing, not search a library and decide which paragraph applies.
Executable workflows
A workflow turns a control statement into behavior. It defines triggers, inputs, required steps, responsible roles, decision rights, conditions, due dates, evidence, and completion criteria. High-risk paths may require additional review, while routine cases can move through a lighter route.
Evidence and record integrity
Evidence should be created or captured at the point of work. Strong evidence is attributable, time-bound, complete, protected from inappropriate change, and connected to the requirement and case it supports. A screenshot saved later may be useful, but it is weaker than a record generated by the workflow that contains the decision, actor, time, and supporting input.
Monitoring, exceptions, and improvement
A program needs thresholds and signals that show when work is late, incomplete, inconsistent, or outside policy. Exceptions require an owner, severity, due date, decision, remediation plan, and closure evidence. Trends from exceptions, testing, incidents, and audit findings should change the control design rather than remain in a report.
How does compliance operations work?
The operating cycle begins before a task is assigned and continues after it is completed. Each stage should produce a usable output for the next one.
- Identify obligations and risks. Define the requirement, affected process, risk scenario, scope, and responsible business area.
- Design the control. Decide whether the control is preventive, detective, corrective, or a combination. Set the frequency, owner, reviewer, evidence, and success criteria.
- Build the operating workflow. Translate the control into tasks, forms, rules, approvals, due dates, integrations, exception paths, and escalation logic.
- Run the work. Assign the case to the right participants, present the applicable instructions, and capture decisions and evidence as they occur.
- Monitor performance. Watch completion, timeliness, exceptions, overrides, evidence quality, and control outcomes.
- Test and assure. Sample or continuously assess whether the control is designed appropriately and operating as intended.
- Remediate and improve. Resolve the individual issue, identify the cause, and update the policy, control, workflow, training, or system when necessary.
Controlled compliance workflow
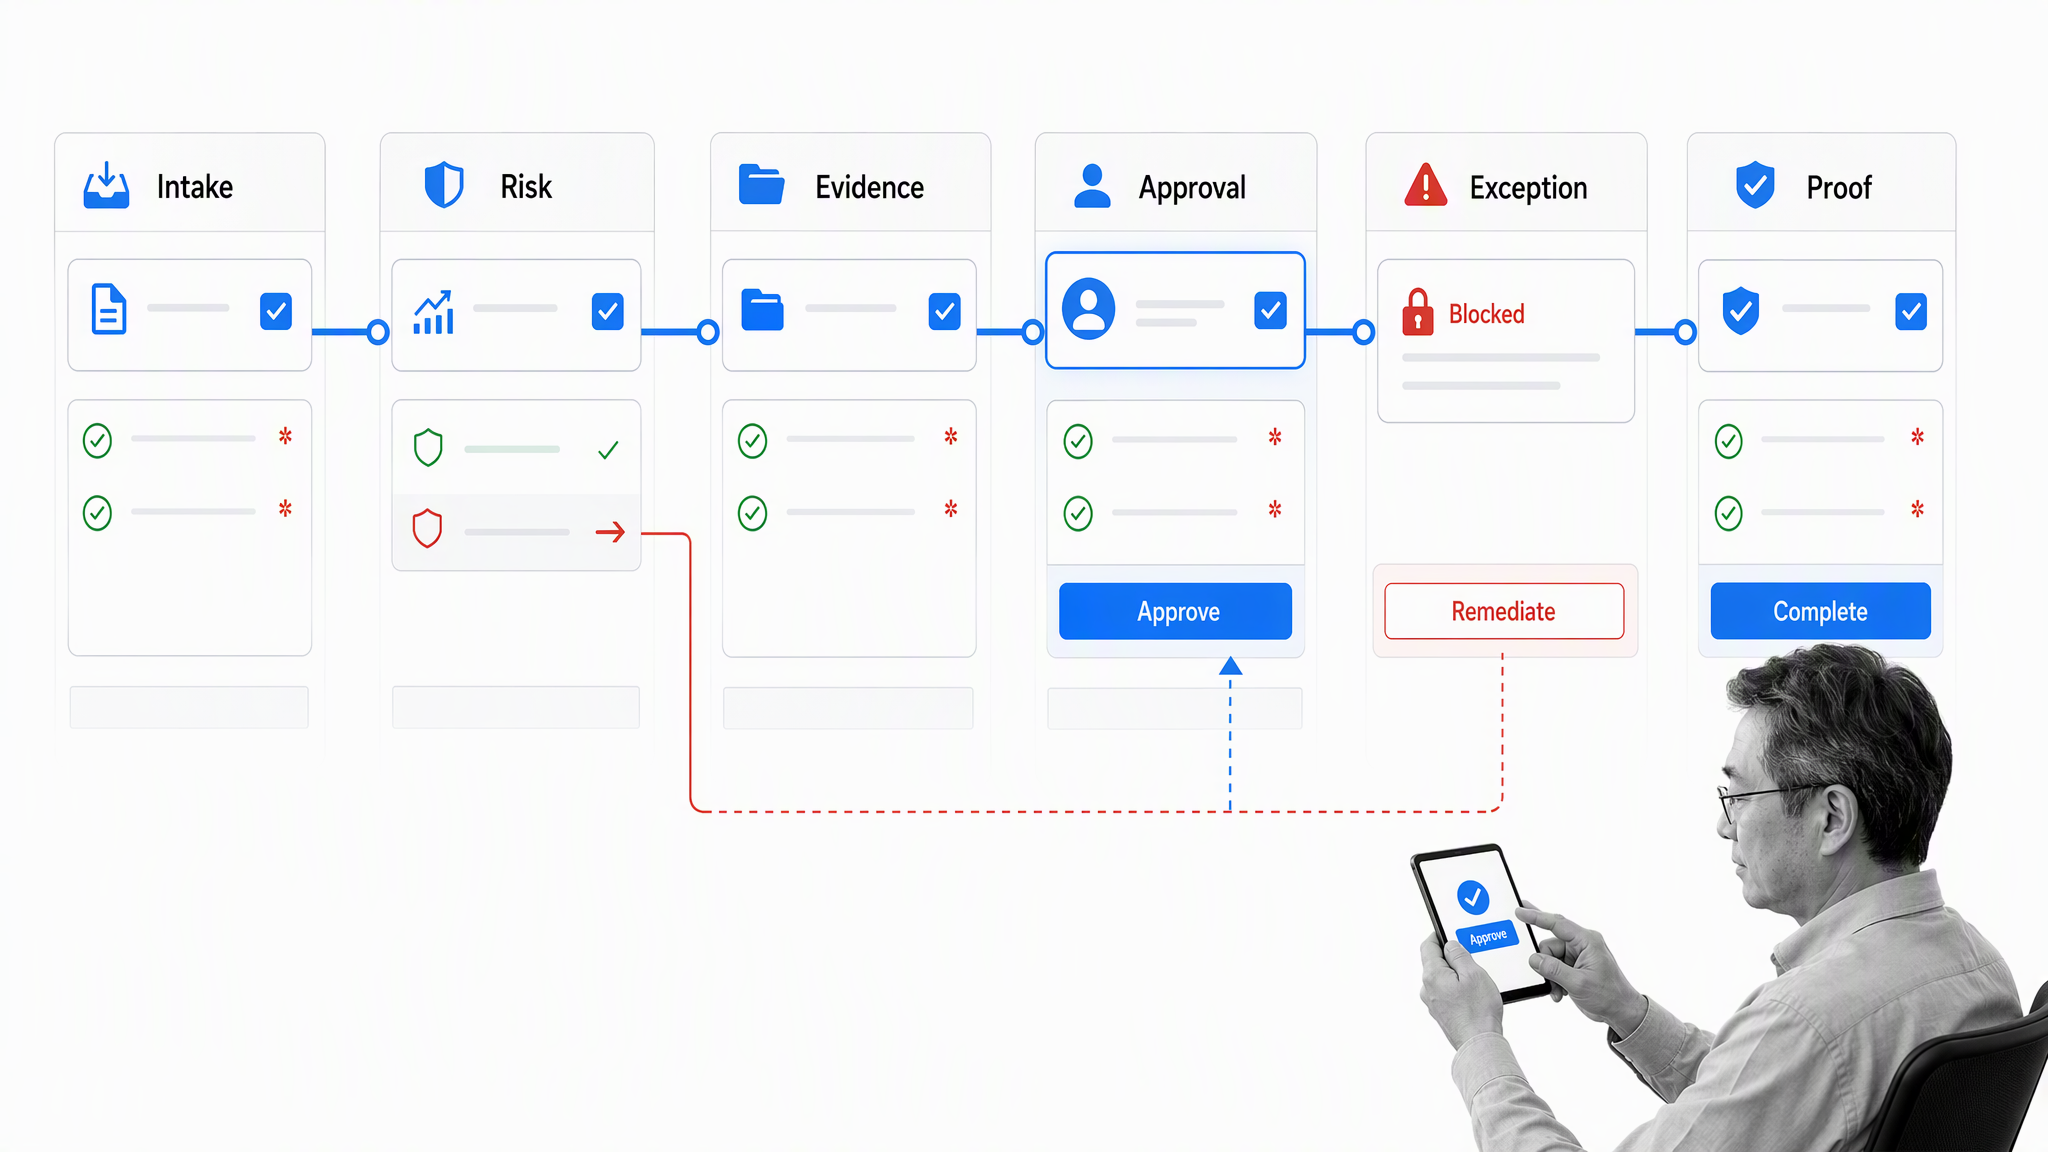
A controlled workflow makes the compliant path explicit. It starts from a defined trigger, uses risk or case data to select the route, requires the correct participants, blocks progress when a mandatory condition is missing, and retains a complete execution record. For a deeper design pattern, see workflow automation compliance.
Exception and remediation queue
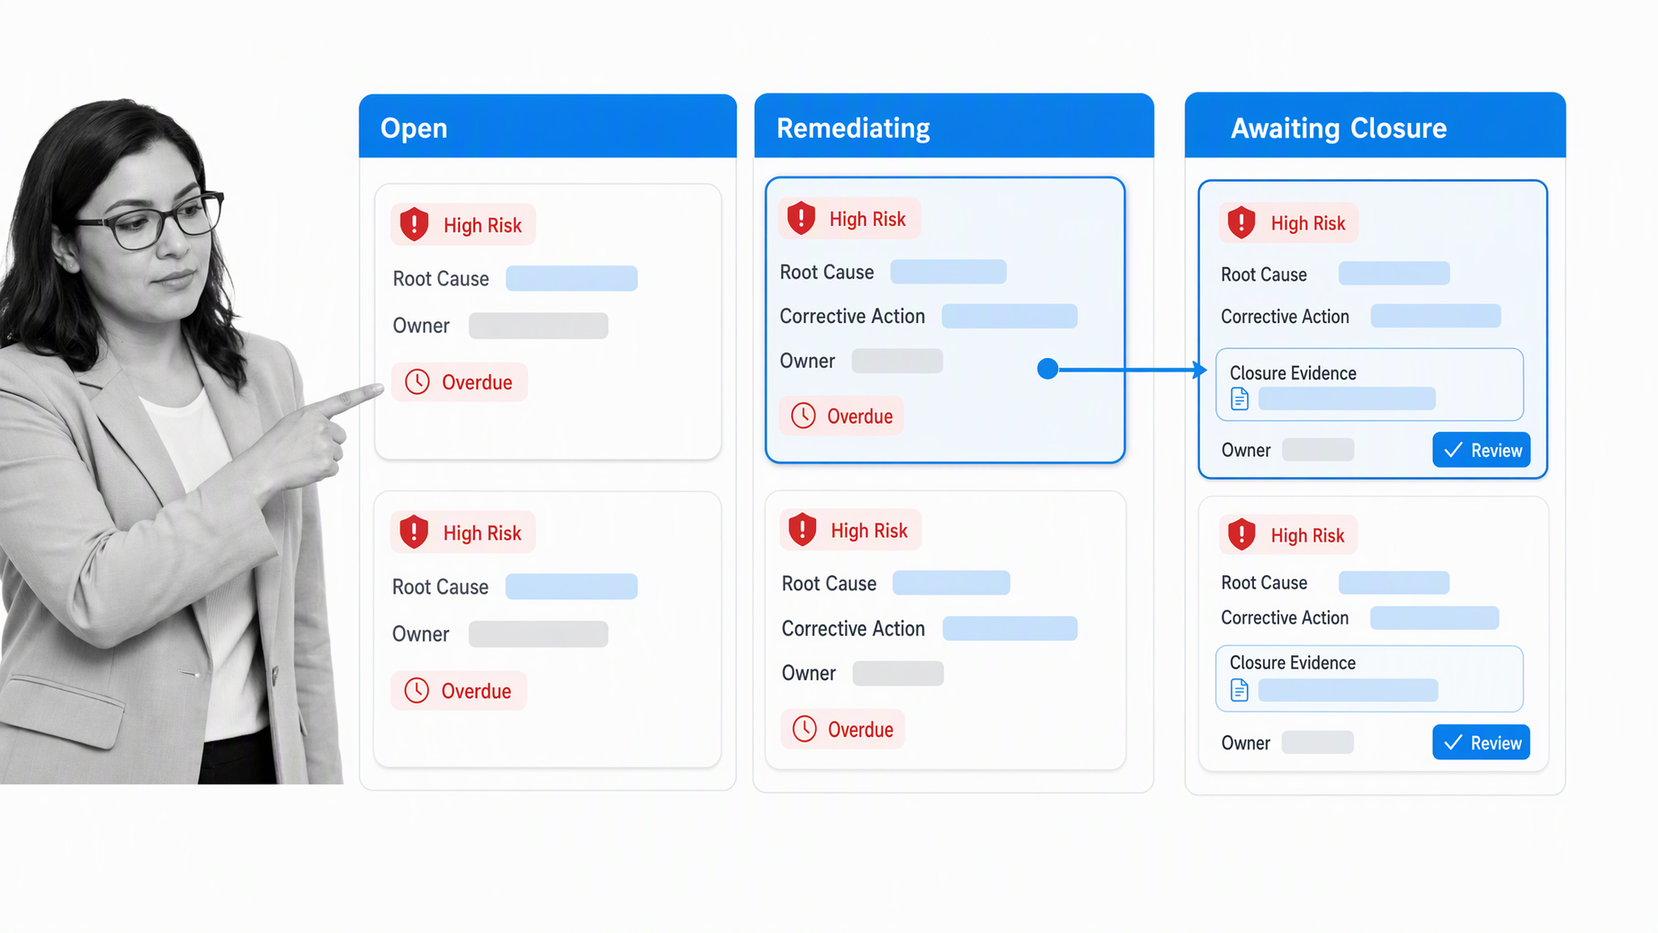
Exceptions should not disappear into email. A structured queue records the affected control, risk, severity, owner, immediate response, root cause, remediation, target date, reviewer, and closure evidence. The queue gives leaders a truthful view of control health and creates the feedback needed to prevent recurrence.
What does compliance operations look like in practice?
Employee onboarding
The workflow can require identity and eligibility steps, security training, policy acknowledgment, equipment records, access approvals, and role-specific controls. Conditional paths add requirements for location, department, access level, or worker type. The record shows which controls applied and who completed them.
Financial close and reporting
Reconciliations, journal review, supporting files, segregation of duties, variance investigation, certification, and signoff can be coordinated in one close process. Exceptions route to accountable reviewers, while timestamps and approval history preserve the sequence of decisions.
Access review
A scheduled review can distribute user and entitlement records to application owners, require a retain or remove decision, route privileged access for additional approval, and track remediation to closure. The workflow separates review completion from the actual removal of access so both actions are proven.
Third-party due diligence
Vendor intake captures the service, data, access, geography, criticality, and business owner. Risk indicators determine which security, privacy, legal, finance, and compliance reviews apply. The decision, conditions, contract evidence, reassessment date, and unresolved issues remain attached to the relationship.
Healthcare access and privacy
Requests for access to sensitive information can require a valid purpose, role approval, least-privilege review, training status, and periodic recertification. Monitoring can detect overdue review, unusual access, or missing evidence and create an investigation route before the next audit cycle.
How do you build compliance operations?
Do not begin by automating every policy. Start with one process where errors carry real consequences, the work repeats often enough to measure, and ownership is identifiable. A focused pilot reveals whether the organization can connect the requirement, workflow, evidence, exception, and review end to end.
- Choose a high-value process and define its start and end.
- List the obligations, risks, controls, systems, participants, and evidence involved.
- Walk real cases, including a rejected approval, missing evidence, late task, policy exception, and failed integration.
- Assign one accountable owner for the process and one owner for each control activity.
- Build the smallest workflow that enforces the required path and makes exceptions visible.
- Test with operators, compliance, security, legal, and internal audit as applicable.
- Measure completion, timeliness, exceptions, evidence quality, rework, and control outcomes.
- Improve the design, then expand to adjacent processes that reuse owners, evidence, or controls.
A workflow is ready when participants can run it without side instructions, reviewers can understand the decision in context, and assurance teams can trace the result back to the requirement. If the happy path works but exceptions still leave the system, the process is not finished.
Who owns compliance operations?
Compliance operations is cross-functional, but shared work should not mean shared ambiguity. Operating teams own the controls embedded in their processes. Compliance and risk functions define requirements, advise, monitor, and challenge. Internal audit maintains the independence needed to provide objective assurance.
The Institute of Internal Auditors Three Lines Model provides a useful role structure: management runs operations and manages risk, specialist functions support and monitor risk-related matters, and internal audit provides independent assurance. The exact organization varies, but decision rights and escalation paths should be explicit.
| Role | Operational responsibility |
|---|---|
| Governing body and executives | Set expectations, risk appetite, authority, resources, and oversight |
| Process owner | Own the end-to-end process, performance, control integration, and improvement |
| Control owner | Ensure a specific control is designed, performed, evidenced, and reviewed |
| Operators and approvers | Complete the work, make accountable decisions, and raise exceptions |
| Compliance and risk | Interpret requirements, advise, monitor, challenge, and report |
| Internal audit | Provide independent assurance on design and operating effectiveness |
Which metrics show compliance operations is working?
Count activity, but do not confuse activity with effectiveness. Training completions, policies published, and controls scheduled are inputs. The stronger measures show whether controls ran on time, detected problems, produced usable evidence, and improved after exceptions.
- Control completion: Percentage of required control activities completed by the due date.
- Evidence quality: Percentage of sampled records that are complete, attributable, current, and traceable.
- Exception rate: Number and severity of deviations by process, control, business unit, and cause.
- Time to detect: Time between the deviation and its identification.
- Time to remediate: Time from issue creation to verified closure, segmented by severity.
- Repeat findings: Issues that recur after corrective action, a signal that remediation did not address the cause.
- Override rate: Frequency, justification, approval, and outcome of control overrides.
- Workflow rework: Cases returned because data, evidence, or approval was incomplete.
- Assurance results: Control design and operating-effectiveness findings from testing and audit.
Use metrics to improve the operating system, not to manufacture a clean dashboard. A rising exception rate can mean the process is deteriorating, or it can mean detection has improved. Pair each metric with context, trend, severity, and a decision about what changes next.
How should AI fit into compliance operations?
AI can classify requests, extract data, compare evidence with policy, prepare summaries, recommend routes, and identify unusual patterns. The process around the model determines whether those actions are governable. Give the agent a bounded task, approved context, permitted tools, validation criteria, and a clear stop condition.
Consequential actions should include human review where risk, uncertainty, or policy requires it. Preserve the inputs, output, decision, approver, exception, and downstream action. Monitor quality and drift, and provide a fallback when the model is unavailable or confidence is insufficient. Agentic process automation combines adaptive AI action with stable workflow controls, permissions, approvals, exception paths, and evidence.
The same principle applies to people and agents: authority should be explicit, required controls should not drift, and completion should leave a reviewable record. Automation is valuable when it strengthens the control environment, not when it hides decisions inside an opaque system.
How does Process Street support compliance operations?
Governed workflow execution in Process Street
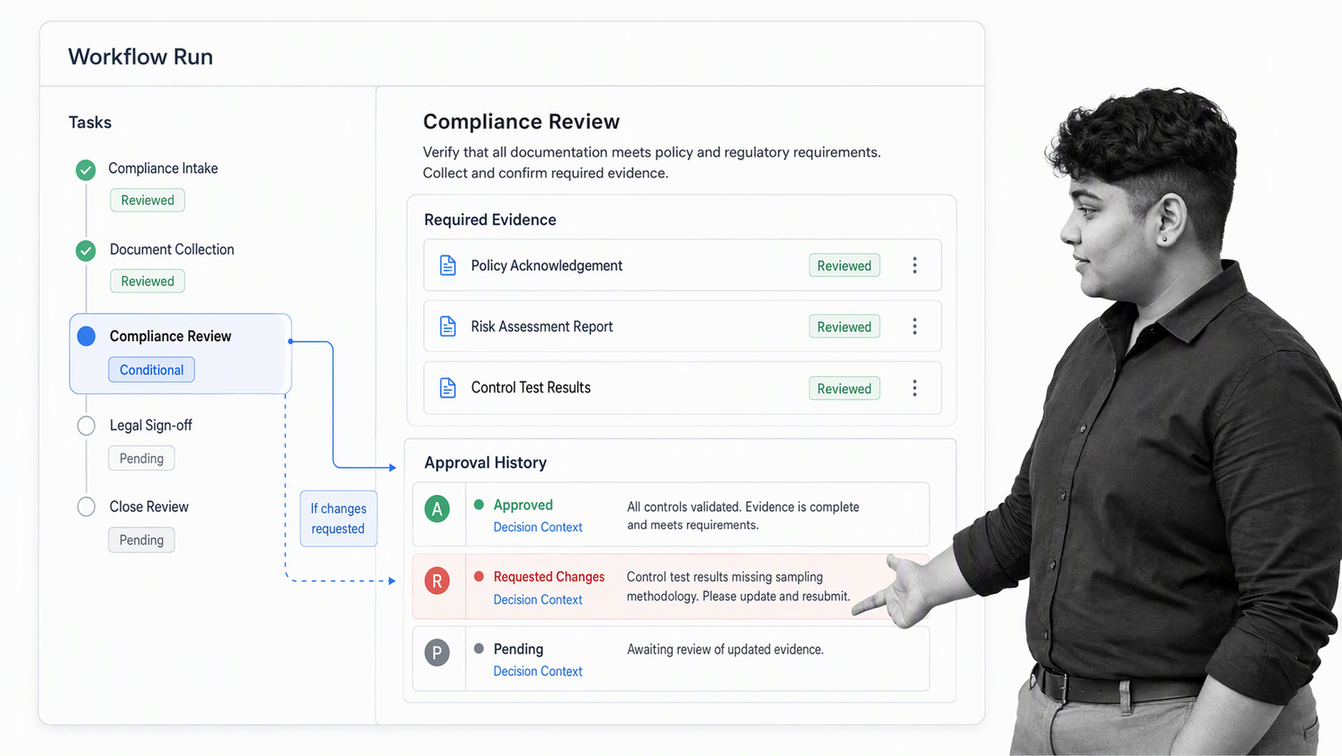
Process Street is an agentic process automation platform for high-stakes operations. Teams can turn policies and procedures into workflows with tasks, instructions, forms, assignments, due dates, conditional logic, approvals, automations, AI tasks, stop tasks, and evidence. Each workflow run carries the specific case, decisions, comments, files, and completion history through the operating path.
That structure supports the core compliance operations loop. The process defines what should happen. Required fields and decision gates guide execution. Conditional paths apply the right control to the case. Approvals keep accountable judgment in context. Exceptions remain visible. The run history becomes proof of what happened. Process owners can then improve the workflow using evidence from real execution.
Approval records can include approvals and rejections, comments, form-field changes, and files included with the request, as described in the Process Street approval history documentation. For the broader evidence model, see compliance as proof of control. Teams evaluating the execution layer can also review how business process software connects recurring work, control, and history.
The goal is not to move every compliance artifact into one tool. Keep authoritative records in the systems designed to own them. Use the workflow as the control layer that coordinates people, systems, and agents, enforces the required path, and keeps responsibility and proof connected from request to completion.
Frequently asked questions
What is compliance operations?
Compliance operations is the operating discipline that turns obligations, policies, and controls into assigned workflows, required decisions, evidence, exception handling, and review. It makes compliance part of daily execution rather than a separate audit-preparation activity.
What is the difference between compliance operations and compliance management?
Compliance management defines and governs the program: obligations, policies, risk assessments, training, reporting, and oversight. Compliance operations is the execution layer that makes those requirements happen in recurring work and records the proof. Effective organizations need both.
What are the core components of compliance operations?
The core components are an obligation and risk inventory, controlled policies, mapped controls, executable workflows, clear ownership, evidence captured during work, exception and remediation paths, monitoring, independent assurance, and a feedback loop for improvement.
How does compliance operations improve audit readiness?
It keeps owners, approvals, timestamps, files, decisions, and exceptions attached to the work that produced them. Auditors can trace a requirement to a control, a control to a workflow, and a workflow to evidence without relying on a last-minute reconstruction project.
Who owns compliance operations?
Business and operations leaders own the controls inside their work. Compliance and risk teams define requirements, advise, challenge, and monitor. Internal audit provides independent assurance. A named program owner coordinates the system, but operating responsibility stays with the people who run the process.
Can AI be used in compliance operations?
Yes, when AI acts inside a governed process. Give it bounded tasks, approved context, permitted tools, validation rules, and human approval for consequential actions. Retain inputs, outputs, decisions, exceptions, and overrides so the organization can review how the result was produced.