Note: SSO is available on our Enterprise plan. If you are interested in enabling SSO for your company, contact our support team, or your Account Executive.
Set up the ADFS Relying Party Trust with the SAML 2.0 protocol. Process Street’s sign-in service supports SAML 2.0 only, not WS-Federation. You need two values from Process Street: the Entity ID and the ACS URL.
Once our team has turned on SSO for your organization, go to Organization Settings, open the Settings tab, and find Service provider details in the Single sign-on section. Copy the following values and use them when configuring your ADFS trust:
When you ask our team to turn on SSO, send them the domain(s) your company will use to sign in, for example company.com or company-info.com.
Then, in the Identity provider part of the Single sign-on section, enter your ADFS Sign-In URL, click Upload certificate to add your ADFS token-signing certificate, and click Set up SSO.
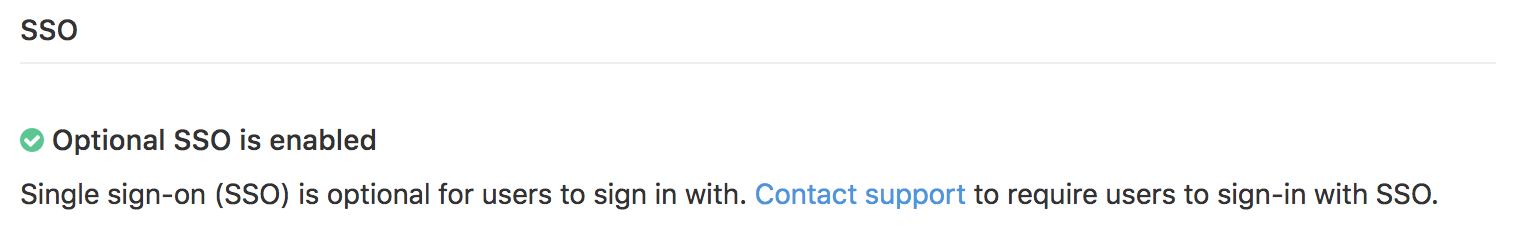
Once it’s set up, test your SSO connection as an optional sign-in method before switching to Required SSO.
You will see this setting under the Settings tab:
After you’ve tested your connection, our team will run a check to ensure your organization can be locked to SSO. They will check that your users do not have any:
They will work with you to fix these issues.
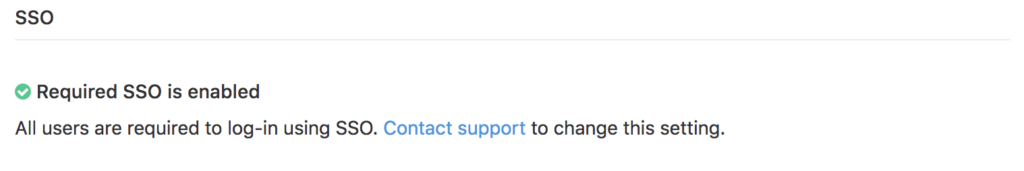
Once any issues are fixed, you can switch SSO sign-in to Required in the Single sign-on section. At this point, all users within your company will be required to sign in with SSO.
You will see this setting under the Settings tab:
Help us improve this help center.