Note: SSO is available on our Enterprise plan. If you are interested in enabling SSO for your company, contact our support team, or your Account Executive.
There are three steps to set-up the Okta SSO connection:
- Set-up Okta Application.
- Enter identity provider details in Process Street.
- Verify Okta SSO is working properly.
Step 1: Set-up Okta Application
- On the general Okta dashboard, click Admin. This takes you to the Okta Admin Dashboard.

- Using the list of shortcuts at the right-hand side of the page, click Add Applications.
- On the Add Application page, select Create New App button.

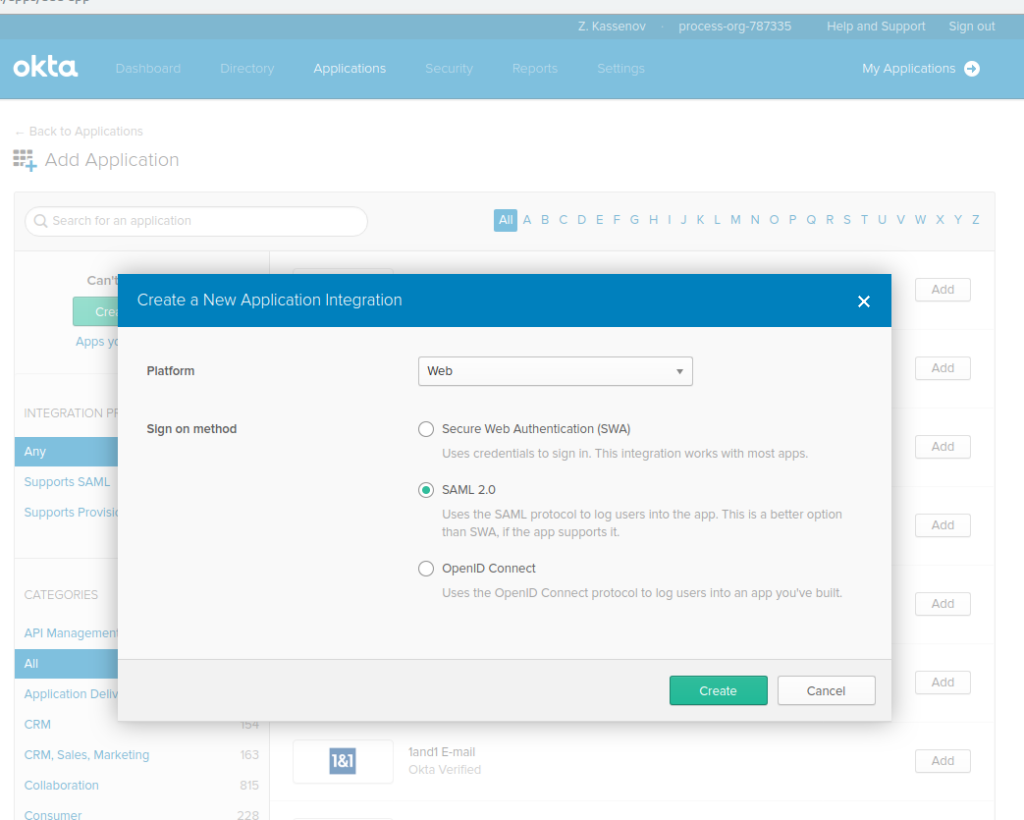
- On the Create a New Application Integration pop-up window, select Web as the Platform for your application and choose SAML 2.0 as the Sign on method. Click Create to proceed.
- You will now create your SAML integration. On the General Settings page, provide the following:
- App name: Process Street;
- App logo (optional);
- App visibility: select whether you want your users to see your application icon and in what settings. Click Next to proceed.

- Next, you will see the SAML Settings page. To fill in these fields, go to Organization Settings in Process Street, open the Settings tab, and find Service provider details in the Single sign-on section. Copy the values into Okta:
- Single sign-on URL: Paste the ACS URL from your Process Street SSO settings.
- Audience URI (SP Entity ID): Paste the Entity ID from your Process Street SSO settings.
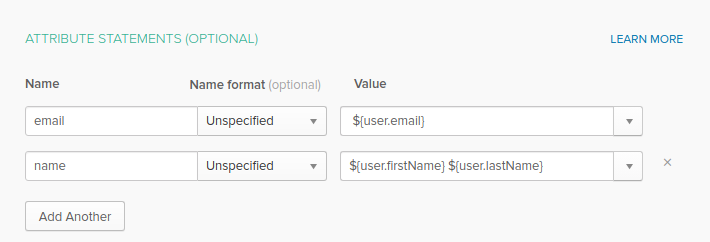
- You will also need to add the following Attribute Statement:
- Name: name
- Name format (optional): ${user.firstName} ${user.lastName}
- Value: ${user.email}
Click Next to proceed.
- Lastly, answer Are you a customer or partner? by selecting I’m an Okta customer adding an internal app. Click Finish.
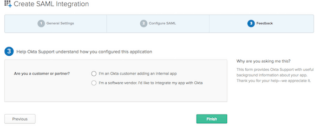
- You’ll be directed to the Sign On page for your newly-created app. Click on View Setup Instructions to complete the process.
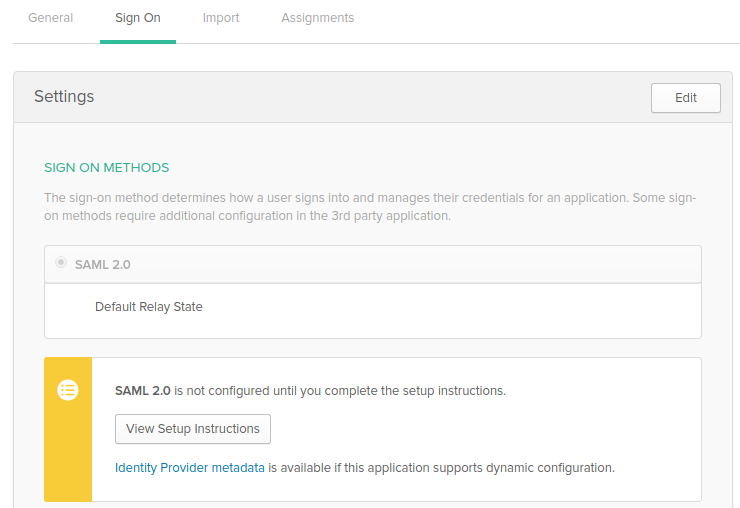
Step 2: Enter identity provider details in Process Street
Take note of the Identity Provider Single Sign-On URL and download a copy of the X.509 certificate from the Okta setup instructions page.
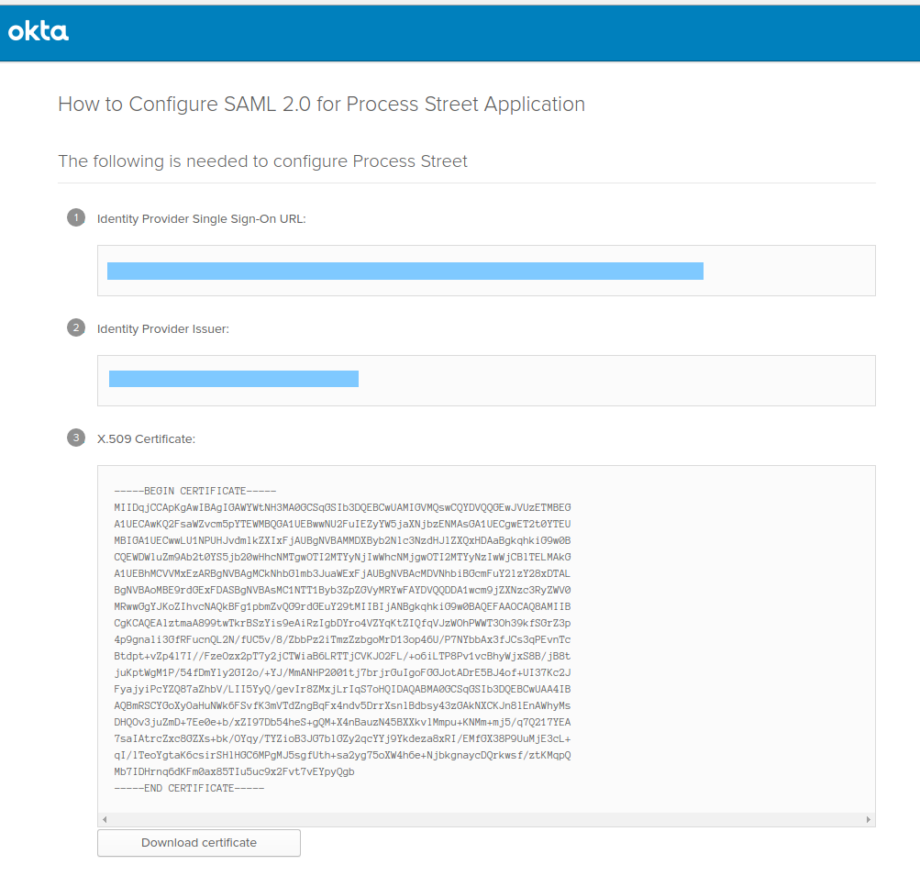
Then enter these details in Process Street:
- In Process Street, go to Organization Settings, open the Settings tab, and scroll to the Single sign-on section.
- In the Identity provider section, paste the Sign-In URL from Okta.
- Click Upload certificate and choose the X.509 certificate file.
- Click Set up SSO.
After entering the identity provider details, go back to Okta and assign the application to people or groups.
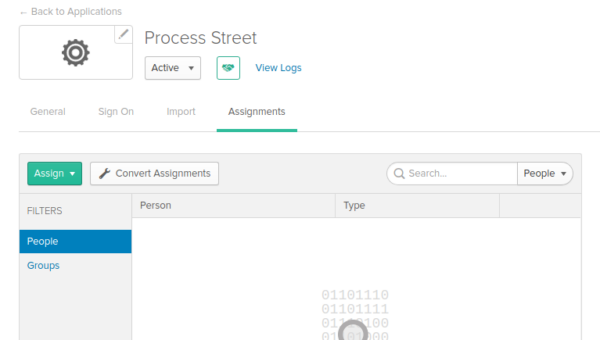
Step 3: Verify SSO is working
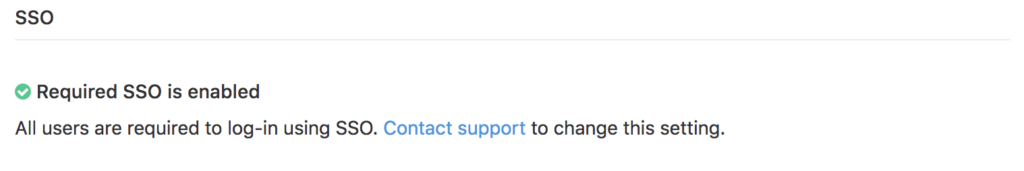
SSO starts as optional, so users can still sign in with a password while you test it. Once it works, switch SSO sign-in to Required in the Single sign-on section. At that point, all users within your company will be required to sign in with SSO.
You will see this setting under the Settings tab.