

Bad processes are workflows whose incentives, ownership, controls, or feedback loops allow the wrong action to become the easiest action. They create more than inefficiency. In regulated work, a broken process can expose customers, employees, and the business itself to harm.
Zenefits became a vivid example. After co-founder Parker Conrad promised insurance brokers in 2013 that the company would “drink your milkshake,” rapid growth made the company a Silicon Valley favorite. By February 2016, Conrad had resigned as investigations exposed licensing and training failures. The episode shows what happens when growth targets move faster than risk controls.
By 2016, Zenefits was eating its own words, or drinking them, to use Conrad’s language.
Conrad stepped down in February 2016 after investigative reports detailed how the company flouted insurance laws and helped brokers cheat on the licensing process.
When PayPal mafia veteran and Yammer founder David Sacks took over, he made it clear that there was one reason for Parker’s resignation: rotten internal processes. As he said in a post on the company blog, “Many of our internal processes, controls, and actions around compliance have been inadequate, and some decisions have just been plain wrong. As a result, Parker has resigned.”
The failure was not one isolated mistake. Growth incentives, licensing controls, training, and accountability reinforced one another. Here are the three process management mistakes they made, and how your startup can avoid them.
Growth outpaced risk controls
Parker Conrad set aggressive hiring and sales goals from the company’s early days. The targets changed quickly, but the controls needed to support them did not.
Growth accelerated after Lars Dalgaard, then a general partner at Andreessen Horowitz, invested. The pressure was clear: build a much larger sales organization, fast. So they set out for hypergrowth. But even though their goals and key metrics changed, their processes did not, which was mistake number one.
The Zenefits sales machine and its lack of process
Once they set their eyes on such large figures, they needed to put processes in place that would help them get there. For one, they needed more sales development reps (SDRs), so they decided to hire aggressively in Phoenix, a less expensive market.
As Conrad said in 2013, “Today we know we can hire 1 SDR that’s gonna create x leads that will feed x reps. So we can push that as hard as we can. It’s really just a machine today, so it’s just about how aggressively we can scale without the wheels falling off the track.”
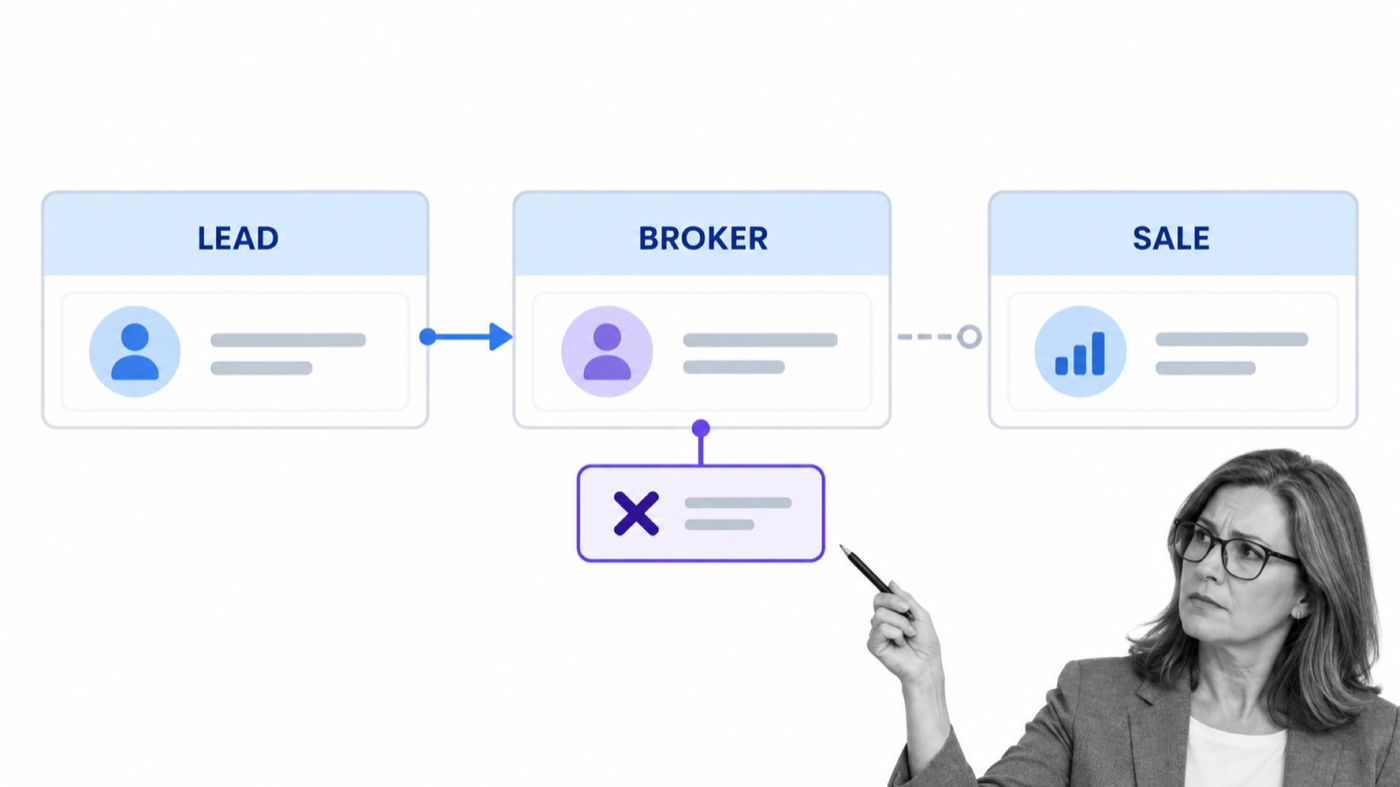
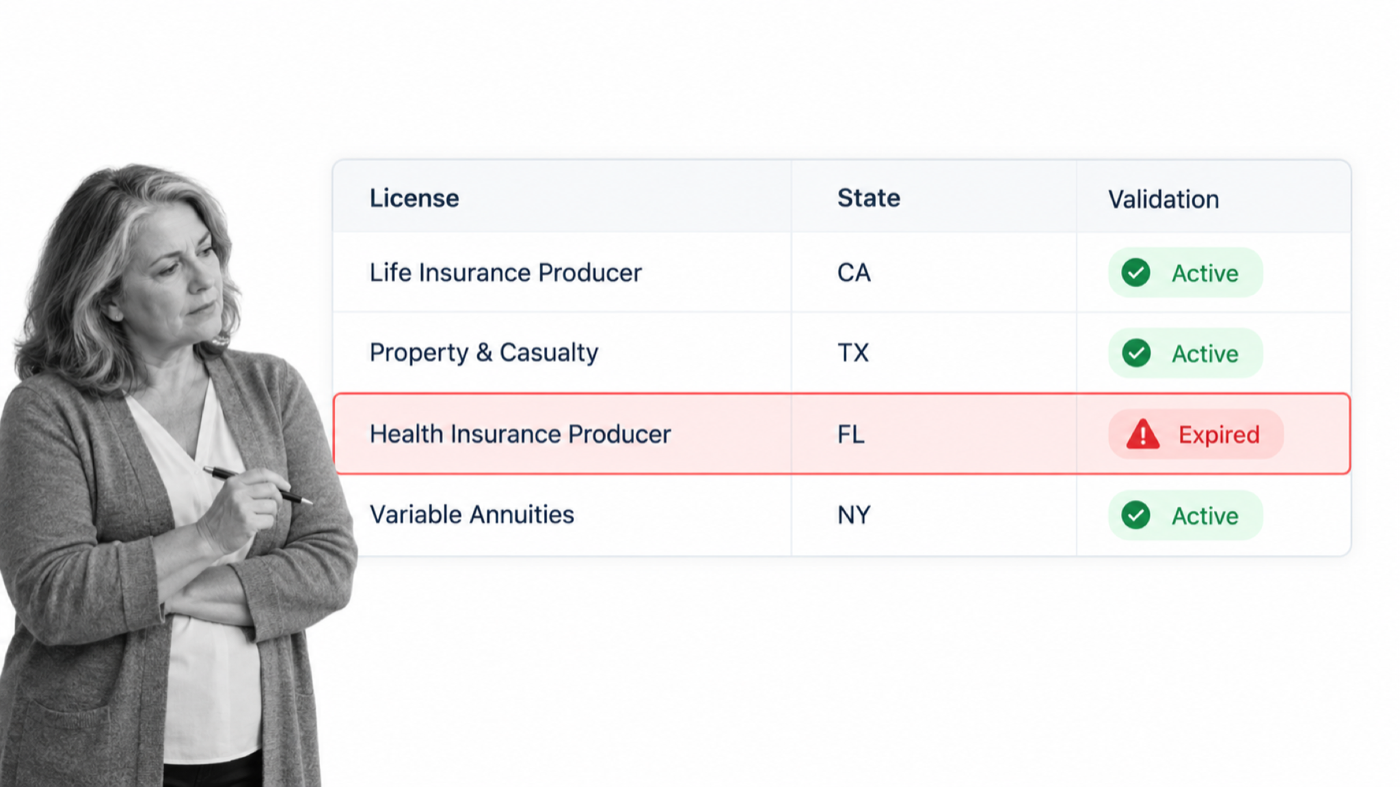
But the real incentives were for recruiting, not training. Brokers were rewarded for hitting targets, not for adhering to processes. For example, brokers were supposed to get licensed in one state and then pay a fee and fill out a couple of forms to have that license validated in other states. But as Buzzfeed reported:
“Even this simple task eluded many sales reps. One former sales rep who started in the Scottsdale office last fall said he had an Arizona license but didn’t bother to get licenses in the other states where he was selling insurance until January.”
Essentially, there were no incentives for actually filling out the paperwork, and no one checking up to make sure that it was all filed correctly. And now, the wheels have fallen off the track.
Inside “The Macro”
What’s more, those licenses were earned under shaky credentials to begin with.
Because Zenefits was so obsessed with their formula of SDRs and brokers, they didn’t care how their brokers were getting licensed. In fact, they created an internal tool to help cheat the licensing system. Business Insider reported the discovery of a “secret app called the Macro that allowed employees to complete a mandatory training course in less than the legally required 52 hours.”
The Macro allowed them to continue to be logged on to the training, racking up the full 52 hours without actually being present, engaged, and learning throughout the process. A lawyer for Sacks said that Conrad believed that 52 hours was too long to spend in training.
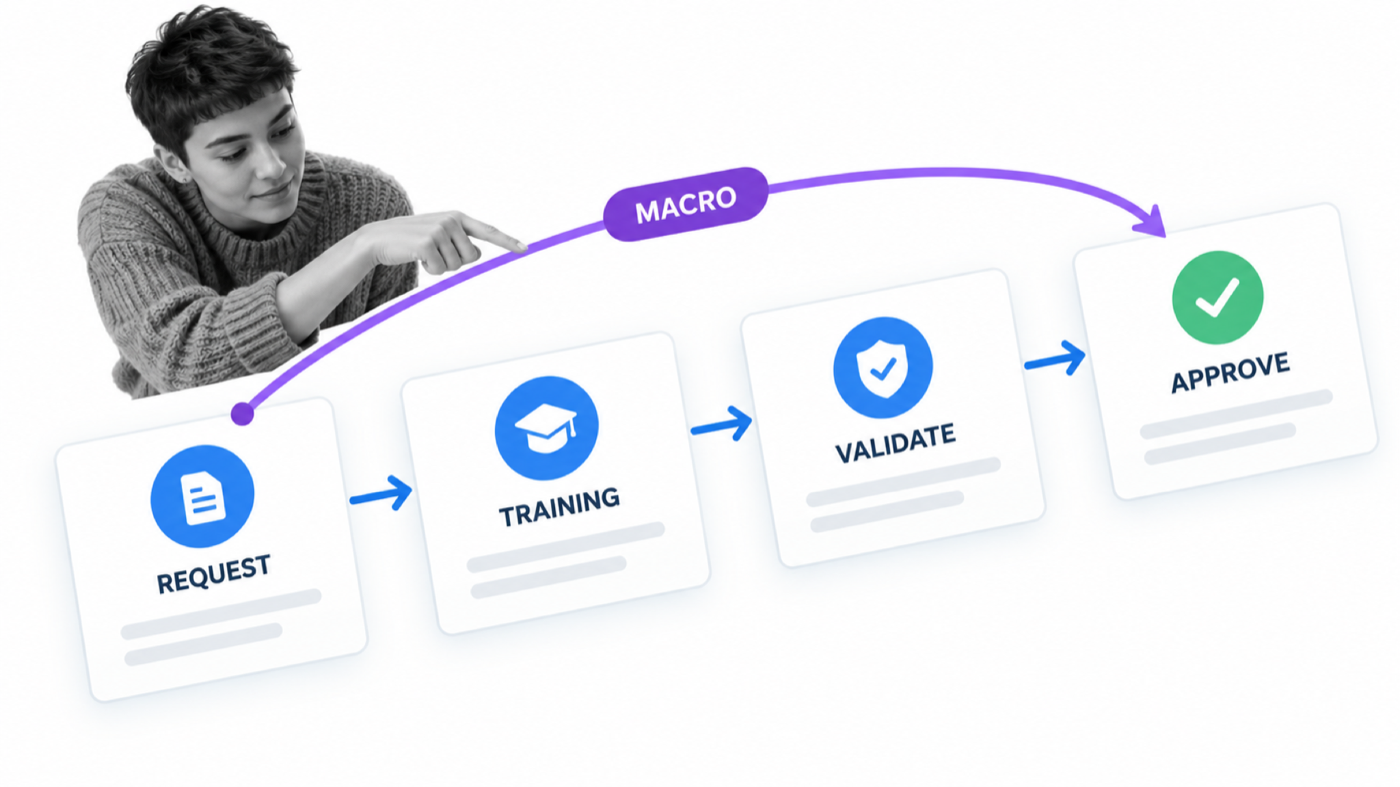
Leadership treated licensing as time away from growth. The lack of accountability did not create an immediate visible failure, but it allowed risk to accumulate inside the sales process.
Customer protections failed
Regulation can feel slow when a company is growing quickly, but licensing controls exist because customers depend on competent advice. Zenefits treated those controls as friction rather than as part of the service.
The regulations Zenefits bypassed existed for a practical reason: customers needed competent advice about coverage that could affect their health and financial security.
“Insurance Broker” is a Regulated Term for a Reason
Insurance producers are licensed at the state level in the United States. The requirement is not ceremonial: customers rely on brokers to understand coverage, exclusions, and obligations before they pay for a policy.
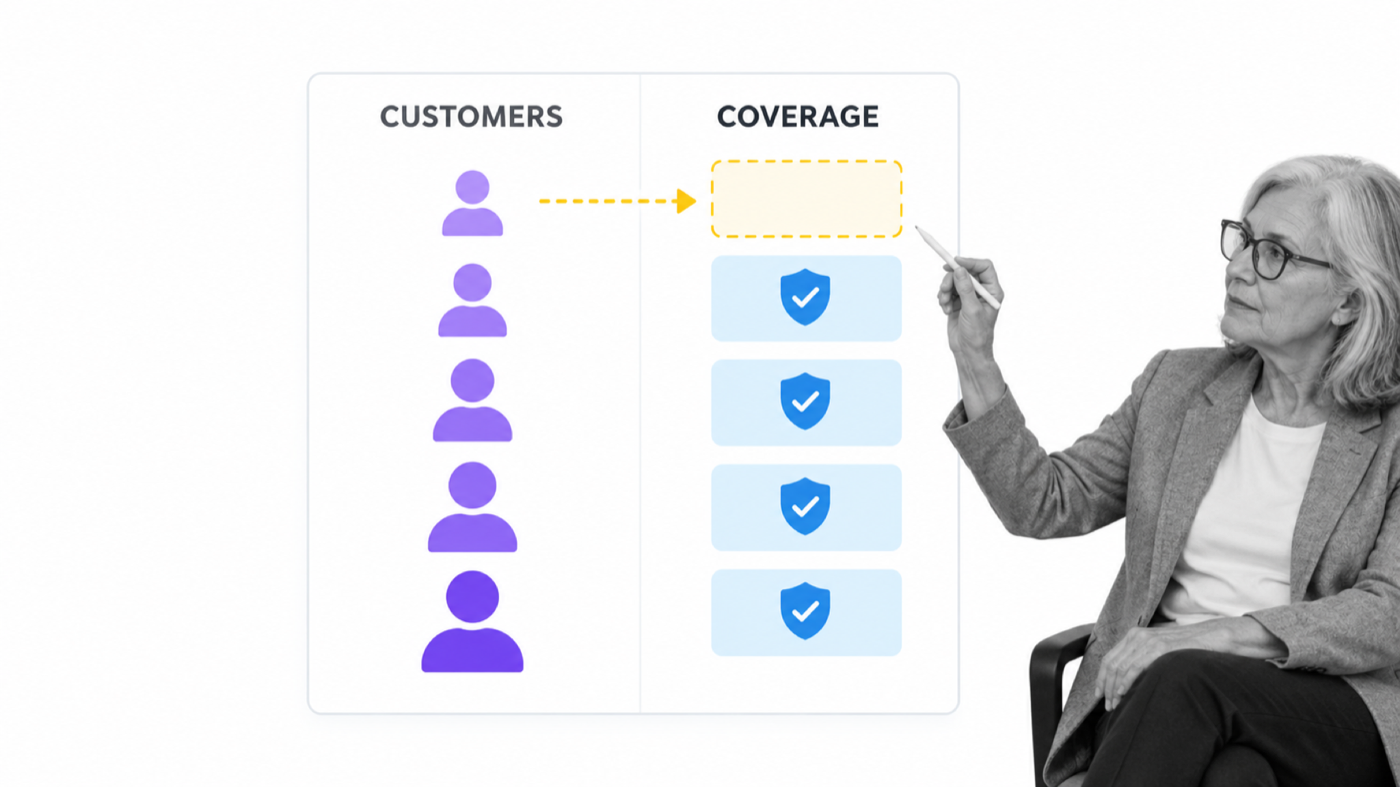
Insurance brokers mediate between insurance companies and customers. State licensing rules commonly require an exam, training, and continuing education before a broker may sell or advise on coverage.
Licensing and continuing education create a minimum standard of competence for work where a bad recommendation can leave a customer exposed.
Other times, people have fallen victim to downright insurance fraud. Just a few years ago, John Paul Kill (yes, that’s his real name) raked in about $3.7 million in premiums insuring trucking companies’ cargo and vehicles, but Kill didn’t actually purchase the insurance, he pocketed it.
So when the Macro allowed for brokers to not officially get licensed, it put consumers at risk of fraud or ineptitude.
The Blind Spot that Almost Sunk Third Eye Blind
Not every failure is fraud. Sometimes customers are harmed because the expert they hired did not understand the coverage they recommended.
One well-known dispute involved the band Third Eye Blind. The band bought advertising-injury coverage through a broker to cover certain legal claims involving creative work, reputation, and image rights.
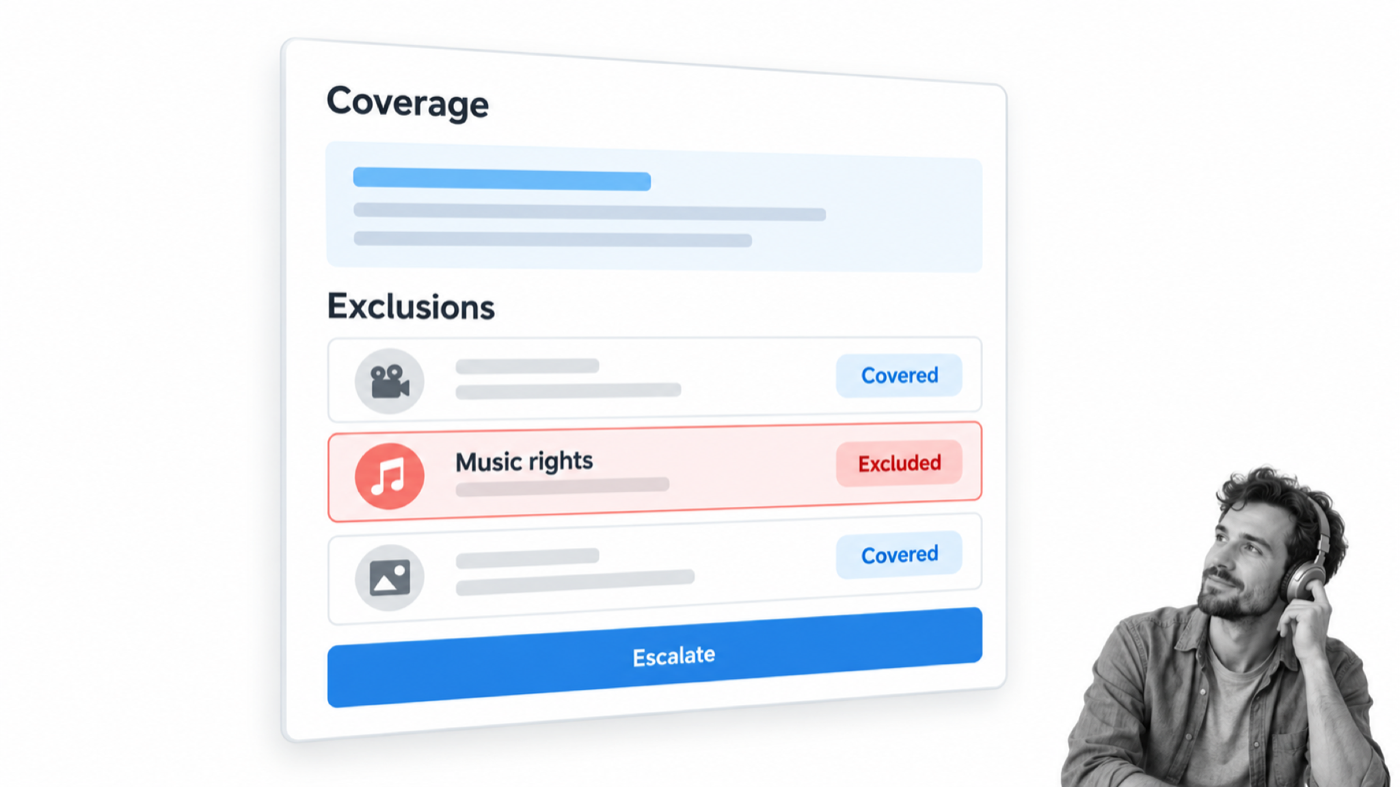
They ended up needing that insurance in 2003 when the band fired guitarist Kevin Cadogan (typical band personality conflicts). Cadogan sued, and the remaining band members spent $3 million of their own money in legal fees because the insurance company, North American Specialty Insurance refused to cover them.
Why? Turns out there was a weird exclusion in their policy. It didn’t cover legal fees in the “field of entertainment” which, for a band, is probably pretty important.
Though they eventually settled, the court held that the insurance broker could be liable for failing to provide competent advice. Insurance brokers need to be competent and know what they’re talking about, before taking people’s money and promising them that they’ll be insured.
If you don’t have as much money as Third Eye Blind, this could be a real problem. So when Zenefits padded hours and hired inept brokers they put people at risk.
Bad processes rotted Zenefits from the inside out
When a company is getting so much press and is the darling of the SaaS world, it can be difficult to take a hard look at processes and say “hey, something isn’t working here.” Even when it’s clear that that’s the case.
That’s exactly what happened with Zenefits. They had been doing so well publicly that they didn’t examine what was really going on, which is why Conrad’s resignation came as such a surprise.
These kinds of processes are dangerous because they rot companies from the inside out. Customers may not see the shortcuts, while employees learn that the shortcuts are normal. Eventually the gap between the stated process and the real process creates consequences for both groups.
High costs for employees
For one, the company cut corners in their employee onboarding processes, a bit ironic for an HR platform. By not fully training and educating all their sales reps and brokers, they wound up with confused and unhappy employees.
The same operating pressure affected employees. When training, licensing, and careful advice were treated as obstacles, people were asked to deliver outcomes without the safeguards needed to do the work well. Pay changes and layoffs added to the sense that employees were absorbing the cost of weak controls.
Employees pushed for a greater voice in 2015, and hundreds reportedly applied to join an internal employee committee. That response was a warning signal: the documented process and the lived process had drifted apart.
Even higher costs for customers
The larger risk fell on customers. When brokers were not properly trained or licensed, customers could not reliably make informed decisions. An anonymous former employee told BuzzFeed News that she failed the licensing test three times but was still allowed to work:
“I took my test three times in a row, and I failed. They still let me work.”
Because she hadn’t received the necessary training, she often had to improvise on calls with customers.
When a customer asked a tricky question, “I would just Google it,” she said. She would tell the customer, “Hold on one second, let me email the expert, he’s on the line, hold on one second, I’ll get back to you.” But in reality, “I would pick one of the first three links and I would just go off of that.”
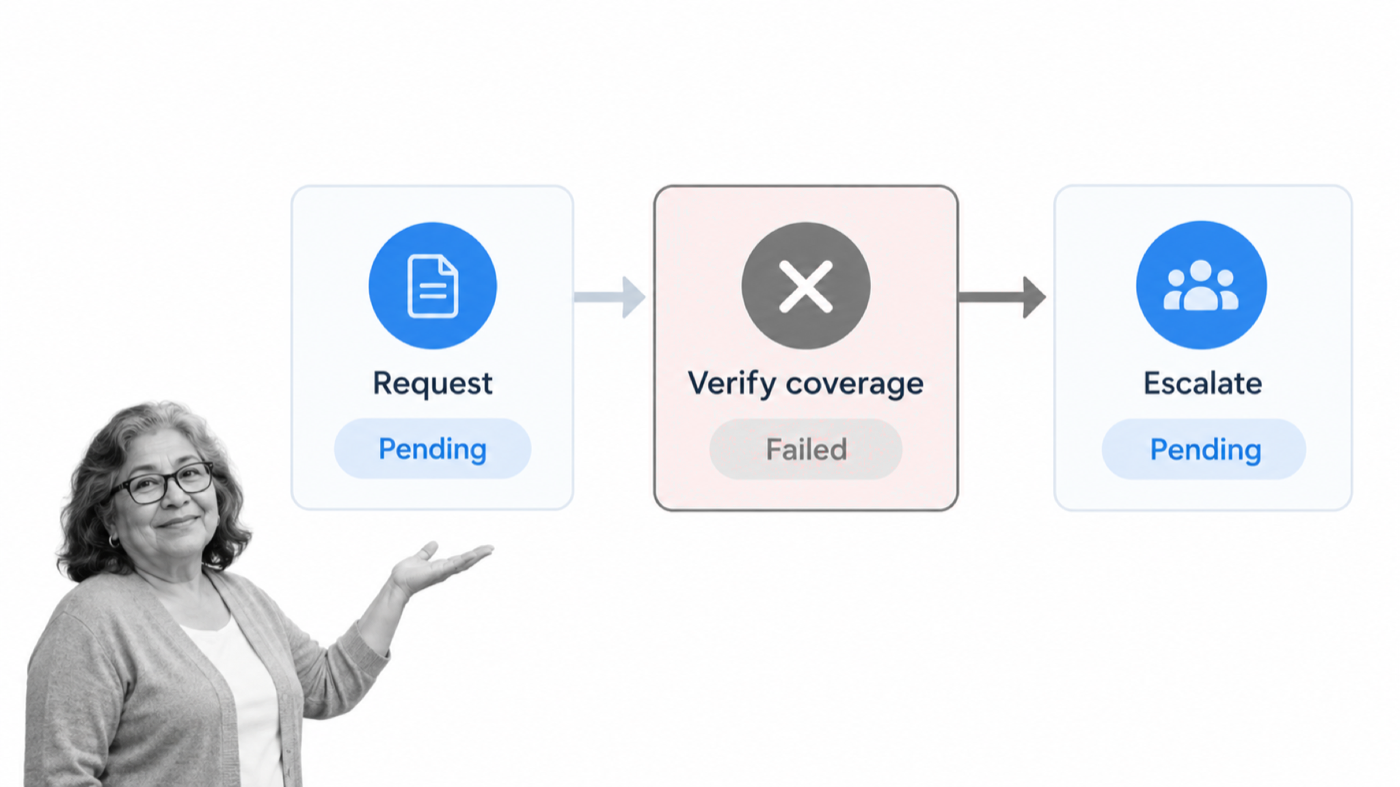
That is how a weak internal process becomes customer risk: uncertainty is hidden at the point where the customer most needs a reliable answer.
Drink It Up, Zenefits
After taking over in February 2016, Sacks set out to rebuild trust and made compliance the center of the response. In a memo to the company he wrote,
“We sell insurance in a highly regulated industry. In order to do that, we must be properly licensed. For us, compliance is like oxygen. Without it, we die.”
Zenefits appointed a former federal prosecutor as chief compliance officer and began a top-to-bottom review of governance, licensing, compliance, and accountability. Later in 2016, the California Department of Insurance imposed a $7 million penalty for licensing and training violations. In 2022, TriNet acquired Zenefits, and the product became part of the TriNet HR Platform.
That kind of compliance and accountability should have been in place from the start to prevent the normalization of deviance and simply to protect customers.
What the Zenefits case teaches about bad processes
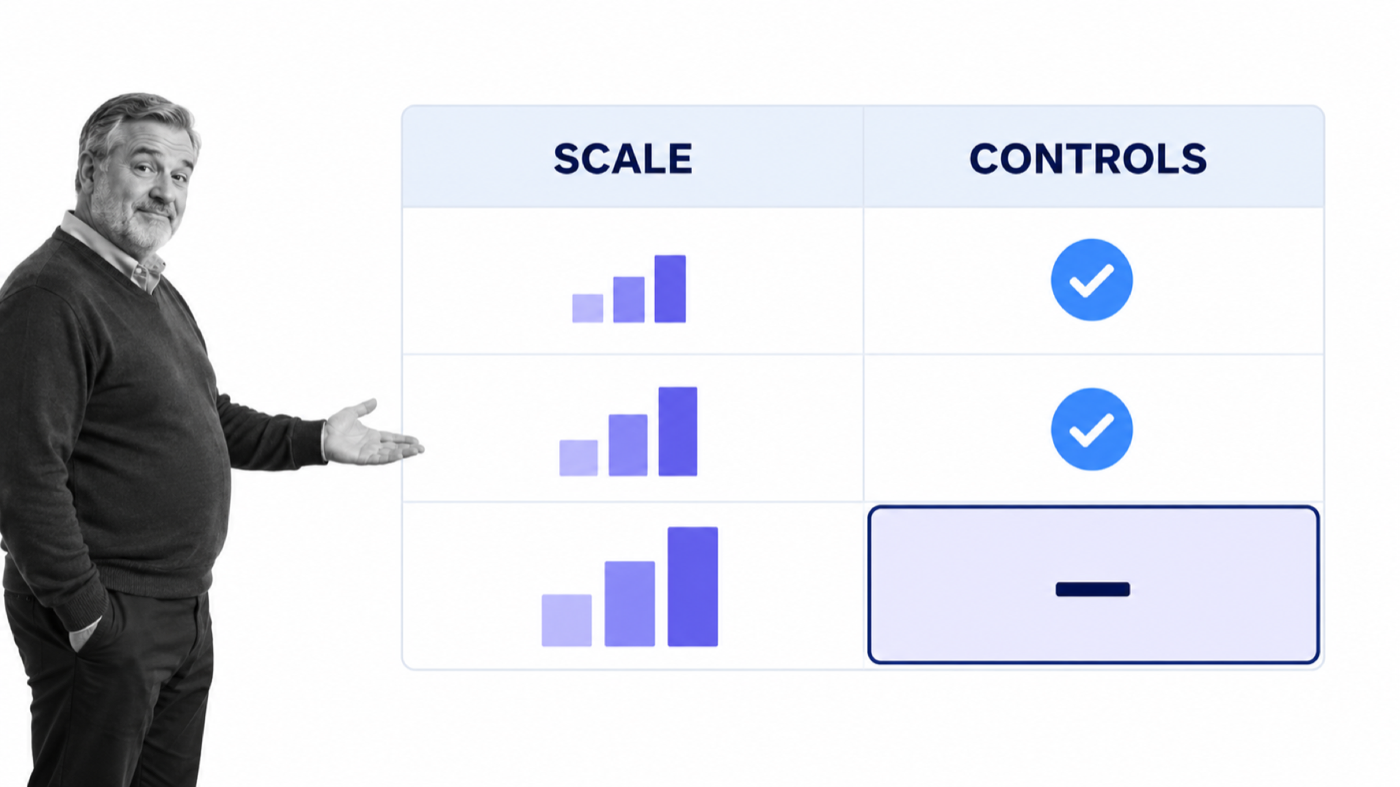
The lesson is not that fast growth is reckless. It is that growth magnifies whatever the operating system already rewards. If a process rewards volume but does not verify competence, ownership, exceptions, and evidence, the company scales risk alongside revenue.
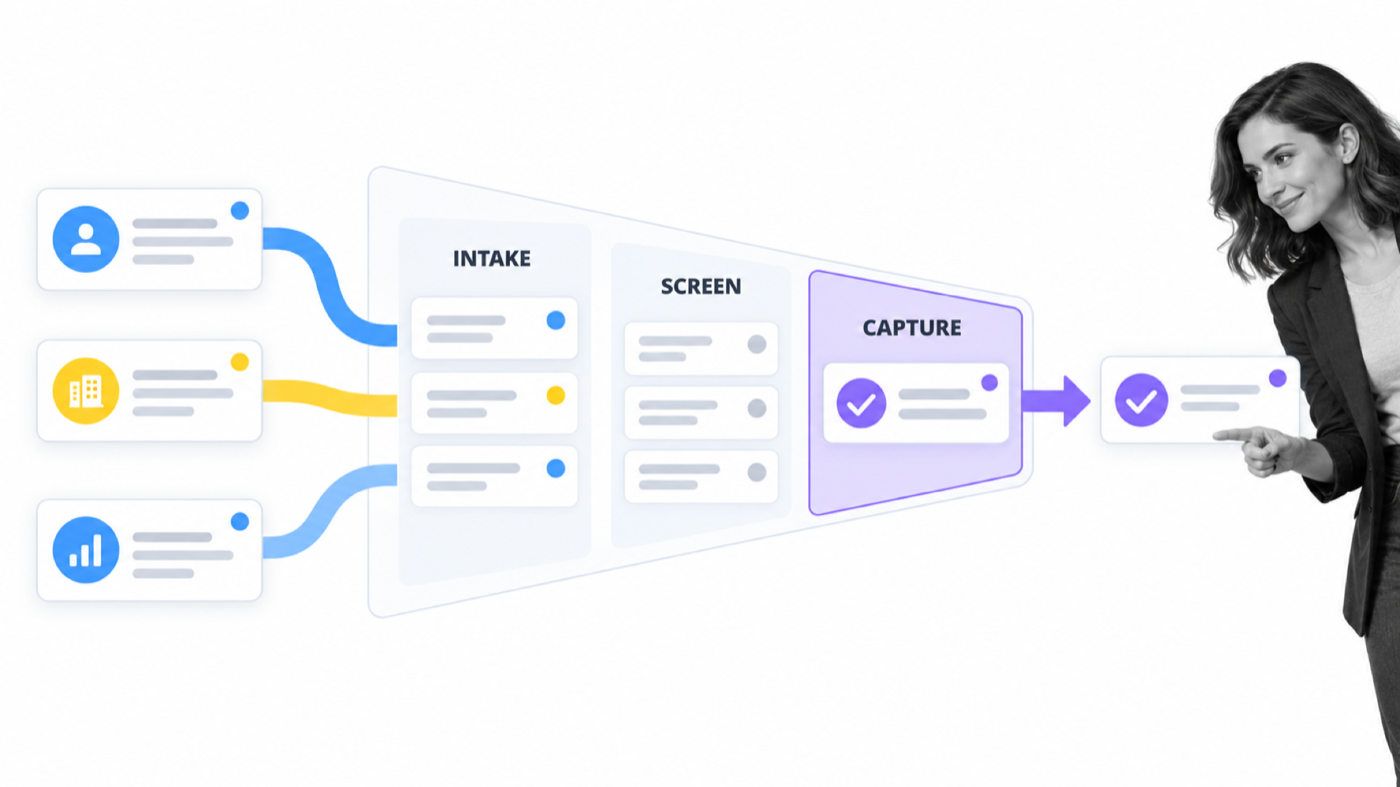
Good processes make the right action easy and the wrong action visible. They assign an owner, define the required control, capture proof, and create an escalation path when reality does not match the plan. That is the discipline Sacks was describing when he wrote in 2016 that compliance was “like oxygen.”
Process Street is a single compliance operations platform with Docs and Ops capability areas plus built-in AI. Teams can govern procedures, run them as accountable workflows, capture evidence as work happens, and spot control gaps before they become customer harm or an audit surprise.
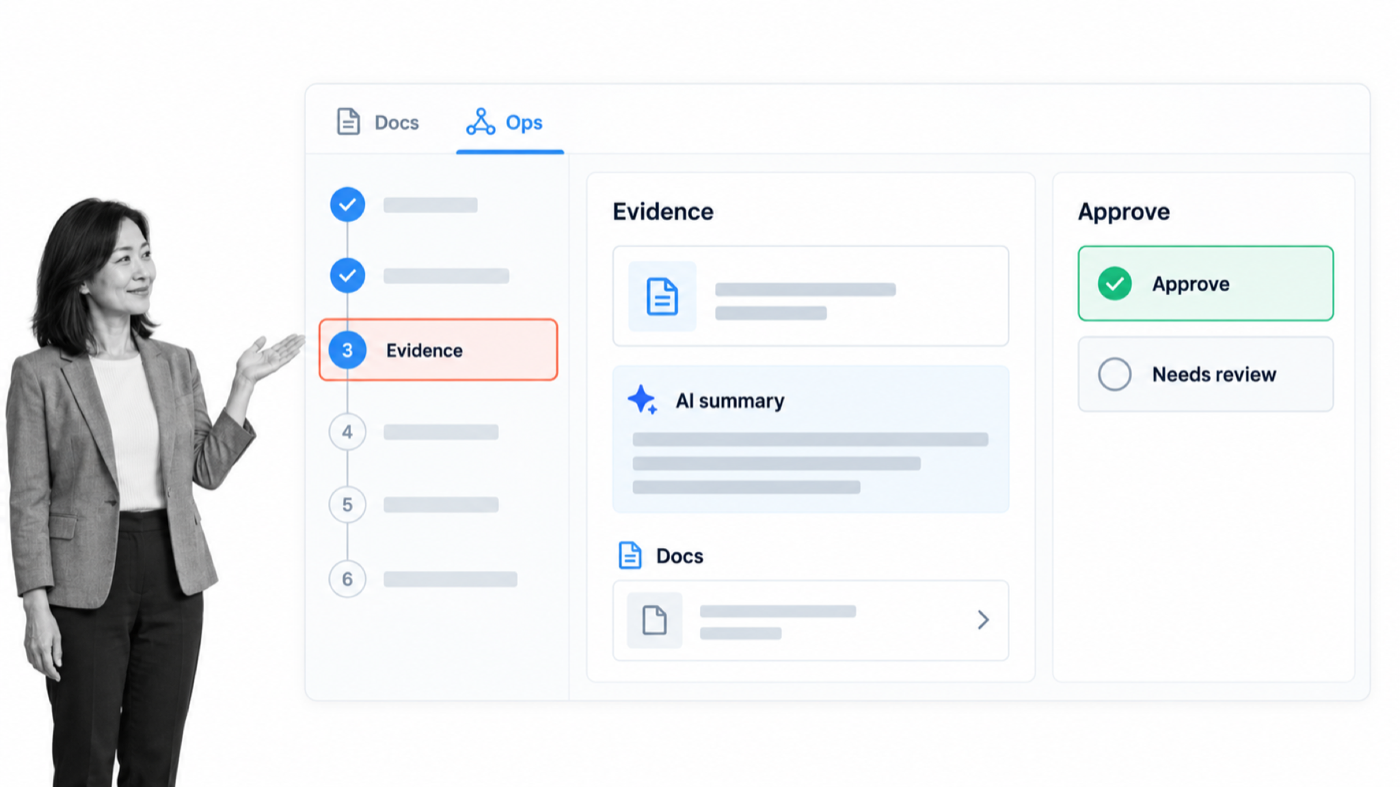
Ready, fire, aim is not a process. The durable alternative is to design incentives, controls, training, and accountability together, then keep checking whether the process works in practice.
Frequently asked questions about bad processes
What makes a business process bad?
A business process is bad when it repeatedly produces avoidable delay, rework, risk, or customer harm. Common causes include unclear ownership, incentives that reward the wrong outcome, missing verification, weak training, undocumented exceptions, and no feedback loop.
How can you identify a broken process?
Look for workarounds, repeated exceptions, skipped approvals, inconsistent results, duplicate data entry, unclear handoffs, and metrics that reward speed without quality. Talk to the people doing the work, then compare the documented process with what actually happens.
How do you fix an inefficient process?
Start with the outcome and risk. Assign an owner, remove unnecessary steps, automate routine handoffs, add controls where failure would matter, define exception paths, and monitor the evidence. Improvement is continuous: review results, learn from deviations, and update the process before the same failure repeats.