Turn every policy into automated workflows with built-in enforcement and audit-ready proof.


A Complete Guide to Hedge Fund Operational Due Diligence
Hedge fund operational due diligence is the independent review of the people, controls, systems, service providers, and operating practices that stand behind a fund. Investment due diligence asks whether a strategy can generate acceptable returns. Operational due diligence asks whether the organization can safeguard assets, calculate values, execute trades, meet obligations, withstand disruption, and give investors reliable evidence of what happened.
A strong investment thesis cannot compensate for weak custody, uncontrolled cash movement, inconsistent valuation, fragile technology, concentrated authority, or an untested recovery plan. ODD gives allocators a disciplined way to test those conditions before committing capital and throughout the relationship.
This guide covers the full review cycle, from scoping and document requests to interviews, independent verification, red-flag resolution, approval, and ongoing monitoring. It is operational guidance, not investment, legal, tax, or regulatory advice.
In this guide:
- What is hedge fund operational due diligence?
- Why does operational due diligence matter?
- What should a hedge fund ODD review cover?
- How do you conduct hedge fund operational due diligence?
- Hedge fund operational due diligence checklist
- How should you evaluate red flags and exceptions?
- When should operational due diligence be repeated?
- How can Process Street support an ODD program?
- Hedge fund operational due diligence FAQs
What is hedge fund operational due diligence?
Hedge fund ODD is a control-focused assessment performed separately from portfolio analysis. It examines whether the manager and fund are genuine, appropriately governed, operationally capable, and supported by reliable third parties. The review follows evidence across the management company, fund vehicles, administrator, custodian, prime brokers, auditor, legal counsel, technology stack, and business continuity arrangements.
The review should distinguish assertions from proof. A policy describes intended behavior. A system configuration, bank mandate, reconciliation record, incident ticket, approval history, or independent confirmation shows how the control operates. Mature ODD tests both design and execution: is the control sensible, and is there evidence that people follow it?
The Investor.gov hedge fund guide recommends understanding who manages the money, how it is invested, and how it can be redeemed. Operational diligence extends that inquiry into the machinery that makes those answers dependable.
Why does operational due diligence matter?
Operational failures can impair a fund without changing the original investment idea. A payment can be misdirected. A valuation can depend on an unchallenged input. A key employee can hold incompatible permissions. A cyber incident can interrupt trading or expose investor data. A service provider can fail at the same time the manager needs it most.
ODD reduces that risk by making dependencies visible and assigning a disposition to every concern. It also improves the investment decision. An allocator can separate a remediable process weakness from a structural conflict, set conditions before funding, require enhanced reporting, or decide that the residual risk is unacceptable.
Public records are an important starting point, not the finish line. The SEC’s Investment Adviser Public Disclosure database provides Form ADV filings and registration information. Reviewers should reconcile those disclosures with offering documents, organizational charts, interviews, service-provider confirmations, and observed practice.
What should a hedge fund ODD review cover?
The review should be broad enough to follow assets, authority, information, and decisions from end to end. The table below provides a practical map.
| Domain | Core question | Evidence to examine |
|---|---|---|
| Governance and people | Who can decide, approve, override, and escalate? | Ownership, committees, role descriptions, conflicts, succession plans |
| Custody and cash | Who holds assets and who can move money? | Custodian records, bank mandates, payment approvals, reconciliations |
| Valuation and NAV | How are positions priced and challenged? | Valuation policy, price sources, overrides, administrator reports |
| Trading and counterparties | Can trades be captured, confirmed, and settled reliably? | Trade flow, break logs, limits, agreements, counterparty reviews |
| Compliance and legal | Are obligations translated into operating controls? | Form ADV, code of ethics, testing, filings, breach records |
| Technology and cyber | Can systems protect data and remain available? | Access reviews, architecture, incidents, testing, vendor controls |
| Resilience | Can critical work continue through disruption? | Impact analysis, recovery plans, backups, exercises, lessons learned |
| Reporting and transparency | Can investors verify material information? | Financial statements, exposure reports, notices, exception history |
How do you conduct hedge fund operational due diligence?
Map the manager, fund, and control environment
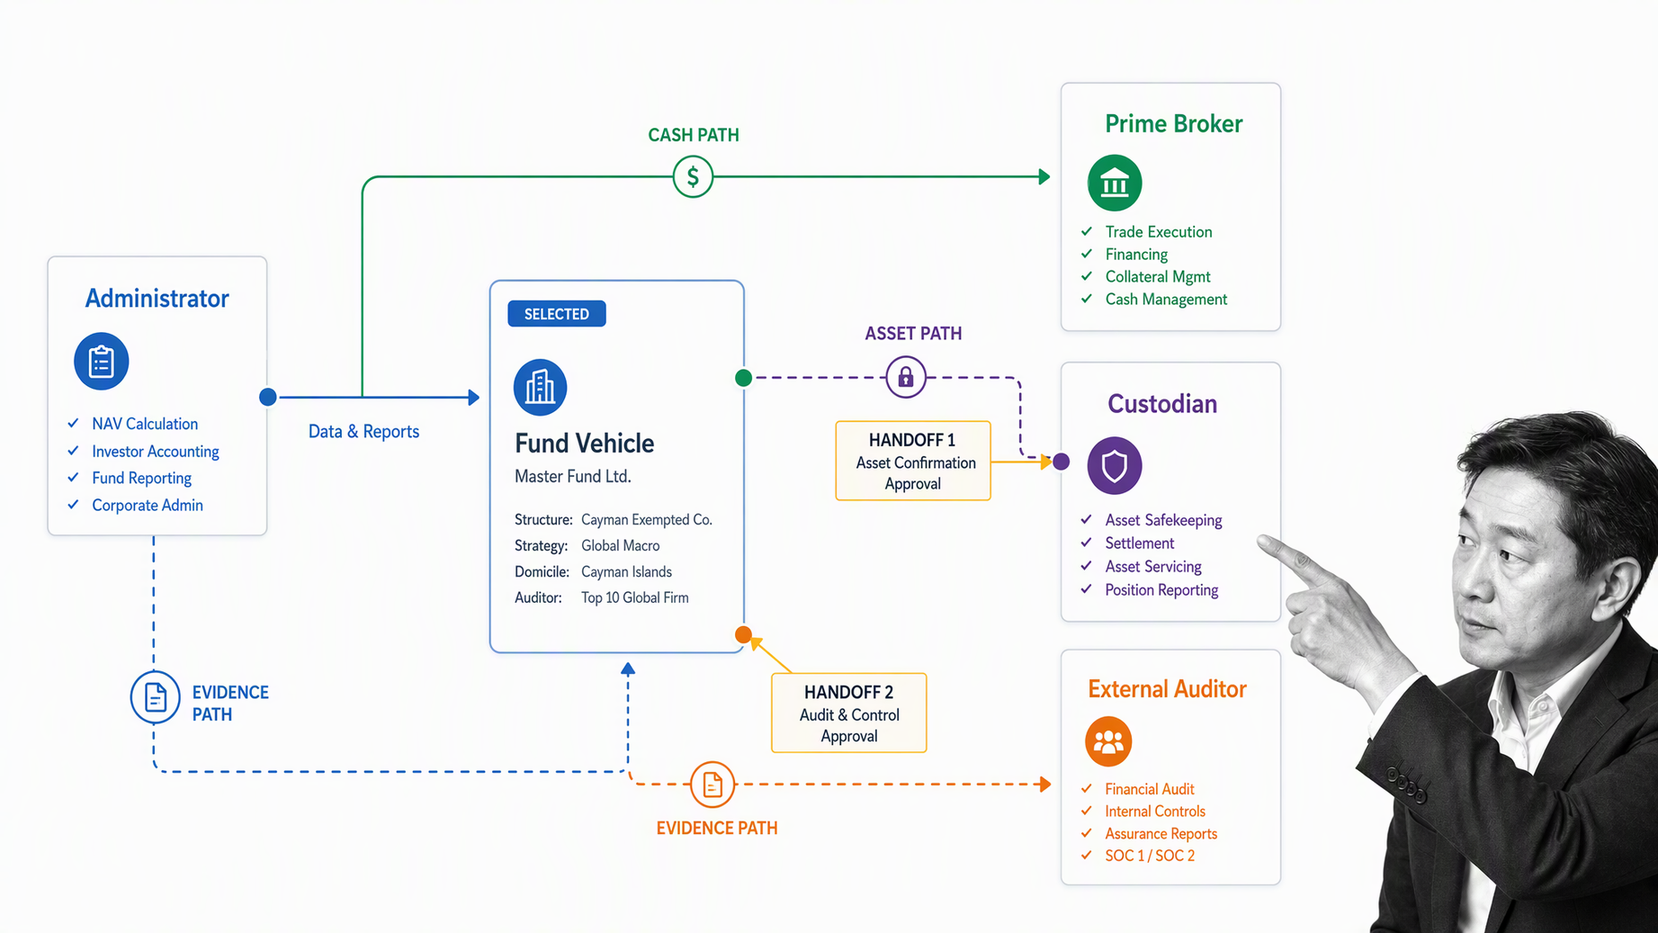
Begin with the legal entities, ownership, fund vehicles, delegated activities, systems, and service providers. Draw the flows of cash, securities, trades, valuations, investor subscriptions and redemptions, data, and approvals. The map should reveal where one person, system, or vendor can create a single point of failure.
Set the scope using strategy complexity, asset liquidity, leverage, geography, investor terms, and recent organizational change. A global macro manager may require deeper review of multi-market operations, collateral, around-the-clock support, and data resilience. A less-liquid strategy may require more attention to valuation governance, side pockets, gates, and cash forecasting.
Issue a focused document request
Request documents that allow cross-checking rather than collecting volume for its own sake. Core materials typically include the offering memorandum, organizational chart, compliance manual, valuation policy, audited financial statements, administrator reports, service-provider agreements, cyber policies, insurance, business continuity plan, incident records, access reviews, and recent regulatory correspondence.
Track each request to a named owner, due date, version, and review outcome. Record gaps explicitly. Missing evidence is not automatically a failure, but it is a fact that must be resolved rather than buried in email.
Interview control owners and test consistency
Interview senior management and the people who operate the controls. Ask the same process question from different angles: who performs it, who reviews it, what system records it, what happens when it fails, and what evidence remains. Differences between policy, management description, and operator practice often reveal the most important follow-up work.
Use scenario questions. Ask how the team would respond to a failed trade, disputed price, urgent wire request, administrator outage, cyber incident, key-person absence, or redemption surge. Strong answers name owners, thresholds, communication paths, and records. Weak answers depend on improvisation or one indispensable employee.
Verify independently and sample execution
Confirm material relationships and facts with independent sources where permission and confidentiality allow. Review Form ADV and disciplinary history. Confirm service providers, audit arrangements, and account-control structures. Sample recent reconciliations, price challenges, access changes, incident closures, and business continuity tests.
Custody deserves direct attention. The current federal custody rule for investment advisers addresses safeguards involving qualified custodians, account statements, examinations, and audited pooled investment vehicles. Applicability depends on the adviser and structure, so legal counsel should assess the precise obligations.
Rate findings, agree actions, and make the decision
Classify findings by severity, likelihood, control dependency, and remediation strength. Separate observations from conditions to funding and from disqualifying issues. Every open item needs an owner, evidence requirement, due date, and decision rule. The final recommendation should explain residual risk, not merely total the number of findings.
Hedge fund operational due diligence checklist
Governance, ownership, and people
- Verify ownership, legal entities, boards, committees, delegated authority, and conflicts.
- Assess experience, turnover, background checks, succession, key-person dependency, and segregation of duties.
- Review how breaches, overrides, complaints, and incidents reach independent challenge and senior oversight.
Custody, cash movement, and asset verification
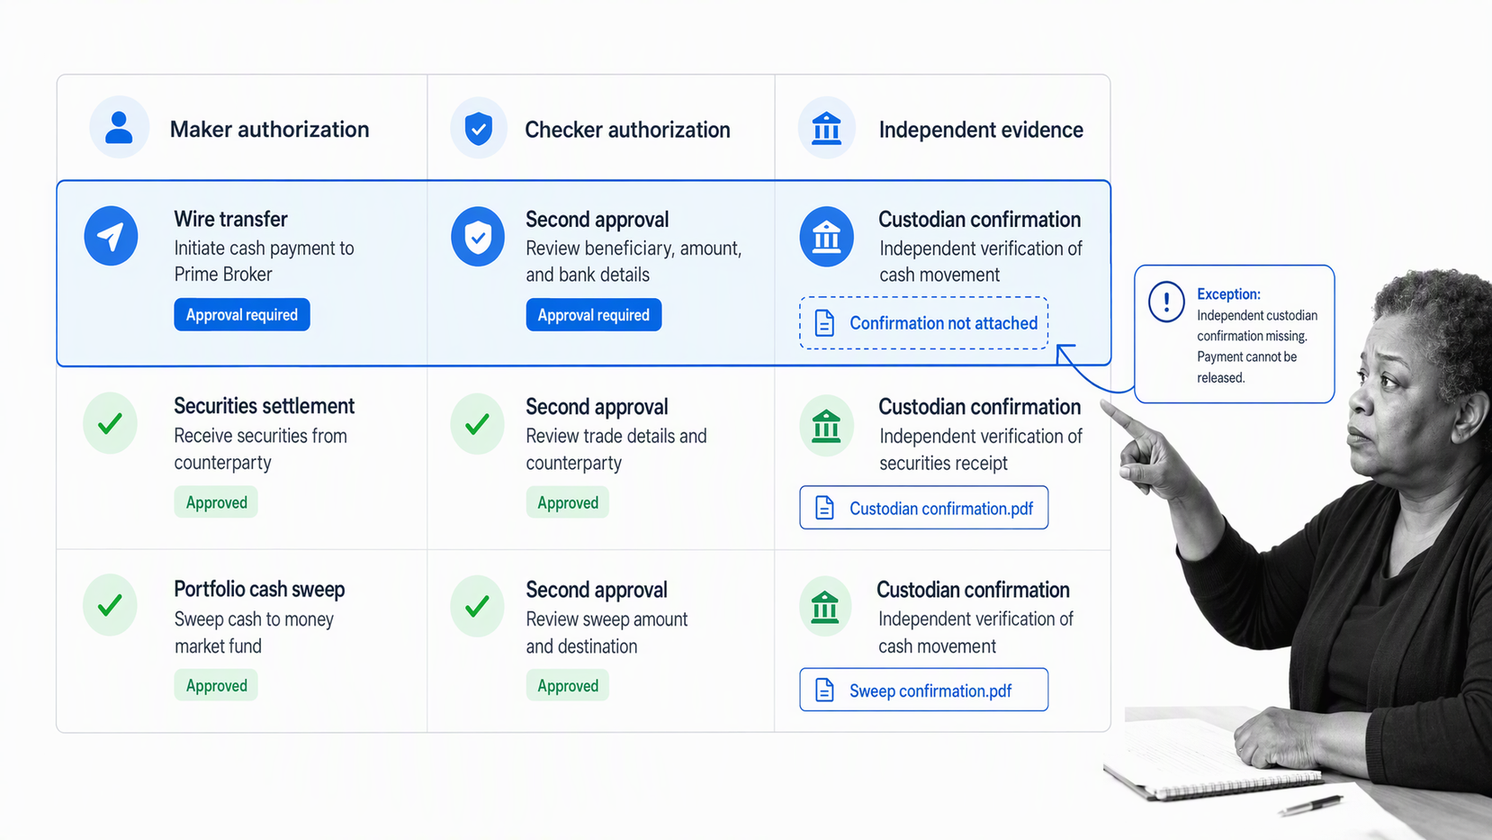
- Identify custodians, prime brokers, bank accounts, signatories, and all paths by which assets or cash can move.
- Test dual authorization, callback controls, standing instructions, restricted access, and reconciliation independence.
- Reconcile manager records with administrator and custodian evidence, and investigate stale breaks or unexplained differences.
Valuation, NAV, and fund accounting
- Map price sources and hierarchy by asset type, including illiquid or model-priced positions.
- Review valuation committee independence, overrides, model changes, side pockets, expense allocation, and error correction.
- Compare the manager’s process with the administrator’s role and audit evidence.
Trading, financing, and counterparties
- Trace order creation, execution, allocation, confirmation, settlement, collateral, and failed-trade handling.
- Review counterparty selection, exposure limits, legal agreements, margin terms, and concentration.
- Test who can change static data, settlement instructions, limits, and broker access.
Compliance, legal, and investor terms
- Reconcile disclosures, registrations, policies, filings, side letters, and marketing materials.
- Review personal trading, gifts, conflicts, restricted lists, complaints, testing, and breach remediation.
- Confirm that subscriptions, redemptions, gates, suspensions, and liquidity terms can be administered as documented.
Technology, cybersecurity, and data
- Inventory critical applications, data feeds, privileged access, vendors, backups, and recovery dependencies.
- Review identity controls, joiner-mover-leaver processes, monitoring, incident response, vulnerability management, and penetration testing.
- Assess third-party technology risk throughout the relationship. NIST Cybersecurity Framework 2.0 organizes cyber risk around Govern, Identify, Protect, Detect, Respond, and Recover.
Business continuity and operational resilience
- Identify critical services, maximum tolerable disruption, recovery targets, alternate locations, and key dependencies.
- Inspect exercise results, backup restoration tests, communications plans, and remediation from prior tests.
- Challenge correlated failure, including a manager and service provider relying on the same infrastructure or personnel.
Service providers and oversight
- Confirm administrators, auditors, custodians, prime brokers, legal counsel, IT providers, and other material delegates.
- Review selection, contracts, service levels, reports, incidents, financial health, subcontractors, and exit plans.
- Test whether the manager actively oversees providers rather than treating a reputable name as a substitute for control.
How should you evaluate red flags and exceptions?
A red flag is a prompt for structured investigation, not a substitute for judgment. Look for inconsistencies across documents and interviews, resistance to independent confirmation, unexplained staff turnover, concentrated authority, stale reconciliations, frequent valuation overrides, weak administrator independence, untested recovery plans, broad privileged access, recurring control breaches, or remediation that repeatedly slips.
Evaluate each issue in context. Determine the assets and processes exposed, the control that failed, how long the condition existed, whether management identified it, the quality of the response, and what independent evidence proves correction. A transparent manager with a credible, tested fix may present less residual risk than a manager with a polished policy and no evidence of challenge.
Document the decision trail. If an exception is accepted, state who accepted it, why, for how long, what compensating control applies, and what event will reopen the decision. Unowned exceptions quietly become permanent policy.
When should operational due diligence be repeated?
ODD should continue after allocation. Use a risk-based cadence that combines scheduled reviews with event-driven reassessment. Annual review is a common organizing rhythm, but material events should trigger work immediately rather than waiting for the calendar.
- Ownership, leadership, key-person, or control-function turnover.
- Administrator, auditor, custodian, prime broker, or other critical-provider change.
- Strategy, leverage, liquidity, valuation, vehicle, or investor-term change.
- Regulatory inquiry, litigation, audit qualification, compliance breach, fraud allegation, or cyber incident.
- Persistent performance dispersion that may indicate valuation, liquidity, or operational questions.
- A failed recovery test, prolonged outage, material reconciliation break, or control remediation delay.
Monitoring should produce the same artifacts as initial review: scoped questions, assigned requests, evidence, findings, approvals, and closure. This keeps the investor’s understanding current and makes trend analysis possible.
How can Process Street support an ODD program?
Run ODD as a controlled workflow
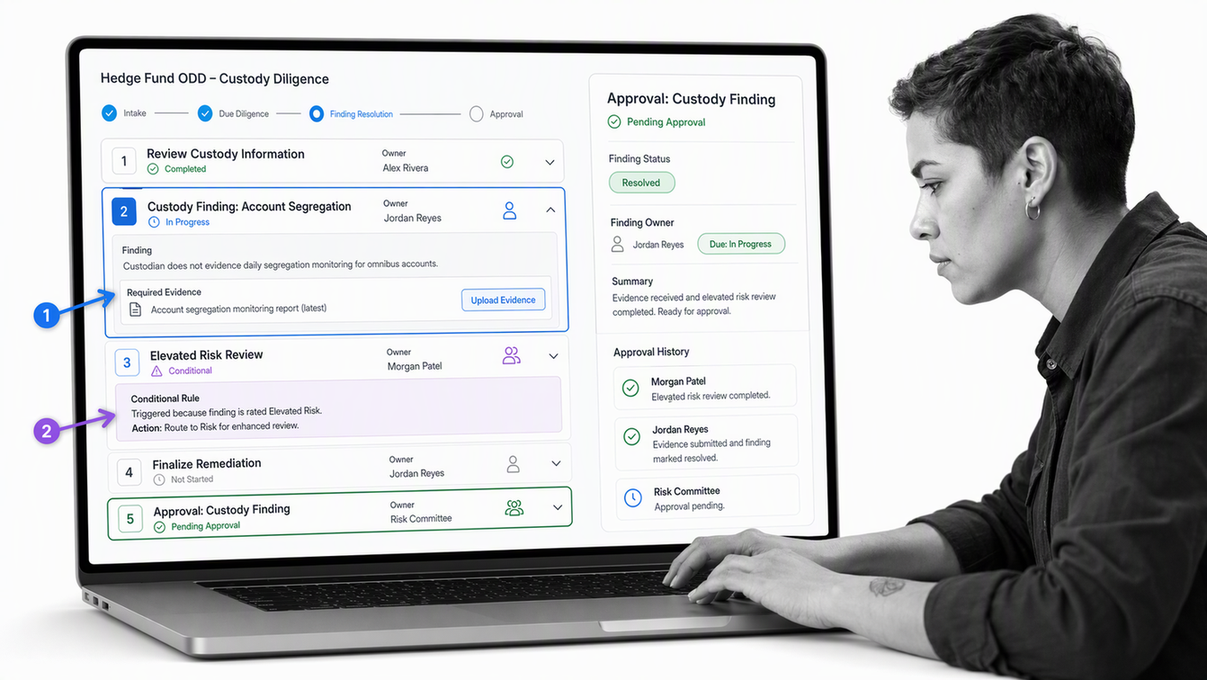
Process Street can turn the diligence method into a repeatable workflow with assigned tasks, required fields, document requests, conditional paths, due dates, approvals, comments, and completion history. The workflow can route deeper testing when a response indicates elevated risk and hold the final recommendation until required evidence and approvals are complete.
A practical design uses one governed run per manager or fund. Intake captures scope and risk factors. Tasks assign document review and interviews. Findings carry severity, owner, action, evidence, and target date. Approval tasks record the investment, risk, legal, or compliance decision in context. The resulting history makes it easier to show what was reviewed, what changed, and why the decision was made.
This approach supports both initial diligence and monitoring. Start with an editable operational due diligence checklist, connect it to a broader risk management process, and use a documented workflow approval process for conditions, exceptions, and final sign-off.
Process Street is an Agentic Process Automation platform for high-stakes operations. Its workflow layer keeps people, AI agents, rules, systems, approvals, and evidence inside a defined process, so automation can accelerate evidence review without removing human control from consequential decisions.
Hedge fund operational due diligence FAQs
What is the difference between investment due diligence and operational due diligence?
Investment due diligence evaluates the strategy, portfolio, performance, and expected return. Operational due diligence evaluates whether the manager and fund can safeguard assets, calculate values, execute reliably, comply with obligations, and withstand disruption.
What documents should an ODD review request?
Typical requests include offering documents, organizational charts, Form ADV, compliance and valuation policies, audited financial statements, administrator reports, service-provider agreements, access reviews, incident records, insurance, and business continuity evidence.
Who should perform hedge fund operational due diligence?
The team should be independent enough to challenge the investment case and should combine operational, compliance, legal, technology, accounting, and investment knowledge. Specialist advisers may support areas that require deeper expertise.
How long does hedge fund operational due diligence take?
Duration depends on the strategy, structure, jurisdictions, service providers, evidence quality, and findings. The process should be driven by risk and evidence rather than a fixed number of days.
What are common hedge fund operational red flags?
Common red flags include concentrated authority, weak segregation of duties, resistance to independent confirmation, inconsistent disclosures, stale reconciliations, frequent valuation overrides, broad system access, untested recovery plans, and overdue remediation.
How often should hedge fund ODD be updated?
Use scheduled periodic review plus event-driven reassessment. Provider changes, leadership turnover, regulatory issues, cyber incidents, strategy changes, control failures, or material liquidity changes should trigger prompt review.