Turn every policy into automated workflows with built-in enforcement and audit-ready proof.


Buy-Side M&A Due Diligence Checklist: A Practical Guide
A buy-side M&A due diligence checklist turns a complex investigation into a controlled decision process. It helps the acquiring team verify the target’s claims, expose material risks, test the investment thesis, and plan what must happen before and after closing.
The checklist is not a substitute for judgment. A strong process connects every request to a reason, every finding to an owner, and every material issue to a deal decision. Use the guide below to scope the review, organize evidence, coordinate specialists, and maintain a defensible record of what was examined.
This guide is general information, not legal, tax, accounting, investment, or regulatory advice. Transaction teams should engage qualified advisers for the deal, industry, and jurisdictions involved.
- What is buy-side M&A due diligence?
- How should buyers scope due diligence?
- What belongs on a buy-side M&A due diligence checklist?
- What documents should go in the data room?
- How do you run buy-side due diligence step by step?
- How should findings affect deal decisions?
- How can Process Street run the diligence workflow?
- What happens after due diligence?
- Frequently asked questions
What is buy-side M&A due diligence?
Buy-side due diligence is the acquiring party’s structured investigation of a target business before completing a transaction. The team tests whether the information provided by the seller is complete, consistent, and supported by evidence. It also evaluates risks and opportunities that may affect valuation, deal structure, contractual protection, financing, closing readiness, or integration.
The work is broader than a document review. Financial results must be reconciled to underlying records. Contracts must be read for obligations, termination rights, and change-of-control effects. Operating claims need to be tested against actual processes, systems, capacity, and dependencies. Technology, security, compliance, and people risks should be evaluated in the context of how the buyer intends to operate the business.
A checklist provides coverage and coordination. It does not guarantee that every fact will be discovered. The objective is to reach a decision with a clear record of the evidence reviewed, assumptions tested, unresolved gaps, and risk treatment agreed by the people authorized to accept it.
How should buyers scope due diligence?
Start with the investment thesis
Write down why the transaction should create value before the review begins. The thesis might depend on recurring revenue, customer retention, geographic expansion, intellectual property, operating capacity, supply security, or cost synergies. Each assumption should become a testable diligence question with an evidence requirement and a named reviewer.
This prevents the team from treating diligence as a race to collect documents. A document matters because it proves or challenges a decision assumption. If a finding does neither, it may not deserve the same review depth as an item connected to valuation, liability, continuity, or integration.
Set materiality and escalation rules
Define what counts as a critical, high, medium, or low issue. Materiality may depend on financial exposure, legal consequence, probability, customer concentration, operational downtime, remediation effort, or damage to the buyer’s strategic objective. Set who can accept each risk level and what must be escalated to the investment committee, board, lender, insurer, or specialist adviser.
Use a single issue log across workstreams. Every issue should record the source evidence, impact, likelihood, owner, open questions, proposed treatment, and decision status. Separate verified facts from estimates and management representations.
Assign workstream owners and decision rights
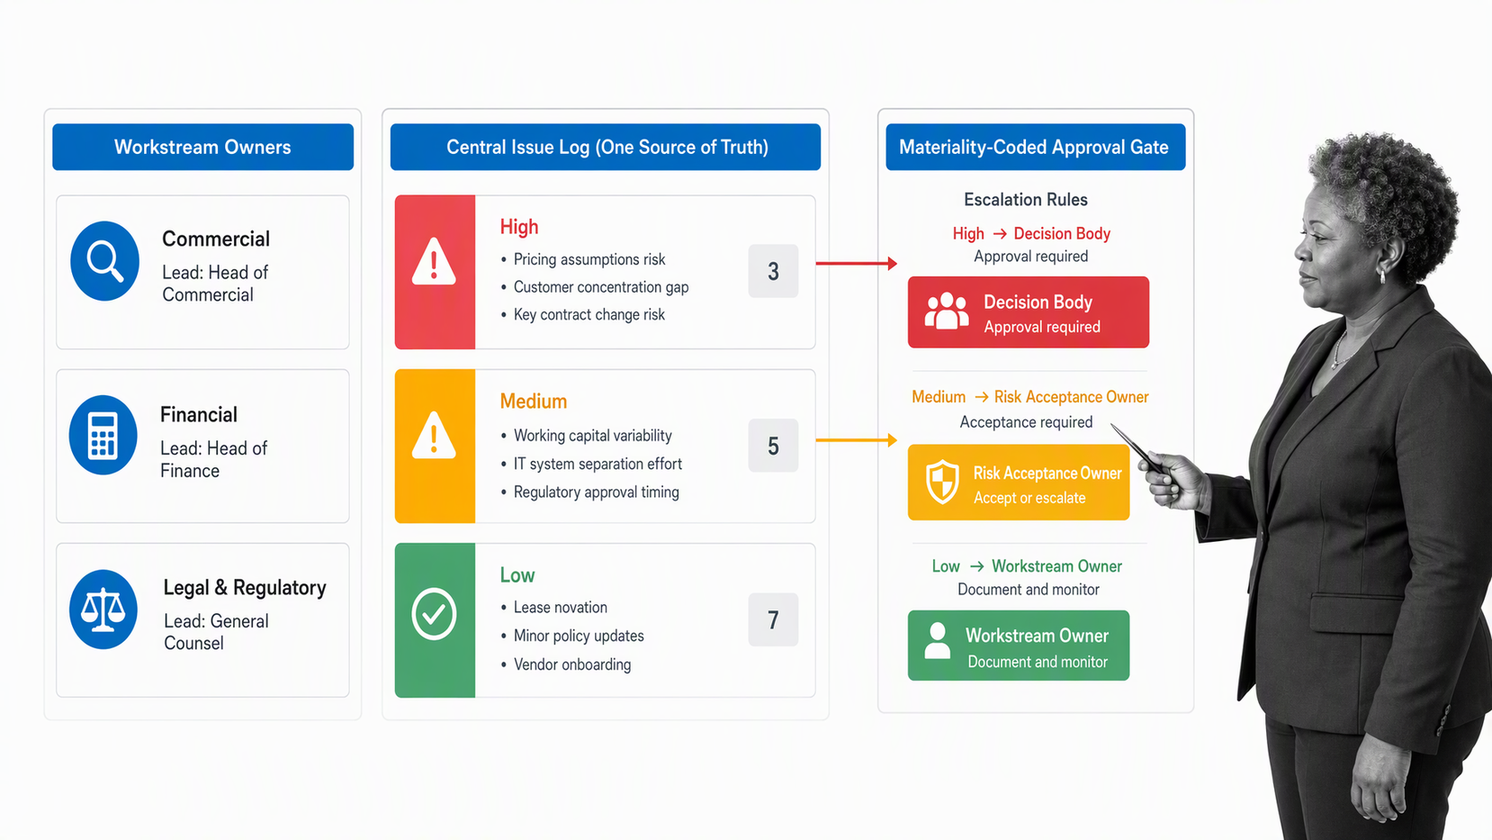
Create one accountable owner for the entire diligence program and one lead for each workstream. Typical leads include corporate development, finance, legal, tax, commercial, operations, people, technology, cybersecurity, compliance, insurance, and integration. Specialists can perform the analysis, but the buyer still needs explicit decision rights for accepting residual risk.
| Role | Primary responsibility | Required output |
|---|---|---|
| Deal lead | Controls scope, timetable, dependencies, and escalation | Consolidated diligence recommendation |
| Workstream lead | Reviews evidence and tests assumptions | Findings, gaps, and risk assessment |
| Legal counsel | Assesses legal exposure and transaction protections | Legal issues and drafting instructions |
| Integration lead | Translates findings into Day 1 and post-close actions | Costed integration and remediation plan |
| Decision body | Accepts, mitigates, transfers, or rejects material risk | Documented proceed, renegotiate, pause, or stop decision |
What belongs on a buy-side M&A due diligence checklist?
The right checklist is risk based. Use the following workstreams as a starting point, then adapt the request list to the deal structure, target profile, industry, and geography. For public-company research, SEC EDGAR search tools provide access to filed reports and statements. Public records are useful corroboration, but they do not replace access to target evidence and specialist review.
Strategy and commercial diligence
- Test the strategic rationale, market attractiveness, competitive position, and sources of value creation.
- Validate the addressable market, pricing power, pipeline quality, sales cycle, churn, renewals, and win-loss patterns.
- Review customer and supplier concentration, key relationship terms, dependency risks, and change-of-control provisions.
- Rebuild synergy assumptions with accountable owners, implementation costs, timing, and downside cases.
- Interview management and relevant functional leaders to compare operating reality with the written narrative.
Financial diligence
- Reconcile audited or reviewed statements, management accounts, general ledger data, bank records, and board reporting.
- Analyze revenue quality, recognition policies, gross margin, recurring versus nonrecurring items, and customer-level trends.
- Review working capital, cash conversion, capital expenditure, debt-like items, commitments, guarantees, and off-balance-sheet exposures.
- Test forecasts against historical performance, contract evidence, capacity, headcount, pipeline, and market assumptions.
- Identify normalized earnings adjustments and document the evidence supporting each adjustment.
Tax diligence
- Review income, payroll, sales, use, value-added, property, and other relevant tax filings and correspondence.
- Identify open audits, uncertain positions, unfiled jurisdictions, tax liens, credits, incentives, and transfer-pricing exposure.
- Assess how transaction structure affects basis, attributes, withholding, elections, and reporting obligations.
- For qualifying asset acquisitions, review the buyer and seller reporting obligations described on the IRS Form 8594 page with tax advisers.
Legal and regulatory diligence
- Confirm legal entities, ownership, capitalization, authority, governance records, subsidiaries, and beneficial ownership.
- Review material customer, supplier, financing, lease, license, partnership, and related-party agreements.
- Identify litigation, investigations, claims, consent orders, settlement obligations, permits, and regulatory correspondence.
- Assess intellectual property ownership, assignments, licenses, open-source obligations, disputes, and contractor-created work.
- Determine whether merger-control, foreign investment, industry, or other approvals may apply. Consult the current official United States HSR materials and qualified antitrust counsel for filing requirements.
Operations and supply chain diligence
- Map how the target delivers its products or services, including critical processes, capacity, quality controls, and failure points.
- Review facilities, equipment, maintenance, inventory, logistics, business continuity, disaster recovery, and insurance coverage.
- Identify single-source suppliers, subcontractors, outsourced services, service-level commitments, and geographic dependencies.
- Compare documented procedures with actual execution and collect evidence from a representative sample of completed work.
- Estimate the cost and timing required to bring operations into the buyer’s control environment.
People and culture diligence
- Review organization structure, critical roles, leadership depth, succession, vacancies, turnover, and retention risk.
- Analyze compensation, incentives, benefits, equity, severance, contractor arrangements, collective bargaining, and employment disputes.
- Identify key-person dependencies and undocumented knowledge that could affect continuity after closing.
- Assess culture through decision patterns, control adherence, employee feedback, and management behavior, not slogans alone.
- Build a communication and retention plan for employees whose departure would threaten the investment thesis.
Technology and cybersecurity diligence
Technology diligence should connect architecture and security posture to operating continuity, integration cost, customer commitments, and regulatory exposure. NIST’s cybersecurity supply chain risk management guidance emphasizes risk assessment across acquisition and supplier life cycles.
- Inventory critical applications, infrastructure, data stores, interfaces, vendors, licenses, and unsupported systems.
- Review architecture, scalability, technical debt, development practices, change management, availability, backups, and recovery testing.
- Examine security governance, access control, vulnerability management, incident history, monitoring, penetration testing, and remediation evidence.
- Map regulated and sensitive data, retention, cross-border transfers, subprocessors, privacy obligations, and customer security commitments.
- Estimate separation, migration, integration, remediation, and recurring technology costs under the buyer’s target operating model.
Compliance and integrity diligence
The compliance review should test whether controls work in practice and how identified issues are tracked. The U.S. Department of Justice guidance on corporate compliance programs addresses comprehensive acquisition-target diligence, timely integration, risk review ownership, and post-acquisition remediation.
- Review the compliance risk assessment, code of conduct, policies, training, reporting channels, investigations, discipline, and remediation.
- Test third-party onboarding, monitoring, sanctions screening, anti-bribery controls, conflicts processes, and books-and-records controls.
- Examine prior misconduct, whistleblower allegations, internal audit findings, regulator contact, and repeat control failures.
- Confirm how compliance findings will become closing actions, contractual protections, or funded post-close remediation.
What documents should go in the data room?
The data room should make evidence easy to locate, verify, and trace to the request list. Use a clear folder taxonomy that mirrors the diligence workstreams. Keep an index with the request ID, document owner, upload date, version, confidentiality restriction, reviewer, and review status.
| Workstream | Core evidence | Common follow-up |
|---|---|---|
| Corporate | Formation documents, cap table, governance records, subsidiaries | Ownership inconsistencies or missing approvals |
| Financial | Statements, ledger extracts, budgets, debt schedules, bank support | Reconciliations and quality of earnings questions |
| Tax | Returns, audits, elections, nexus analysis, correspondence | Unfiled jurisdictions or uncertain positions |
| Commercial | Customer data, contracts, pipeline, pricing, churn, market research | Concentration, renewal, and forecast support |
| Legal | Material contracts, disputes, permits, IP records, insurance | Change-of-control rights and contingent liabilities |
| Operations | Process maps, supplier records, quality data, continuity plans | Capacity, dependency, and control testing |
| People | Organization charts, agreements, compensation, benefits, turnover | Retention and key-person mitigation |
| Technology | Architecture, asset inventory, licenses, security evidence, incidents | Remediation cost and integration feasibility |
Avoid treating an upload as proof that a request is complete. Reviewers should be able to mark evidence as accepted, incomplete, superseded, inconsistent, or not applicable. Maintain a question-and-answer log that links each answer to the supporting document and records any follow-up commitment.
How do you run buy-side due diligence step by step?
1. Confirm scope and confidentiality
Agree the review scope, clean-team requirements, data access rules, communication channel, and authorized participants. Align the workplan with the letter of intent, exclusivity period, financing path, regulatory process, and intended transaction structure.
2. Build the request list and data room
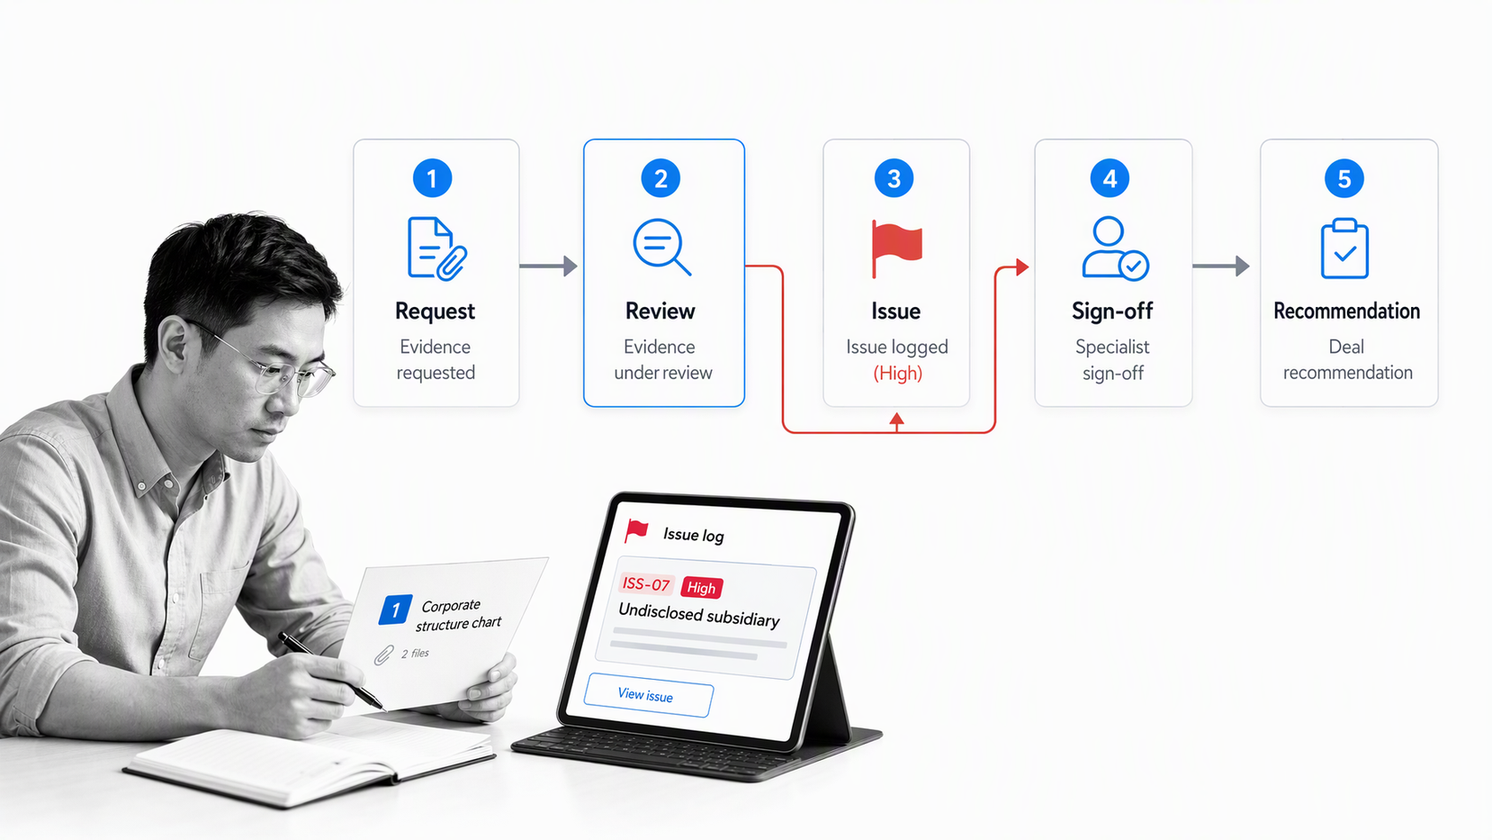
Convert the investment thesis and workstream scope into numbered requests. Specify the exact evidence needed, period covered, owner, reviewer, due date, and acceptance standard. Organize the data room to match the request list so the team can distinguish missing evidence from work that has not yet been reviewed.
3. Triage the first evidence
Start with documents that can change the rest of the review: financial statements, major contracts, capitalization, debt, litigation, customer concentration, intellectual property ownership, security incidents, regulatory matters, and key employment arrangements. Early triage helps direct specialist time toward the highest-risk assumptions.
4. Test claims and reconcile inconsistencies
Cross-check management presentations against contracts, ledger detail, customer data, system reports, policy evidence, and public records. Sample completed transactions or operational cases where appropriate. When sources disagree, log the discrepancy and keep the request open until the team has a supported explanation or treats the gap as a risk.
5. Interview management and specialists
Use interviews to explain evidence, not to replace it. Send focused questions in advance, record the answer and owner, and request corroborating material. Separate current-state facts from future plans. Capture assumptions that must be reflected in valuation, integration, or transaction documents.
6. Maintain the issue and decision log
Hold regular cross-workstream reviews. A contract issue can affect revenue quality, technology cost, customer retention, and integration timing at once. Consolidate duplicate findings and make dependencies visible. Escalate according to the materiality rules agreed at the start.
7. Produce the diligence report
The final report should lead with decisions, not document counts. Summarize the investment thesis result, material findings, unresolved gaps, recommended deal protections, required closing actions, post-close remediation, integration cost, and residual risks. State who reviewed each workstream and what limitations applied.
How should findings affect deal decisions?
Turn findings into deal decisions
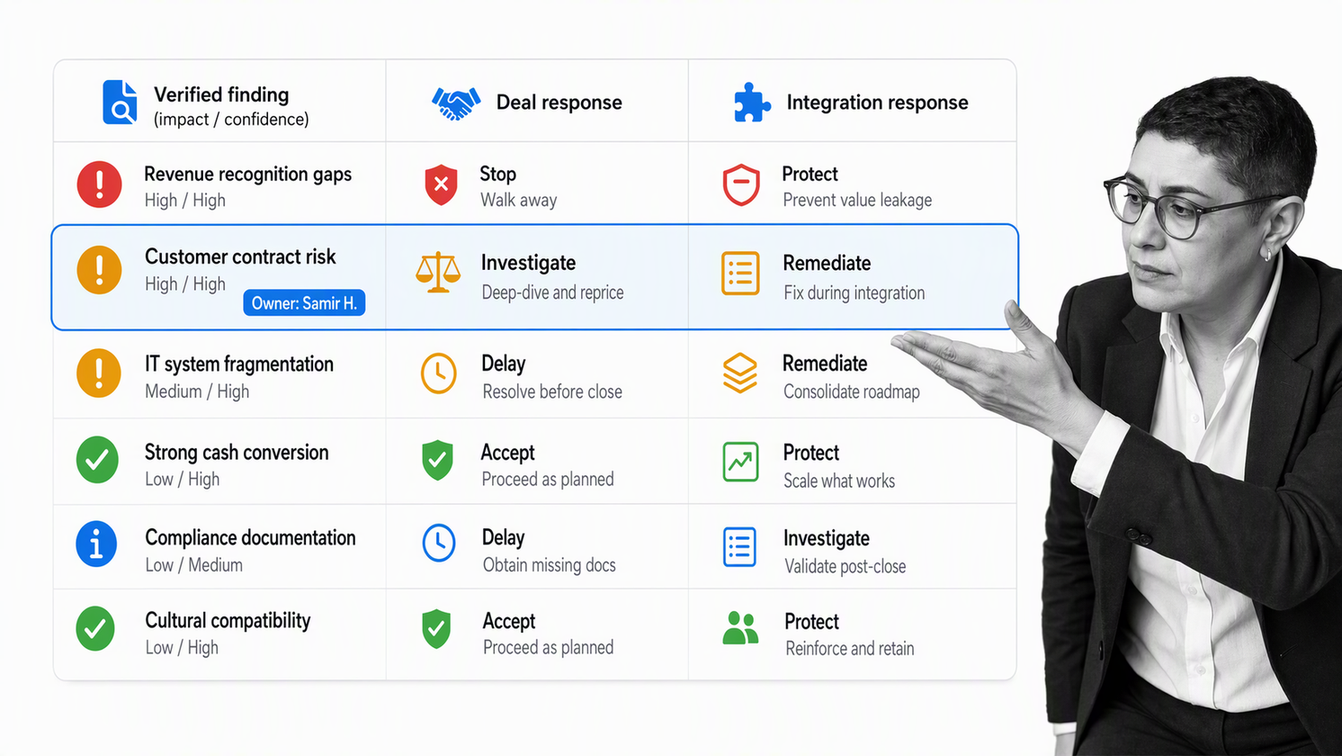
A finding becomes useful when the team decides what to do about it. The available responses usually include accepting the risk, obtaining more evidence, correcting the issue before closing, changing price or structure, adding contractual protection, transferring risk through insurance, funding remediation, delaying closing, or ending the transaction.
Keep a traceable line from source evidence to finding, impact, recommendation, and final decision. If management accepts a risk, record the person with authority to accept it and the assumptions supporting that choice. If the issue moves to the purchase agreement, link the drafting instruction back to the diligence finding.
| Finding type | Possible deal response | Possible integration response |
|---|---|---|
| Unsupported earnings adjustment | Revise valuation or price mechanism | Improve reporting and close controls |
| Change-of-control consent | Make consent a closing condition | Assign relationship owner and fallback plan |
| Security weakness | Require remediation, protection, or risk allocation | Fund and sequence a security workplan |
| Key-person dependency | Use retention or transition arrangements | Document knowledge and build succession |
| Compliance control gap | Require disclosure and contractual treatment | Implement controls, testing, and ownership |
| Unclear integration cost | Adjust economics or reserve | Validate dependencies and phase the migration |
How can Process Street run the diligence workflow?
Run the checklist in Process Street
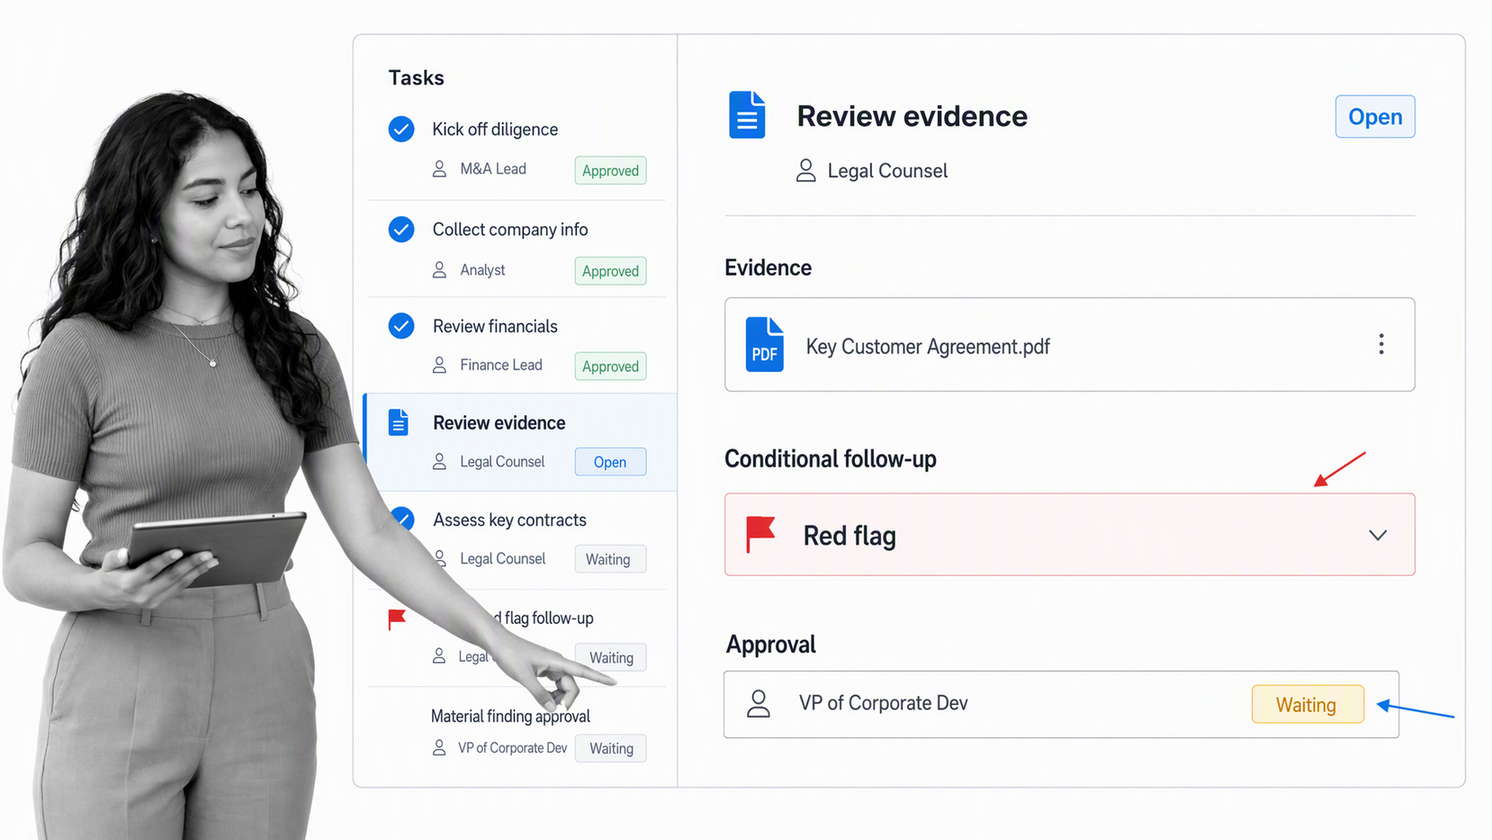
The free Process Street M&A Due Diligence Checklist provides a reusable starting point for collecting corporate, financial, strategic, intellectual property, asset, contract, employee, litigation, and compliance information. It also includes review and approval steps for the diligence report and the final go-forward decision.
A Process Street workflow can turn the request list into assigned work with clear due dates and evidence fields. Conditional logic can reveal additional tasks when a response identifies a risk. Approval tasks can route material findings to the right decision maker. Stop tasks can prevent a later stage from advancing before required work is complete. Role assignments make the same workflow reusable across transactions even when the people change.
Build the workflow around control points: scope approval, evidence acceptance, specialist sign-off, issue escalation, report approval, and the proceed decision. Keep the data room as the secure document repository when appropriate, while the workflow coordinates who must review what, what remains open, and what evidence supports completion.
- Create one workflow run for each target or transaction.
- Assign every request and review task to a named role.
- Require links or file evidence before critical tasks can be completed.
- Use conditional paths for industry, geography, transaction structure, and red-flag responses.
- Route material issues through approvals with the decision and rationale recorded.
- Carry open findings into a separate closing and integration workflow.
What happens after due diligence?
Due diligence ends only when its conclusions have been absorbed into the transaction and operating plan. Open items should be classified as pre-signing, pre-closing, Day 1, or post-close actions. Each action needs an owner, due date, budget, evidence requirement, and escalation path.
Finalize transaction protections
Legal and financial advisers translate material findings into the definitive documents and economics. Confirm that the final drafting reflects the approved risk treatment, including any representations, warranties, indemnities, covenants, escrows, holdbacks, price mechanisms, consents, or closing conditions.
Prepare Day 1 controls
Identify what must be true when ownership changes: authority, access, banking, payroll, customer service, supplier continuity, security monitoring, regulatory reporting, insurance, and employee communication. The integration team should receive the evidence and rationale behind each control, not just a list of tasks.
Track remediation and integration
Move every accepted issue into a funded remediation plan. Keep the original finding, owner, target state, milestone, and proof of completion linked. Review whether the combined business is realizing the assumptions used to approve the transaction, and escalate when actual results diverge from the investment case.
A disciplined handoff protects the value of the diligence work. The same evidence that shaped the deal should shape integration priorities, control design, and management reporting after closing.
Frequently asked questions
What is included in a buy-side M&A due diligence checklist?
A complete checklist covers the target’s strategy, financial performance, tax position, legal obligations, commercial model, operations, workforce, technology, cybersecurity, intellectual property, compliance, insurance, and integration requirements. The buyer should tailor depth and evidence requirements to the transaction structure, industry, geography, and risk profile.
Who should own the buy-side due diligence process?
A deal lead or diligence program manager should own the overall process. Each workstream also needs a named specialist, such as finance, legal, tax, operations, people, technology, security, and compliance. Decision rights for escalating risks and approving exceptions should be agreed before document review begins.
What is the difference between buy-side and sell-side due diligence?
Buy-side due diligence is performed for the potential acquirer and tests whether the target supports the buyer’s investment thesis, price, risk tolerance, and integration plan. Sell-side due diligence is organized for the seller and aims to prepare evidence, identify issues early, and reduce disruption during a buyer’s review.
How should a buyer manage missing due diligence documents?
Log every missing item, assign an owner, set a response date, and record why the evidence is unavailable. Decide whether an alternative source is acceptable. Material gaps should become explicit risks that influence valuation, contractual protection, closing conditions, or the decision not to proceed.
How do due diligence findings affect the purchase agreement?
Findings can affect price, working capital mechanisms, representations, warranties, indemnities, escrows, covenants, closing conditions, and post-close remediation commitments. Legal, tax, and financial advisers should determine how a specific finding is reflected in the transaction documents.
Can Process Street be used for M&A due diligence?
Yes. A Process Street workflow can assign diligence requests, collect files and responses, route exceptions with conditional logic, require approvals, enforce completion order, and preserve a record of the review. The workflow should complement, not replace, qualified legal, financial, tax, security, and regulatory advice.