


Enterprise mobility management (EMM) is the combination of technology, policies, and operating processes used to secure and manage mobile devices, applications, identities, and business data. It covers company-owned and employee-owned phones and tablets throughout their lifecycle, from enrollment and access through incident response and retirement.
EMM makes mobile work possible without treating every device as trusted by default. A practical program combines device management, app and data protection, identity controls, employee privacy, documented exceptions, and evidence that controls actually ran. This guide explains how EMM relates to MDM, MAM, BYOD, and unified endpoint management, then shows how to implement it without creating unnecessary friction.
- What is enterprise mobility management?
- BYOD and the benefits of EMM
- Enterprise mobility management best practices
- How Process Street supports EMM operations
- Enterprise mobility management FAQ
The modern workforce is, quite literally, movers and shakers. Whether a device is self-bought or company-bought, employees use mobile devices in the office, between meetings, while traveling, and when working from home. For the security-minded, that creates familiar hazards: theft, security breaches, and data loss. Modern mobility needs modern controls.
What is enterprise mobility management?
Enterprise mobility management is a management layer for mobile work. It brings together technical controls and repeatable operating procedures so people can use mobile devices while the organization protects access, applications, and data. IBM describes EMM as managing mobile devices, applications, content, and security. The exact product category has evolved, but that operating goal remains useful.
In practice, EMM includes the processes, procedures, and technology that help secure mobile devices in a business context. There may be software for the IT team to control devices remotely, processes to keep workers secure while using their mobile devices, and procedures to protect employee and corporate data if the worst happens. It is a broad term, but it boils down to keeping data and devices safe if an endpoint is lost, stolen, or corrupted.
Enterprise mobility management is a set of technology, processes, and policies to secure and manage the use of corporate-owned and employee-owned mobile devices within an organization. EMM is constantly evolving to accommodate an ever-changing set of device platforms and mobility trends in the workplace.
A complete EMM program is wider than installing an agent. It defines which device ownership models are allowed, how devices are enrolled, what access conditions apply, which data can move between work and personal apps, how lost devices are handled, what evidence is retained, and how access is removed when a device or employee leaves the program.
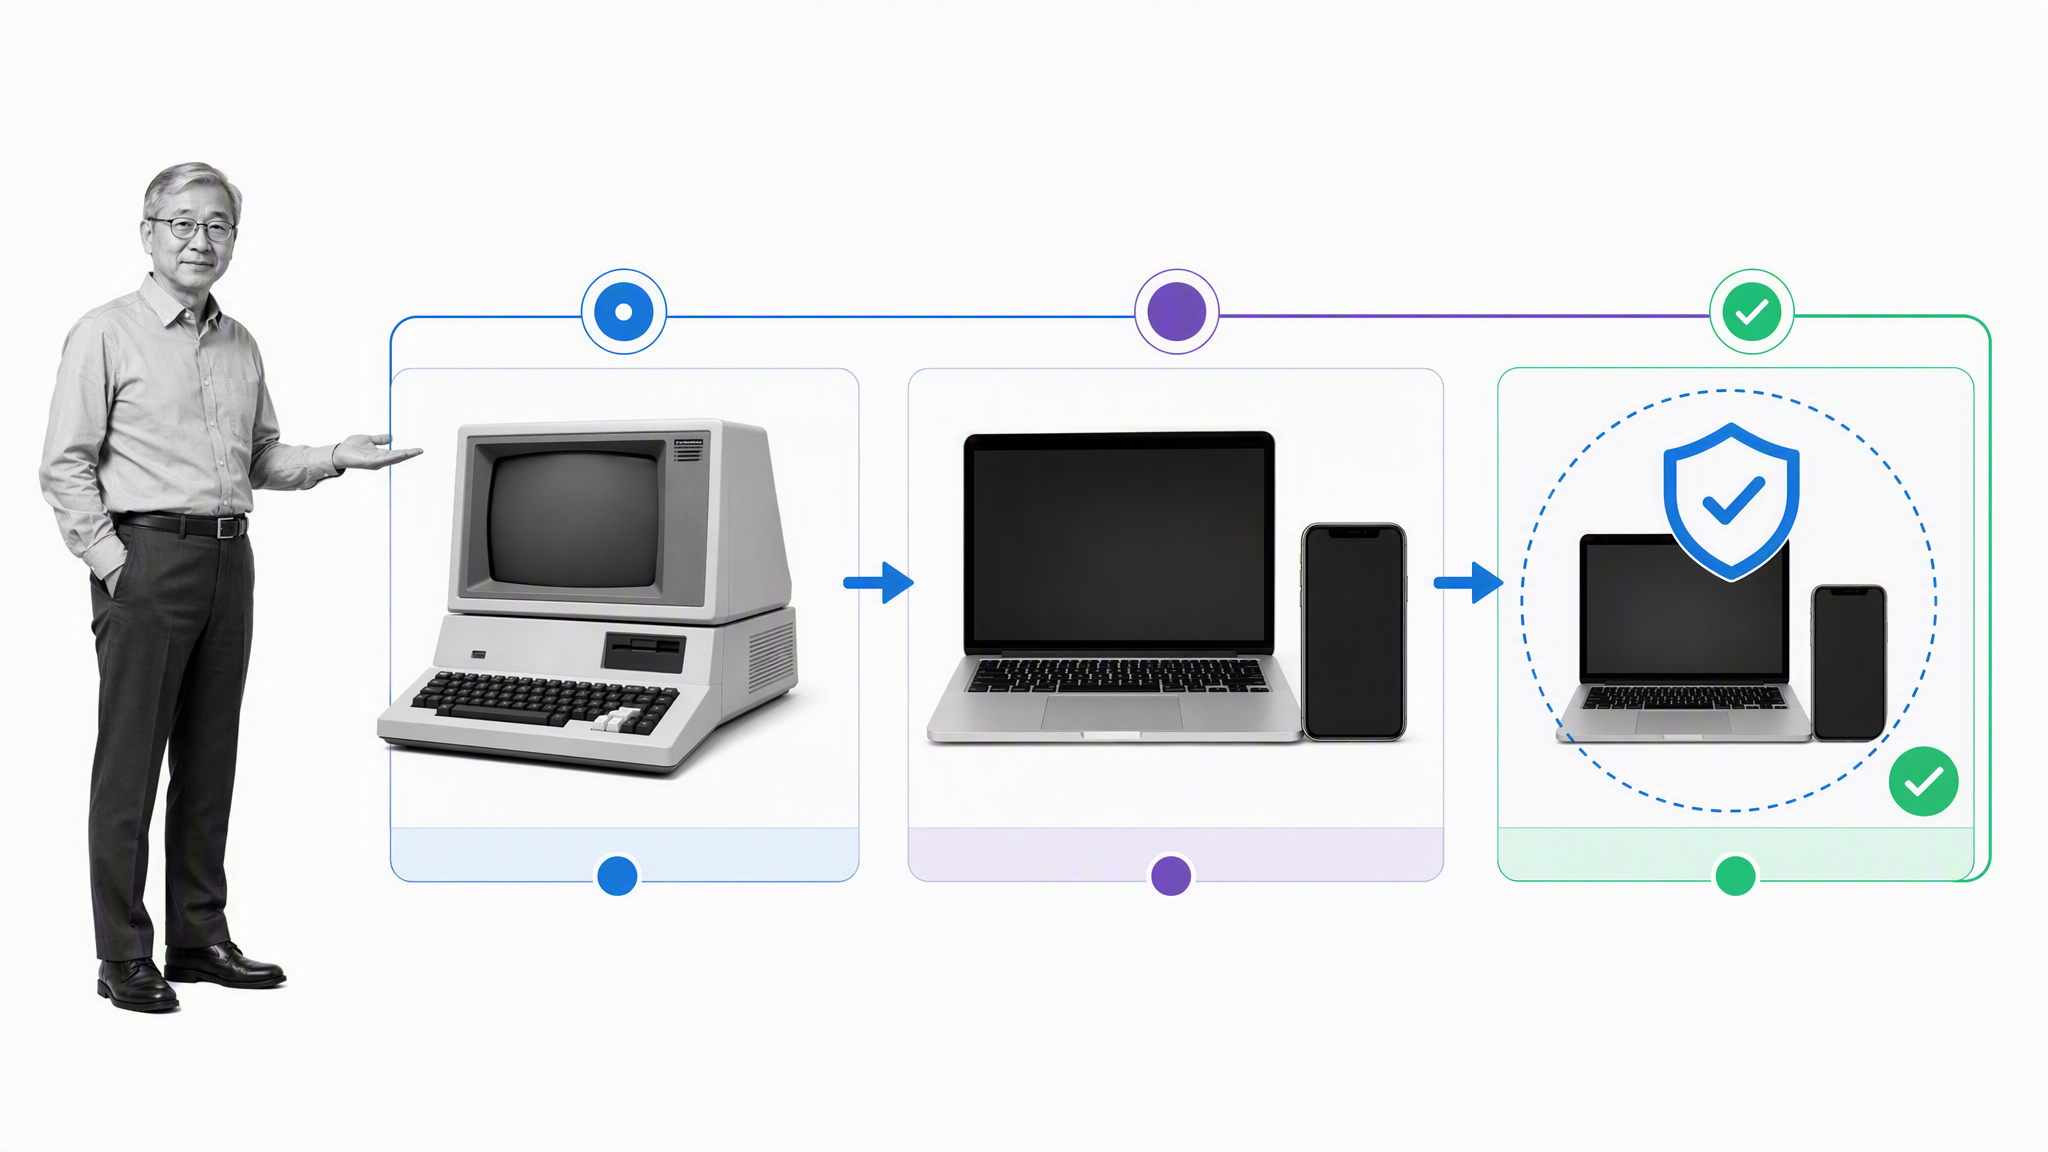
The need grew as work moved away from fixed office computers. The Apple II helped make personal computing useful to businesses, but it was still tied to a desk. Laptops, smartphones, and tablets made work portable. Employees could use familiar devices in meetings, at home, and while traveling. That flexibility also moved business data beyond a network perimeter that IT could physically observe.
The Apple II was one of the world’s most loved mass-produced computers. From homes to offices across the United States, these large machines were everywhere. For organizations, they were valuable for business efficiency even though their size meant they were by no means portable.
Technological advances soon condensed chunky computers into laptops that could be taken almost anywhere. Cellphone technology advanced too. Phones became handheld computers that were more accessible, powerful, and useful than earlier mobile phones. Tablets also became commonplace in offices and field work.
By the tail-end of the 2000s, many employees had an iPhone or a BlackBerry, a Windows laptop or a MacBook. Tablets started becoming lynchpins for forward-thinking organizations and increasingly became commonplace in the office. The device mix kept expanding from there.
Employees were no longer tethered to the computer waiting at a desk each morning. They could work from laptops, cellphones, and tablets inside or outside the office. That is when the bring-your-own-device movement truly changed how organizations approached mobility.
The history matters because the control problem changed. Securing one office workstation is different from governing a mixed fleet that changes networks, carries personal information, installs apps, and can disappear in a taxi or airport. EMM responds by managing the relationship between the person, device, app, identity, and data rather than relying on location alone.
Bring your own device (BYOD)
Bring your own device (BYOD) allows employees to use personally owned phones, tablets, or computers for work. It can improve flexibility and reduce the need to switch between unfamiliar devices. It also changes the risk and privacy model because one device now contains both personal and organizational activity.
NIST guidance for BYOD treats security and employee privacy as connected design requirements. An organization should be explicit about what it can inspect, which data it can remove, what happens when a device is lost, and how participation ends. Employees should not have to guess whether a control can reach personal photos, messages, or apps.
The negatives, such as losing devices and having data stolen, are exactly why EMM became integral for large and small organizations alike: it keeps potential security threats at bay while preserving the flexibility that made BYOD useful in the first place.
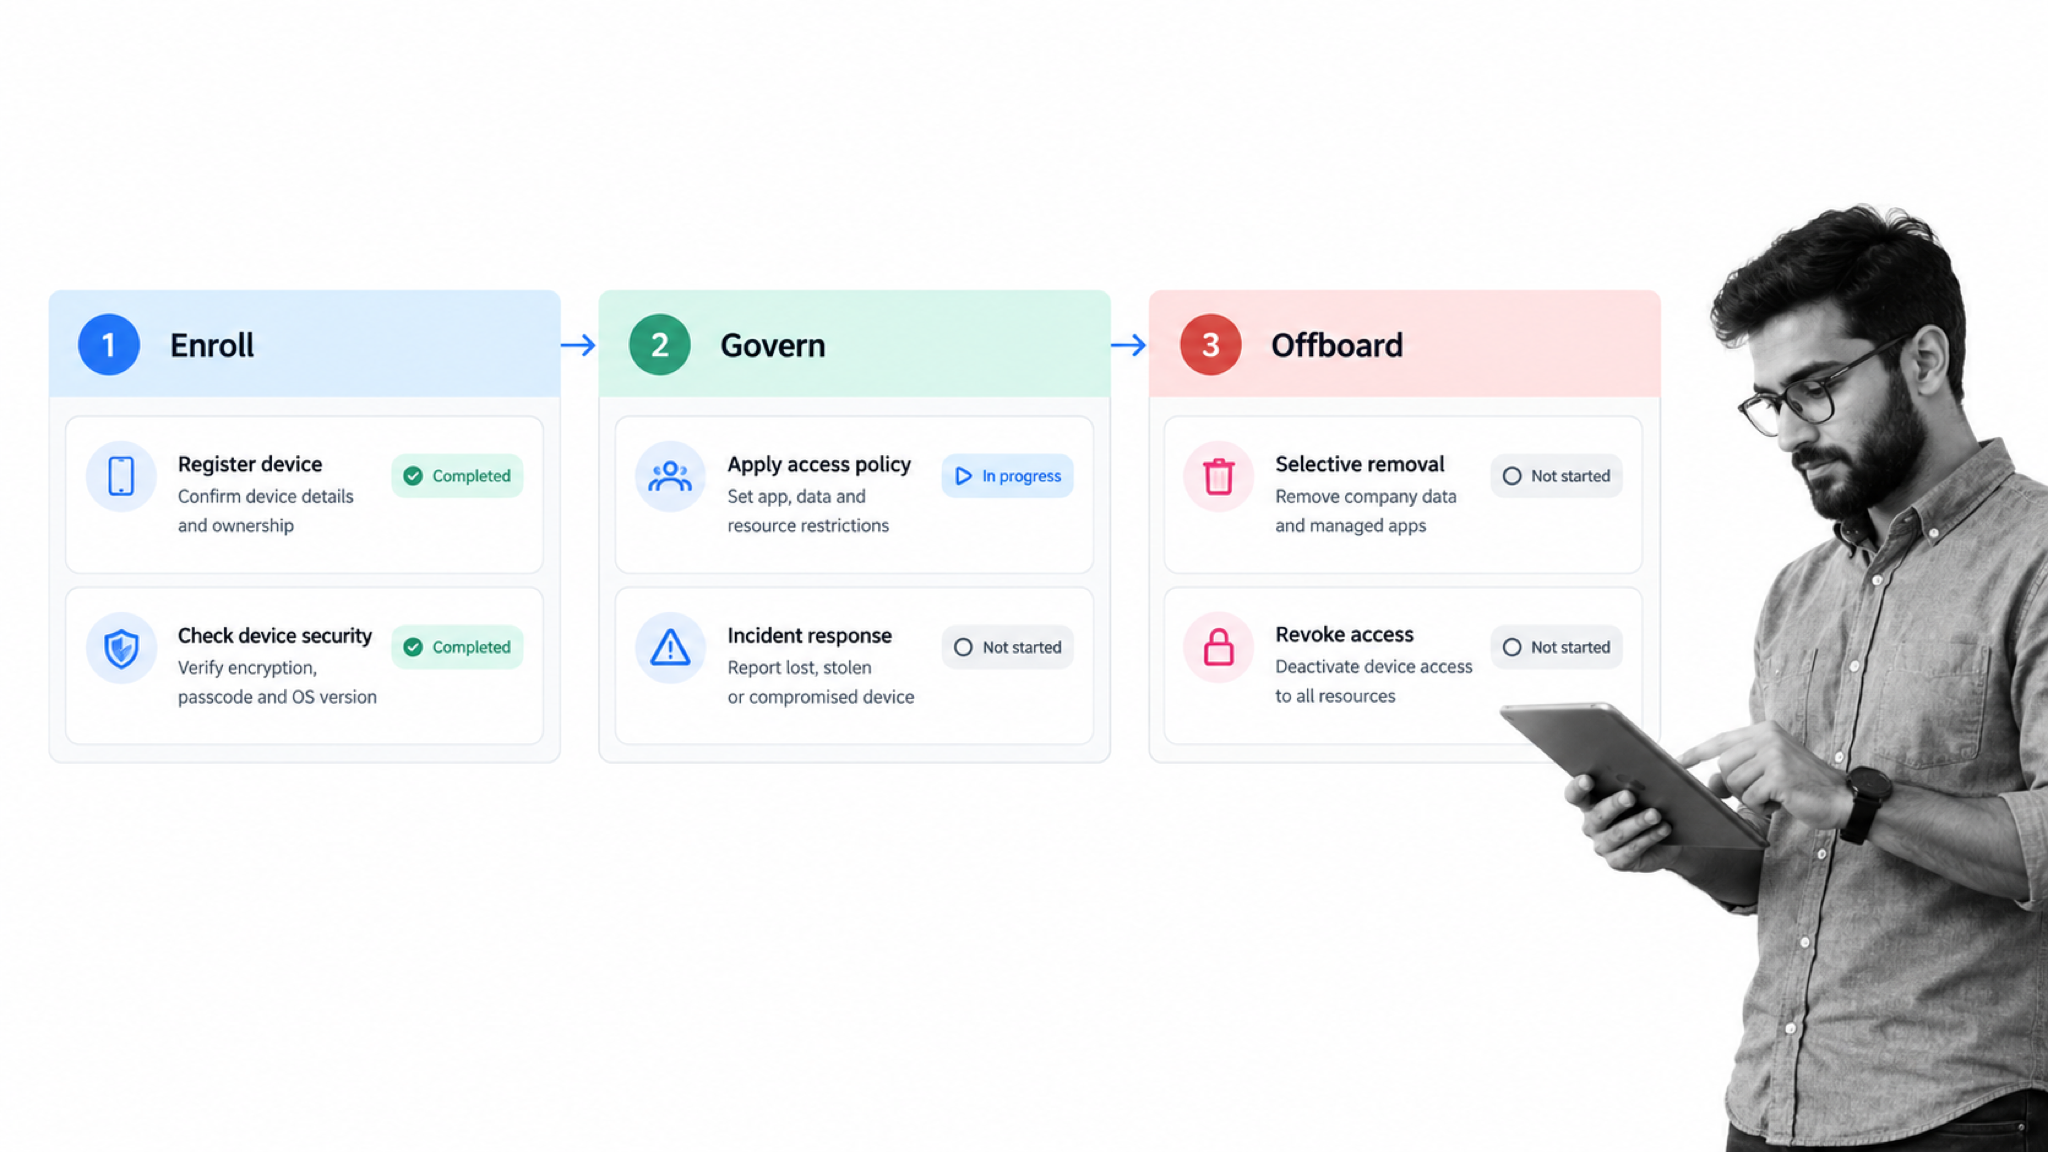
A BYOD lifecycle normally includes eligibility, informed enrollment, device posture checks, access assignment, monitoring, incident handling, selective removal of work data, and final deprovisioning. Treating enrollment as the whole program leaves the highest-risk moments, such as a lost phone or departing employee, without an owned response.
Device-level controls (MDM)
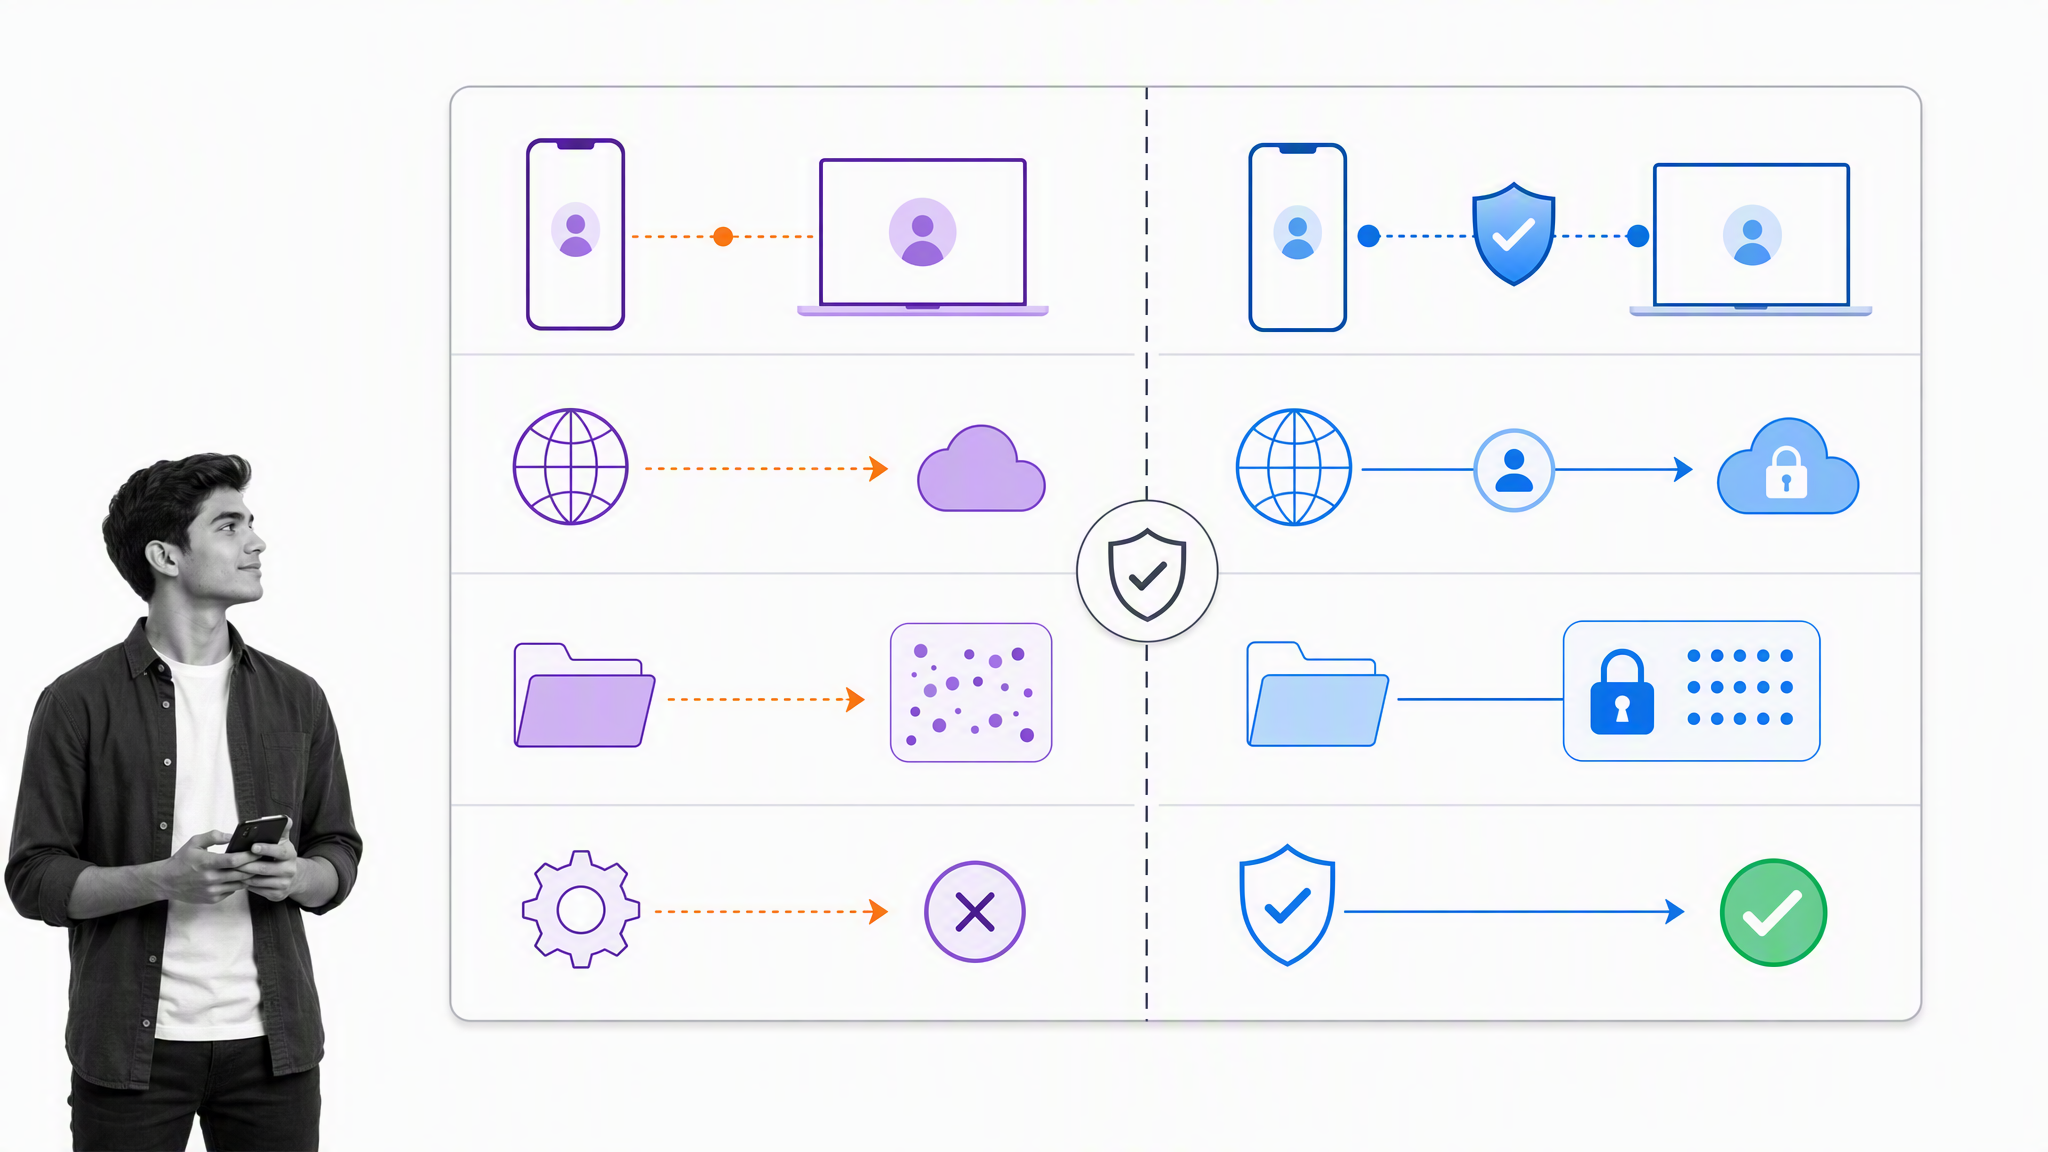
Mobile device management (MDM) manages the device itself. Depending on the platform and ownership model, MDM can configure security settings, require encryption and screen locks, install certificates, distribute network settings, check operating-system posture, inventory managed devices, and remotely lock or wipe corporate data.
What happens if an employee accidentally leaves a device on a train, in an airport lounge, or inside the plane itself? What happens if malware reaches the device or the device is corrupted? Those scenarios are why mobile device management became necessary. The IT team needs a controlled way to guard network access, secure the device, and respond before a missing endpoint becomes a larger incident.
An MDM service normally uses a management server and operating-system interfaces on the endpoint. Administrators configure policies through a management console, and the service applies those policies to enrolled devices. That gives employees a more secure way to send email, access documents, and use approved services while giving authorized administrators a way to lock the endpoint or remove organizational data.
With MDM, IT professionals provide employees with a more secure experience: employees can send emails, access documents, and search the web through managed connections and data encryption. At the same time, authorized administrators may have the power to wipe managed data from devices that are accidentally left on a flight from JFK to LHR.
Mobile device management relies on endpoint software called an MDM agent and an MDM server that may live in a data center or in the cloud. IT administrators configure policies through the MDM server’s management console, and the server pushes those policies over the air to the MDM agent on the device. The agent applies the policies by communicating with application programming interfaces built into the device operating system.
Microsoft’s Intune overview distinguishes enrolled-device management from app-level management. That distinction is important for BYOD. A company-owned phone may justify broad device controls, while a personal phone may call for a narrower boundary around work apps and data. The strongest policy is not automatically the most invasive one; it is the least intrusive control that meets the stated risk.
Application-level controls (MAM)
Mobile application management (MAM) controls work applications and the data they handle. MAM policies can require authentication, restrict copy and paste between work and personal contexts, prevent work files from opening in unmanaged apps, and remove corporate app data without erasing the employee’s personal content.
Mobile application management gives IT professionals the ability to control corporate applications and the data stored, transferred, or transmitted through those applications. It reaches deeper into the work context than device-only management because it focuses on the software and information on the device rather than only the hardware.
The practical difference is scope. MDM focuses on the employee’s device, while MAM focuses on the applications and software on that device. With device management, IT may be able to lock a phone. With application management, IT can remove access to corporate email or erase managed app data without making the employee’s personal data inaccessible.
Put another way: with MDM, IT is capable of wiping or locking an employee’s phone. With MAM, IT can lock the user out of corporate email without the employee worrying about personal data becoming inaccessible. The ownership model and risk should determine which level of control is appropriate.
That makes MAM especially useful when full device enrollment is unnecessary or inappropriate. Microsoft’s app-management documentation explains how application protection can separate organizational data from personal data. MAM does not eliminate every device risk, but it gives administrators a more proportionate control option.
EMM vs MDM vs UEM
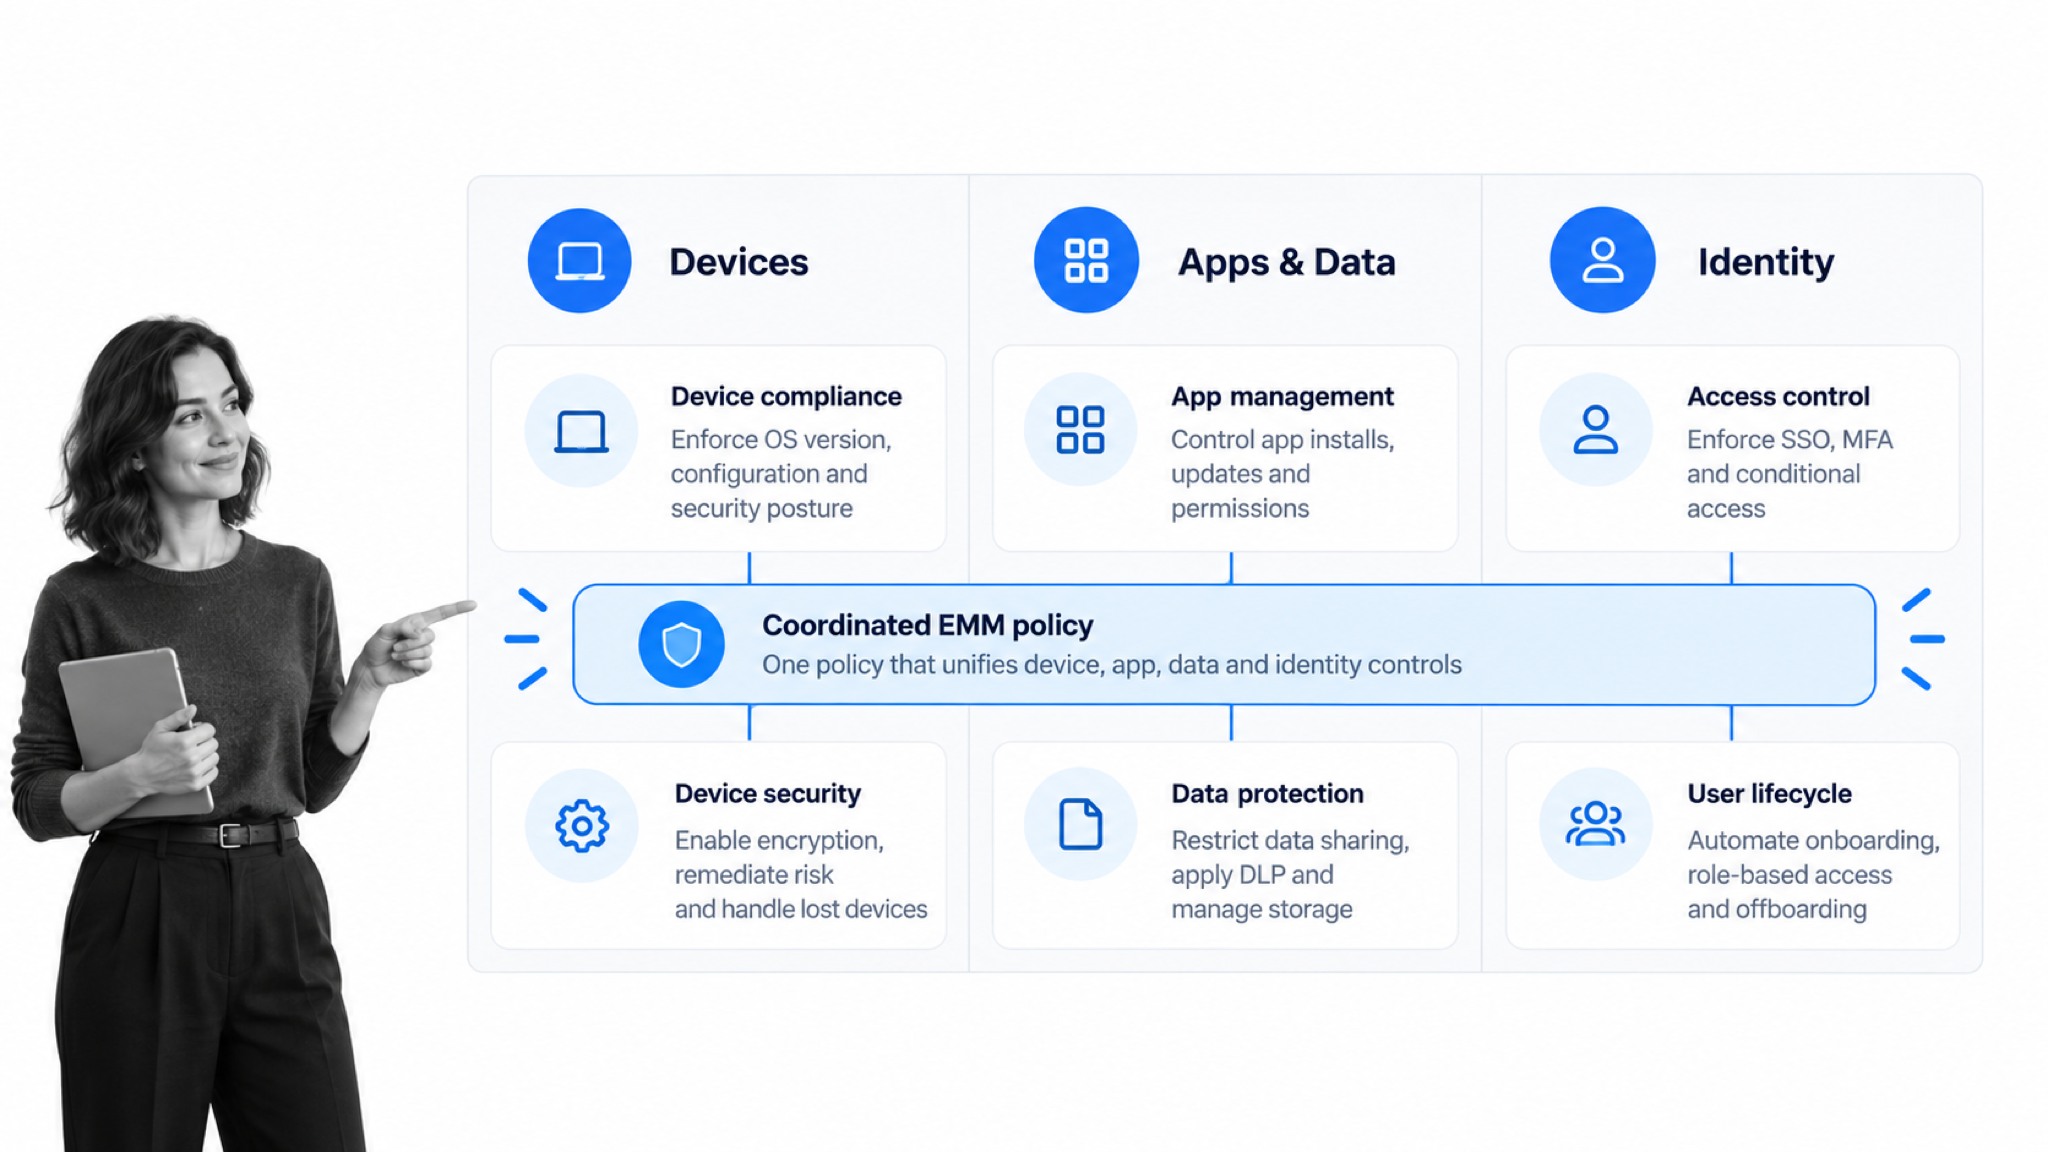
MDM is one control domain inside the broader EMM program. MAM adds application and data controls. Mobile content management and identity and access management may also sit inside the EMM design. In simple terms, MDM asks whether the device is managed; MAM asks how work apps and data behave; EMM coordinates the mobile program around both.
Unified endpoint management (UEM) extends that approach across more endpoint classes, such as laptops, desktops, rugged devices, and mobile endpoints, through a common administration model. Many current products use UEM language even when teams still search for EMM or MDM. The labels matter less than confirming that the chosen solution covers the organization’s actual devices, ownership models, applications, identities, and lifecycle events.
BYOD and the benefits of enterprise mobility management
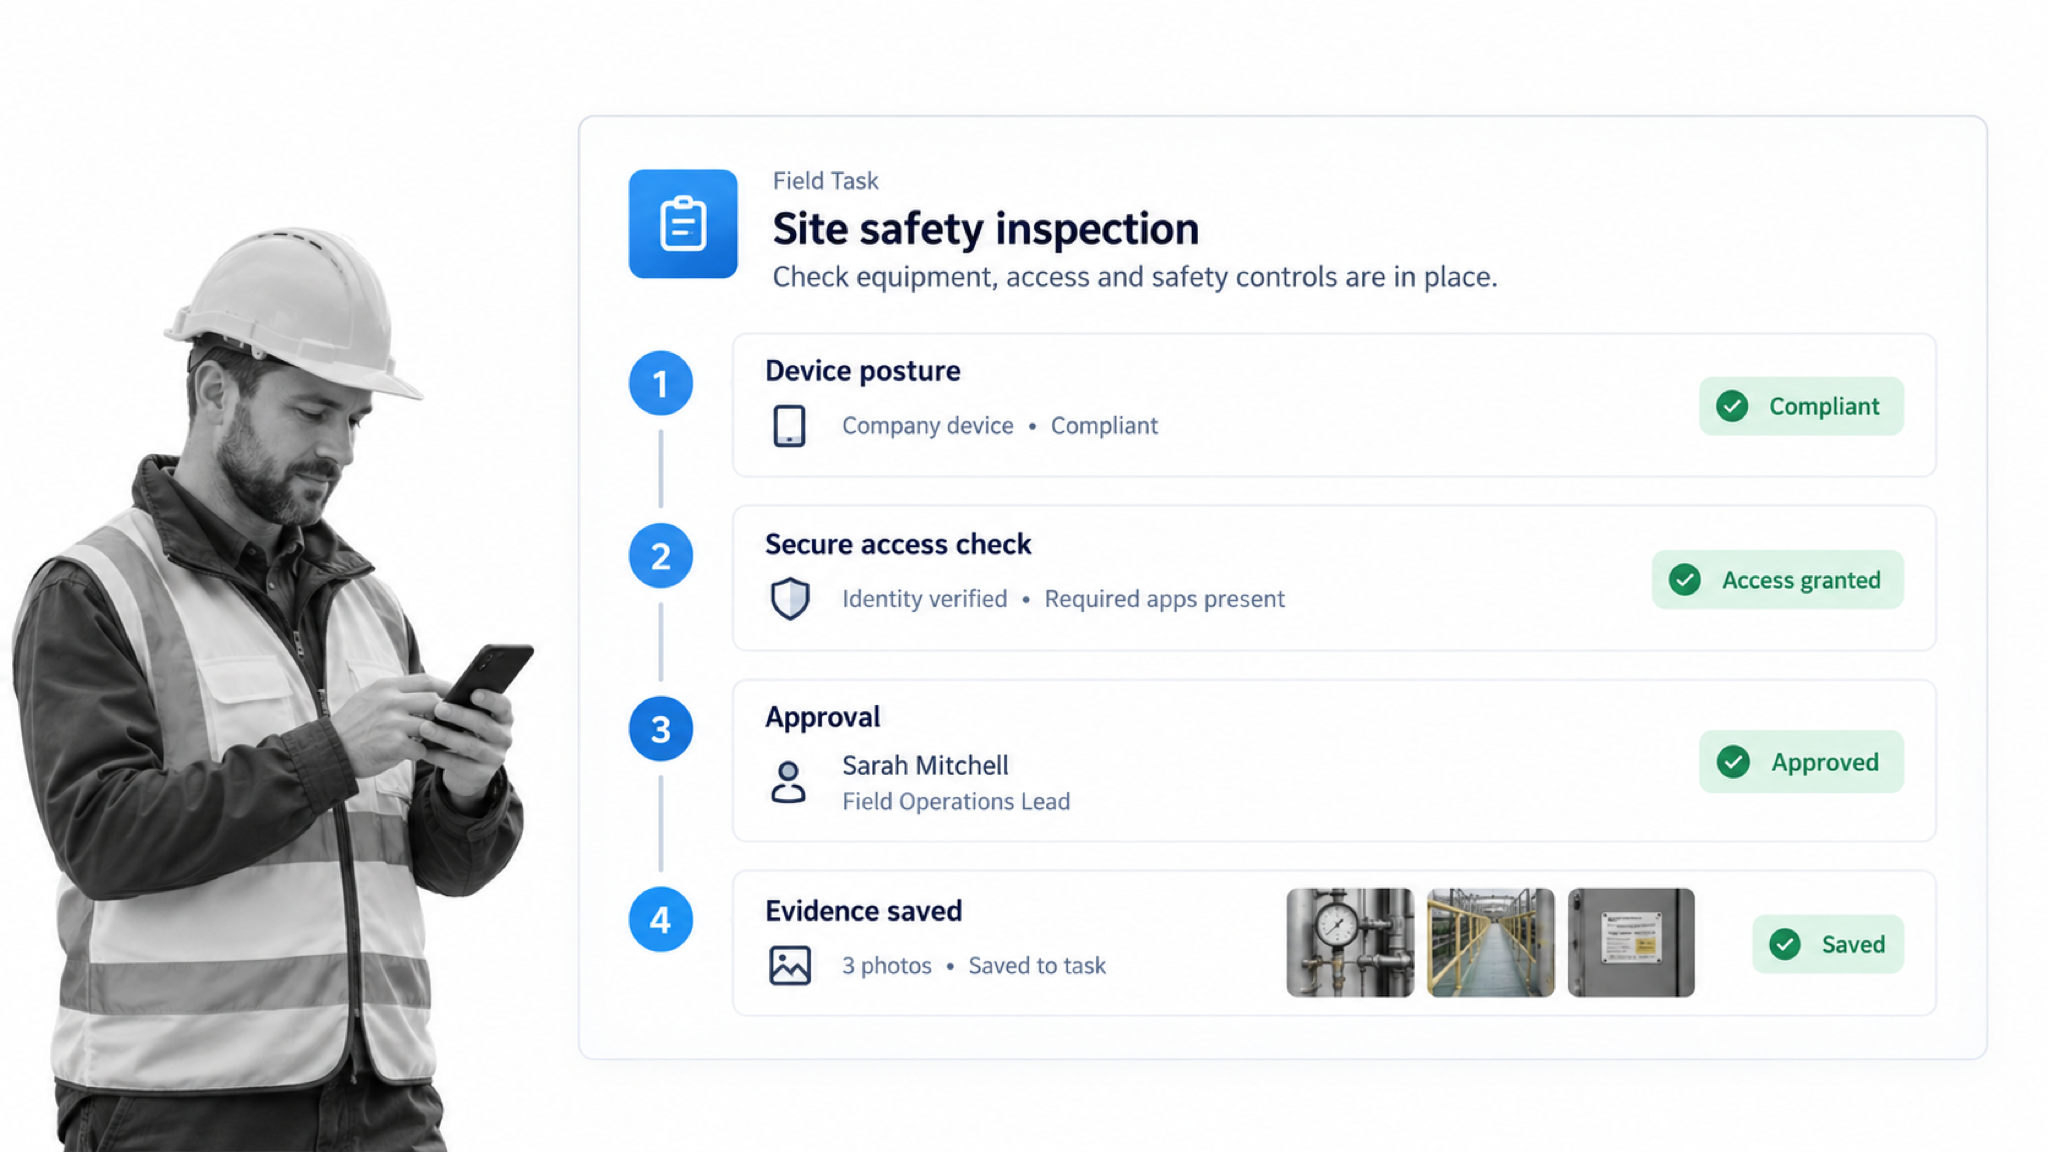
Mobile work creates value when employees can use the right device in the right place without creating an unmanaged path to sensitive information. BYOD and EMM address different halves of that outcome: BYOD provides flexibility, while EMM provides the controls and evidence that make the flexibility supportable.
The benefits of BYOD
- Increased productivity: Going back and forth between different devices creates friction. A person who knows the placement of every key, setting, and application can focus on the task instead of relearning the tool. Familiar phones and tablets can offer the same advantage when they are approved for work.
- Acknowledged as an employee perk: Thousands of employees believe that sticking to one device, whether company-bought or self-bought, is a useful perk. Some prefer one familiar device; others value the flexibility that BYOD entails. For them, a clear BYOD culture is an attractive quality rather than a deterrent.
- Potentially lower company spend: Not having to buy an extra device for every eligible employee can lower hardware spend. That saving should be evaluated beside support, security, reimbursement, privacy, and administration costs.
- Work can be completed in more places: Even in an office-based organization, not all approved work happens inside the office. Employees may check email before a meeting, review a project at home, or respond during a commute. With the right controls, BYOD lets employees work from wherever the role and policy allow.
There is nothing worse than going back and forth between different devices. Take me as an example. I am so used to my own laptop’s keyboard that trying to type on another keyboard feels like learning to type again. It slows the writing process because I have to think consciously about the placement of my hands. Using a familiar device removes that friction. The same benefit can apply when employees use familiar phones and tablets for approved work.
Many employees also see the ability to stay with one device as a perk. They may value the familiarity, accessibility, or flexibility that comes with it. Work is not always done inside the office: people check email before meetings, finish a task at home, or respond during a commute. A workable BYOD policy makes that flexibility deliberate rather than accidental.
Those benefits are not a reason to permit unrestricted access. They are a reason to design a clear mobile operating model. If the employee experience is so restrictive that people invent workarounds, the organization has exchanged a visible policy problem for an invisible security problem.
The benefits of EMM
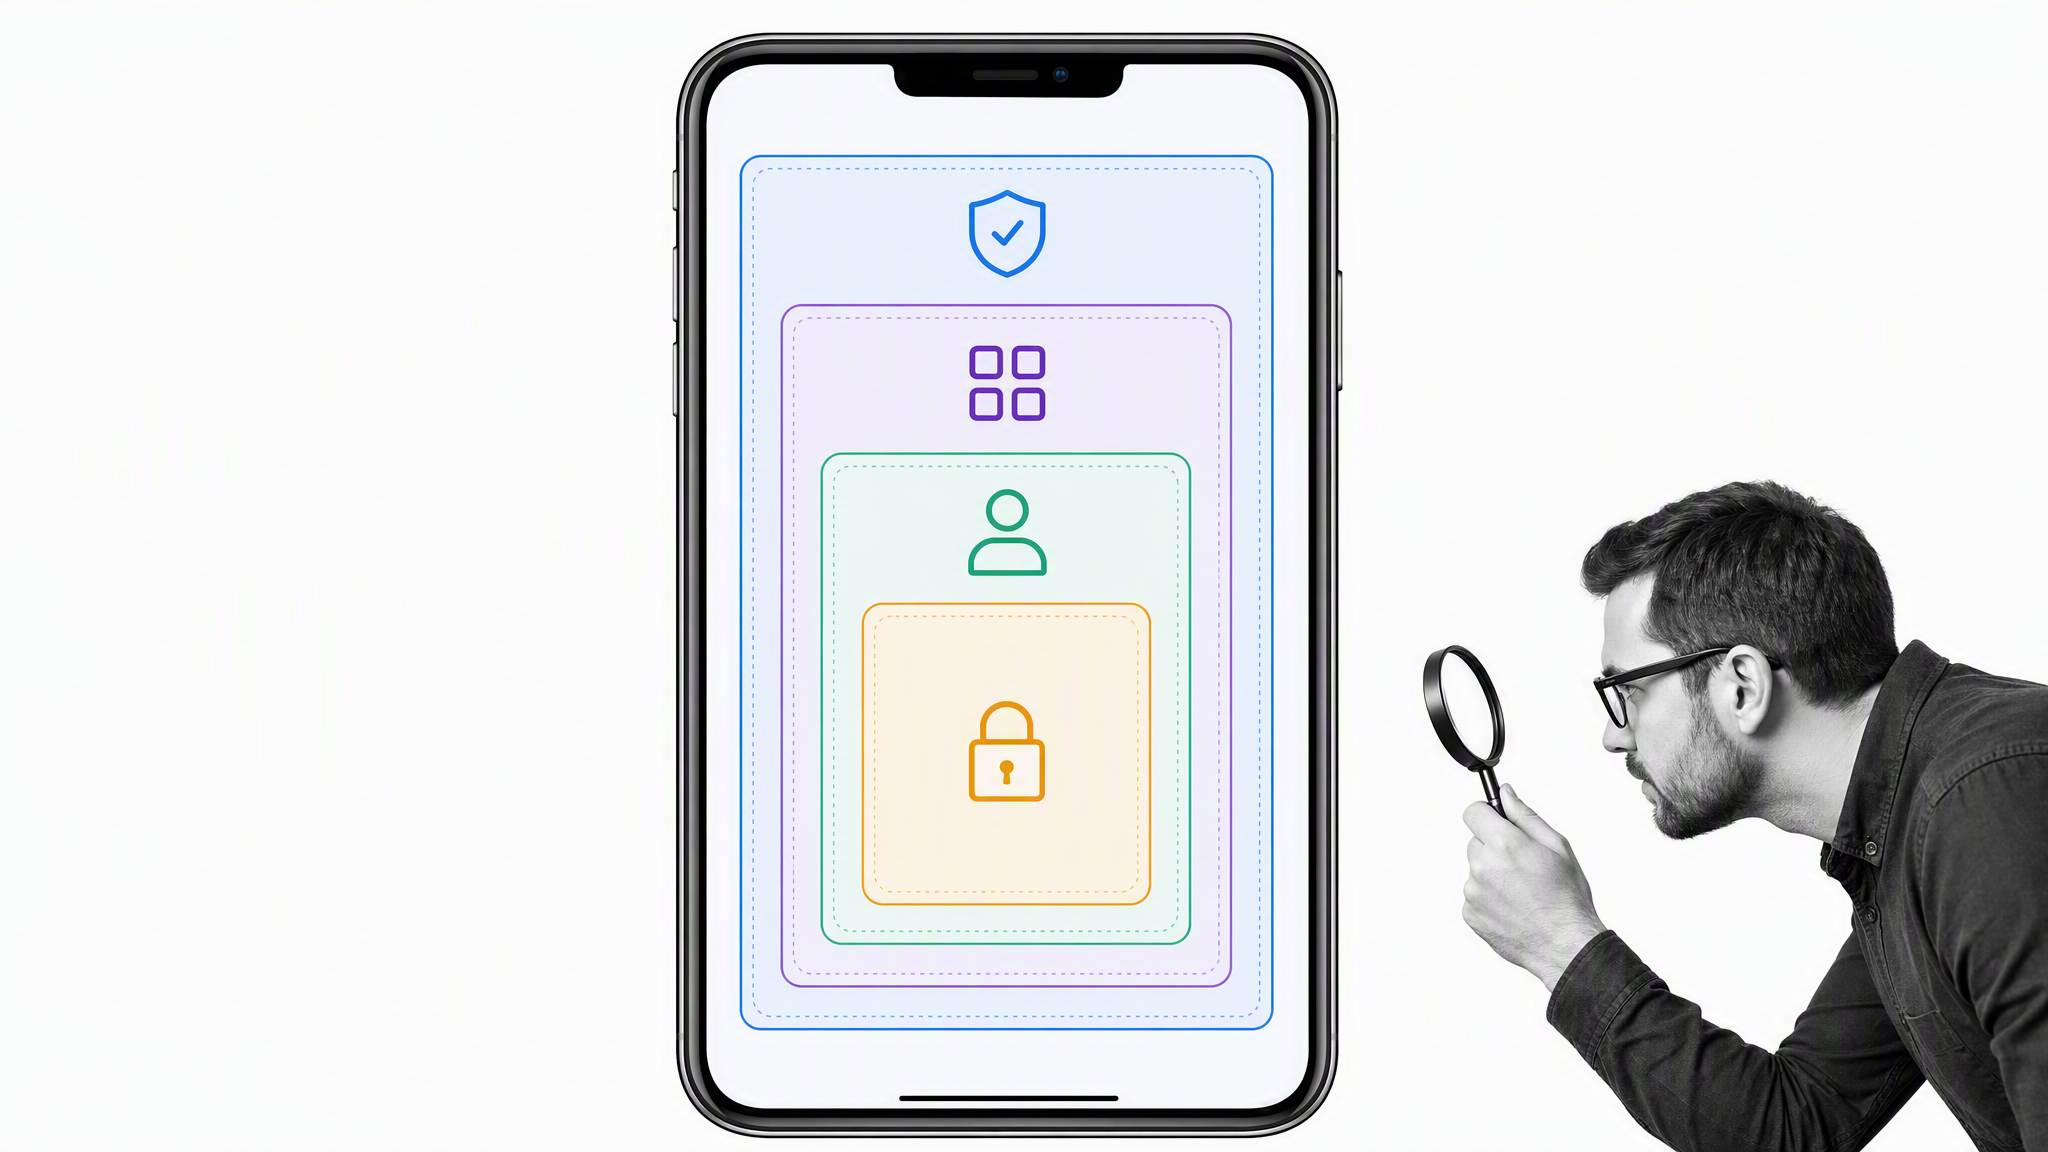
- Protects employees’ data: Whether an employee is in the office or on the road, personal and work information can be compromised in many ways. EMM helps keep workforce data inside defined access, application, and storage boundaries.
- Protects the organization’s data: Corporate data should not be available to an unapproved person or application. Device enrollment, authentication, application and website controls, encryption, and selective wipe can reduce that exposure.
- Can wipe or remove organizational data: Data wiping has been mentioned several times for a reason. It is a prominent EMM capability because mobile devices can be lost. A proportionate response may erase managed work data, lock a company-owned endpoint, or revoke access.
- Supports different kinds of devices: A suitable solution should cover the actual mix of operating systems and device types in the organization. Verify the supported Windows, Mac, Android, and iOS versions plus shared, rugged, and personally owned devices.
- Helps with compliance: EMM can apply security controls and preserve evidence for obligations such as HIPAA or GDPR where they apply. The product supports the program; it does not guarantee legal compliance.
- Provides peace of mind: Employees can understand how to use devices safely, and administrators have a defined response if a device goes missing. The program turns a worrying event into an owned sequence of actions.
The most visible EMM benefit is the ability to protect employees’ data and the organization’s data across different kinds of devices. When an employee is in the office or on the road, information can be compromised in many ways. Device enrollment, device authentication, application controls, website allowlists and blocklists, encryption, and selective data wiping help keep workforce and corporate data where it should be.
Data wiping and erasing are prominent EMM capabilities for a reason. Mobile devices are mobile, which means they are also easy to lose. If a managed device goes missing, an authorized response may erase organizational data, revoke access, or lock the device. The action should not depend on someone remembering informal steps. The organization needs to know which data can be removed, who can authorize the action, what evidence should be captured, and how to confirm that access is no longer available.
Enterprise mobility management solutions can support different device brands and operating systems, but coverage should be verified rather than assumed. The fleet may include Windows and Mac computers plus Android and iOS phones and tablets. Every supported combination needs a tested enrollment, policy, incident, and retirement path. Unsupported combinations need an explicit decision instead of silent access.
EMM can also help with compliance by enforcing safeguards and producing evidence. It does not create compliance automatically. The organization remains responsible for choosing controls that fit its legal, contractual, and risk context, reviewing how they operate, and correcting failures.
Finally, a well-operated EMM program provides peace of mind. Employees can use approved devices with a clear understanding of the boundary, and administrators have a defined response if a device goes walkabout. A lost endpoint should trigger a controlled workflow, not become the end of the world.
EMM supports compliance work, but it does not make an organization compliant by itself. For regulated health information, the official HIPAA Security Rule in the eCFR sets out the safeguards expected of covered entities and business associates. In the European Union, data protection duties depend on the processing context and applicable law; the European Commission’s data-protection overview is a better starting point than a blanket claim that one tool guarantees GDPR compliance.
Enterprise mobility management best practices
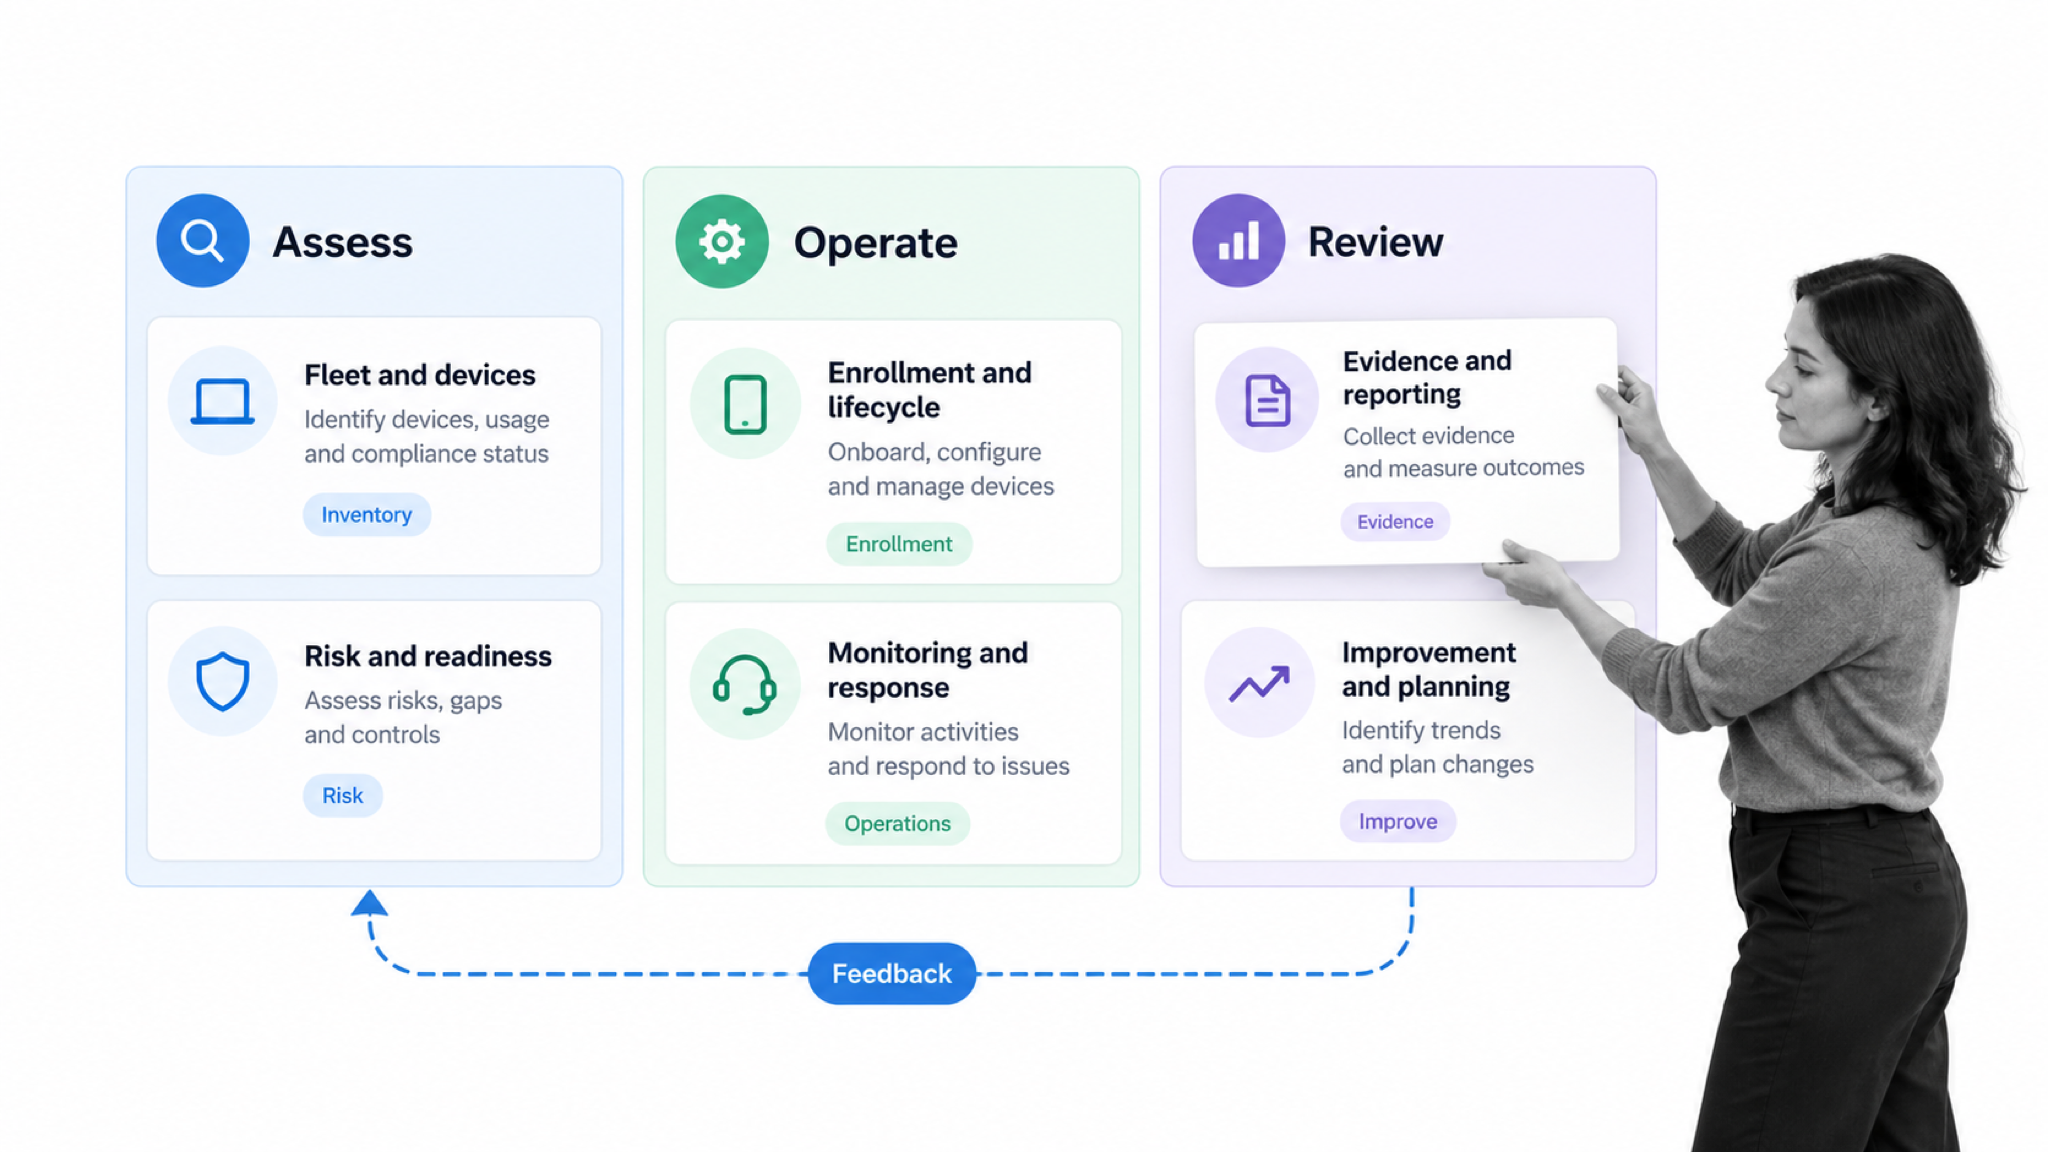
NIST Special Publication 800-124 Revision 2 frames mobile-device security across the deployment lifecycle. That lifecycle view is the most useful organizing principle for an EMM program: assess, select controls, configure, deploy, monitor, respond, review, and retire.
Introducing a new business system and an EMM solution can go either way. On one side, it can streamline mobile security, protect essential information, and create peace of mind for the IT team, employees, and leadership. On the other, it can confuse administrators and employees if the product, policies, and procedures are not well considered. Successful implementation connects the technology to understandable decisions and owned routines.
Understand your organization’s needs
First things first: it is pivotal to understand your organization’s own needs. Everything required for understanding, implementing, and sustaining EMM should flow from that operating context.
Start with users, data, devices, and decisions. Inventory mobile use by role and ownership model. Identify the data employees need, the applications that process it, the identity systems involved, and the consequences of a compromised or unavailable device. A field technician using a shared rugged tablet needs a different design from an executive accessing email on a personal phone.
There are no hard-and-fast rules for how every organization should manage enterprise mobility. What works for one organization may not work for another. One company might need a narrow set of lock and selective-wipe capabilities, while another may need the wider capabilities of an EMM or UEM platform. Understanding the organization’s own requirements makes it possible to choose a solution that fits instead of buying the broadest feature list.
- Ownership: Which devices are corporate-owned, personally owned, shared, or dedicated?
- Platforms: Which operating systems and minimum versions must be supported?
- Access: Which apps and data should each role reach, and under what conditions?
- Privacy: What device information is necessary, who can see it, and how will employees be informed?
- Response: Who acts when a device is lost, out of compliance, or suspected of compromise?
Five useful evaluation questions are: What management solutions do I need in my EMM suite? Can I upgrade my existing MDM solution? What operating systems does the EMM solution support? How does the EMM solution help maintain security? Does the enterprise want a SaaS or on-premise deployment? The answers turn a broad product search into a requirements brief.
Evaluate enterprise mobility management solutions
Translate those needs into testable requirements before comparing vendors. Check platform coverage, identity integrations, zero-touch enrollment, app protection, conditional access, selective wipe, certificate management, reporting, audit logs, shared-device support, exception handling, and offboarding. Test the highest-risk workflows with real device types instead of relying on a feature checklist.
Considering the sheer number of EMM solutions on the digital marketplace, administrators have their work cut out for them. A consistent decision process keeps the evaluation grounded.
The number of enterprise mobility management solutions on the market can make evaluation feel like a large task. A decision framework makes it easier to compare options against the same criteria, narrow the choices, and explain the final decision. That saves time, reduces stress, and keeps a persuasive demonstration from outweighing the organization’s actual requirements.
Use the DECIDE framework from this decision-making process: define the problem, establish criteria, consider alternatives, identify the best alternative, develop and implement the plan, then evaluate the result. The six-step framework helps whittle software choices down to the final contender and can save time, effort, and a whole lot of stress. If administrators must support devices outside the office, include secure remote management tools and access boundaries in the evaluation rather than adding them after deployment.
Write policies around realistic use cases
Policies should describe outcomes and decisions, not just settings. Cover enrollment, acceptable use, authentication, operating-system support, app installation, data transfer, backup, travel, lost devices, suspected compromise, employee departure, and disposal. Each rule needs an owner, an enforcement mechanism, an exception path, and a clear employee-facing explanation.
Policies are sets of rules that allow or disallow device functions and configure access settings. They may disable a sensitive function, configure an email account or VPN, require a screen lock, or restrict how managed data moves. The point is to translate a risk decision into a control employees and administrators can understand.
A policy can allow or disallow device functions, such as disabling screenshots in a sensitive app. Policies are also used to configure settings such as email accounts and VPN access. The control should be specific enough to enforce and plain enough for an employee to follow.
Balance security with workability. Blocking screenshots may be justified for one application but unnecessary across an entire personal device. A full wipe may be appropriate for a company-owned phone and disproportionate for a BYOD device when selective removal will protect the same business data. Write these distinctions down before an incident forces a rushed choice.
Policies should not create a bottleneck that blocks employees from completing legitimate work. At the same time, they must protect the people and data on those devices. The middle ground is a policy aligned to realistic use cases, with a documented exception route when the normal control does not fit.
Align controls with applicable law and contracts
The next policy-level step is to ensure whatever policies are created are law-abiding. Before informing employees why a product is being introduced, how to use it, and which policies apply, confirm that those policies align with applicable laws in the locations where the organization operates.
Map each control to the data and obligation it supports. Consider privacy notices, labor requirements, records retention, breach response, customer contracts, and sector-specific safeguards. Legal applicability varies by organization and jurisdiction, so security and legal owners should review the program together. Avoid collecting device data merely because the platform can collect it.
Review the program continuously
Continually review how the organization goes about EMM. Similar to regular performance appraisals and operational reviews, enterprise mobility management needs a recurring review cadence.
EMM is not a one-time rollout. Review platform changes, operating-system support, inactive enrollments, exception age, incident patterns, employee feedback, and control failures on a defined cadence. Track whether actions closed, not just whether a meeting happened. A recurring review should end with owners, due dates, and evidence.
Frequent reviews confirm that the EMM solution is working, that employees use it properly, and that the organization can improve its tools, policies, or training. A regular review can expose unnecessary restrictions, unsupported devices, recurring exceptions, or gaps in how new employees learn the mobile-security rules. Do not let avoidable security issues slip through the cracks.
Use incident exercises to test the operating path. Ask what happens when a phone is left on a train, when an employee changes roles, when a certificate expires, or when an unmanaged app receives a work file. The original lost-device scenario remains valuable because it forces the organization to connect policy, technology, human judgment, and communication.
Coordinate EMM policy and operations with Process Street
Process Street does not replace an EMM or UEM platform. It coordinates the governed work around that platform. Security teams can document control standards and employee guidance, run enrollment and offboarding workflows, route exceptions, collect evidence, and prove that recurring reviews and incident actions were completed.
How Process Street supports enterprise mobility operations
Process Street is one Compliance Operations Platform with Docs and Ops capability areas plus built-in AI. Docs can hold controlled mobile-security policies, ownership rules, decision criteria, and response guidance. Ops can turn those controls into assigned workflows with approvals, due dates, conditional paths, forms, evidence, and audit history. Built-in AI can help summarize approved evidence or route work inside those controls while people retain approval authority.
Workflow features such as conditional logic, task permissions, dynamic due dates, role assignments, and approvals let a mobile-security workflow adapt to the device, ownership model, risk, and requested action. The same controlled run can remain simple for the employee while exposing the necessary evidence and decisions to administrators.
The operating layer matters because an EMM console can enforce settings but cannot own every cross-functional decision. Lost-device response may involve IT, security, legal, a manager, and the employee. A policy exception may require risk acceptance and an expiration date. Offboarding may require HR timing, identity revocation, selective wipe, asset recovery, and evidence retention.
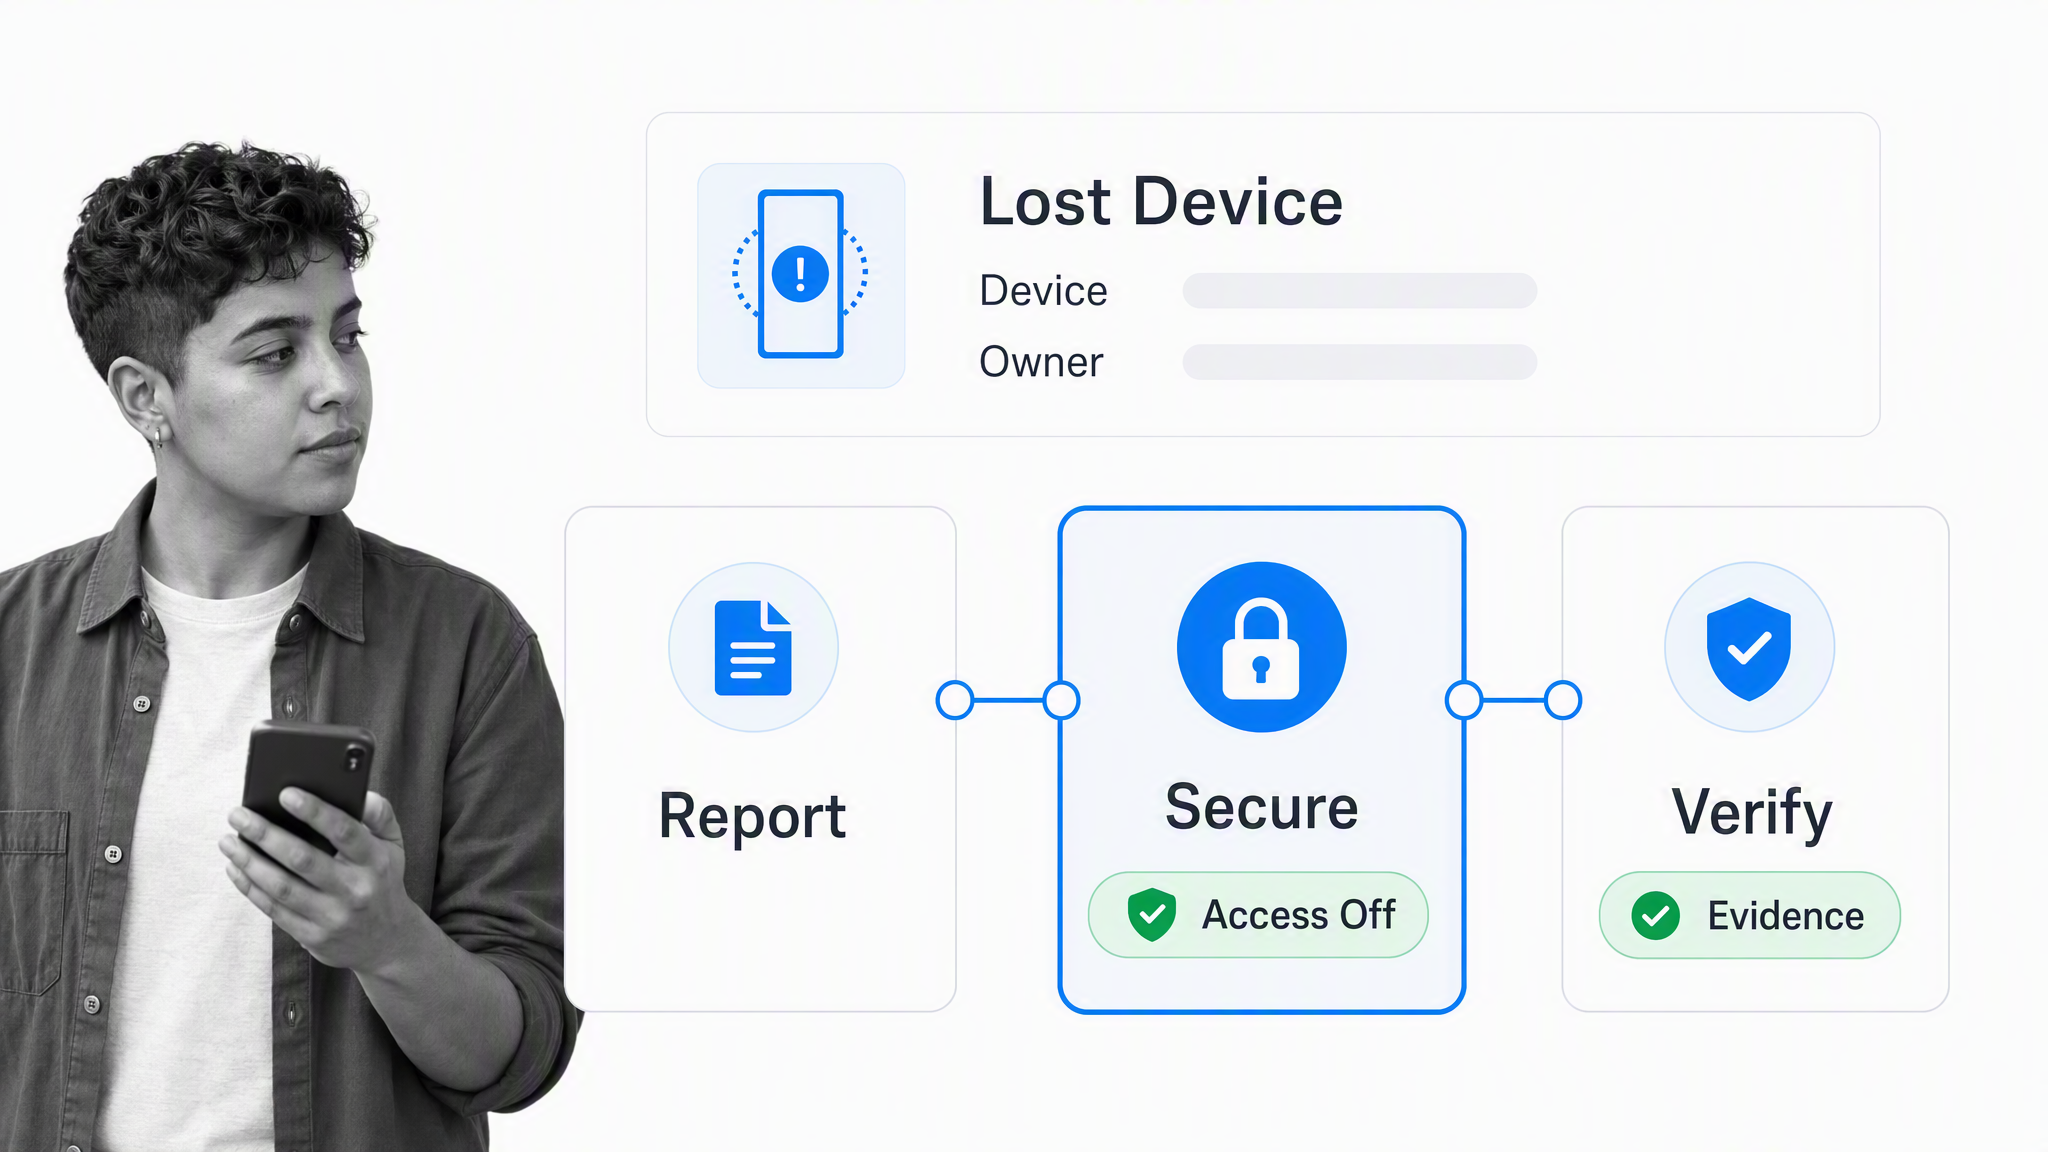
A lost-device workflow can capture the device and owner, suspend access, initiate the correct lock or wipe action, record the decision, assess notification duties, verify recovery or retirement, and schedule follow-up. Conditional logic can distinguish company-owned and personal devices so the response uses the correct privacy boundary. Approvals can reserve destructive actions for authorized roles.
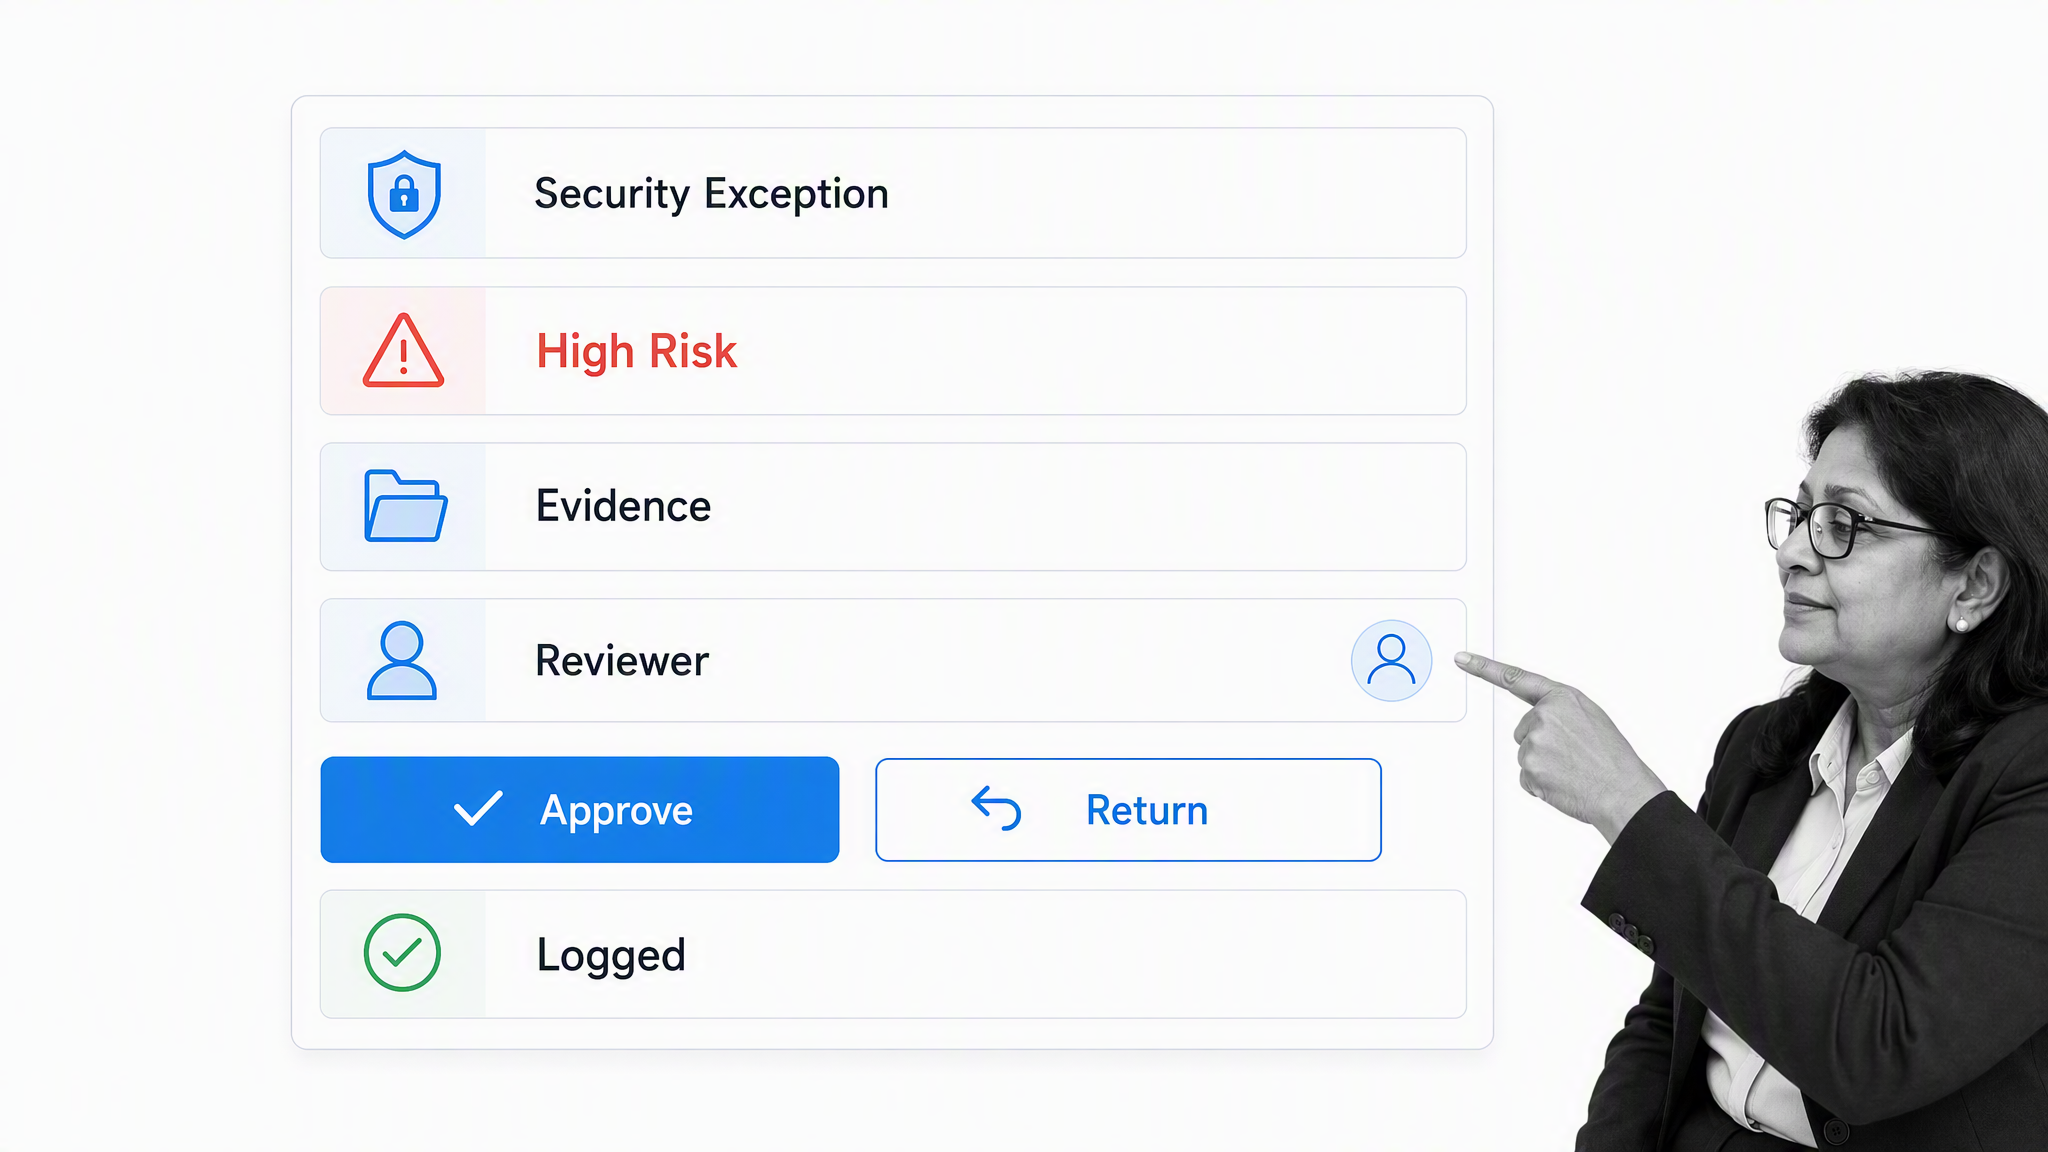
An exception workflow can require a business reason, affected device and data, risk owner, compensating control, approval, expiration date, and review task. That turns an informal chat into a time-bound decision with accountability. The same pattern works for unsupported operating systems, travel exceptions, temporary access, or a device needed for a specialized field application.
Other useful workflows include enrollment readiness, new-hire mobile access, certificate renewal, inactive-device review, quarterly policy review, employee feedback, and offboarding. The goal is not more process for its own sake. It is a reliable handoff between technical controls and the people responsible for operating them.
Additional security resources
Additional resources can bolster the organization’s security beyond the mobile program. Teams responsible for data, device, and network security management often need connected routines for identity, network configuration, server hardening, audit work, and testing.
The privileged password management template below can support one part of a wider security program. The same library includes network administrator daily tasks, network security audits, firewall audits, VPN configuration, Apache server setup, email server security, and penetration testing workflows.
A mature enterprise mobility strategy joins those supporting controls to one lifecycle: enroll only what is needed, grant proportionate access, monitor meaningful conditions, respond through owned workflows, remove access cleanly, and improve the system with evidence.
Enterprise mobility management FAQ
What is enterprise mobility management?
Enterprise mobility management is the combination of technology, policies, and processes used to secure and manage mobile devices, applications, identities, and business data across the endpoint lifecycle.
What is the difference between EMM and MDM?
MDM focuses on managing device configuration and posture. EMM is broader: it coordinates device management with application protection, content, identity, data handling, employee privacy, incident response, and governance.
Is EMM the same as UEM?
Not exactly. EMM grew around mobile endpoints. UEM extends centralized management across mobile devices, laptops, desktops, and other endpoint classes. Many modern products use UEM language while still providing the mobile controls associated with EMM.
What should an EMM policy include?
An EMM policy should cover ownership models, eligibility, enrollment, authentication, approved apps, data transfer, privacy, monitoring, travel, lost devices, suspected compromise, exceptions, offboarding, retirement, owners, and review cadence.